Ruby2ßhell runs code on stock Rails before login, and a JVM fix waited two months
4 hours ago
A one-byte overflow in Ruby's case conversion lets anyone run code on a stock Rails app without logging in, and the fix is a Ruby upgrade. Also from Thursday's Hacker News front page: a JVM Base64 fix that waited two months to merge, PHP 8.6, and Zerodha's blob store on SQLite. Ruby2ßhell: Pre-authentication RCE on stock Rails, by Veria Labs https://verialabs.com/ruby2shell/ Discussion: https://news.ycombinator.com/item?id=50556287 Multiple vulnerabilities in Regexp and String case conversion, the Ruby security advisory https://www.ruby-lang.org/en/news/2026/11/18/multiple-vulnerabilities-in-regexp-and-string/ Discussion: https://news.ycombinator.com/item?id=50554038 Someone reported java4shell bug in September 2026 (OpenJDK pull request 32781) https://github.com/openjdk/jdk/pull/32781 Discussion: https://news.ycombinator.com/item?id=50558906 black3r on Oracle asking the author to hold the fix: https://news.ycombinator.com/item?id=50562104 The Adoptium issue it quotes: https://github.com/adoptium/adoptium-support/issues/1480 What's New in PHP 8.6 https://www.php.net/releases/8.6/en.php Discussion: https://news.ycombinator.com/item?id=50557870 williamdclt on partial function application: https://news.ycombinator.com/item?id=50560160 Distributed, high-performance blob storage on SQLite, by Sarat Chandra at Zerodha https://zerodha.tech/blog/high-performance-distributed-blob-storage/ Discussion: https://news.ycombinator.com/item?id=50557537 CyrusGrissom on replication: https://news.ycombinator.com/item?id=50558304
Links
Ask about this presentation
Chapters
Show transcriptHide transcript
On Thursday's HN front page, a bug in how Ruby changes the case of text lets a stranger run their own code on a stock Rails app, with no account. It has been in Ruby since version 2.4. Also on the page: a Java crash fix that waited two months to merge, PHP 8.6, and a stockbroker's blob store built on SQLite.
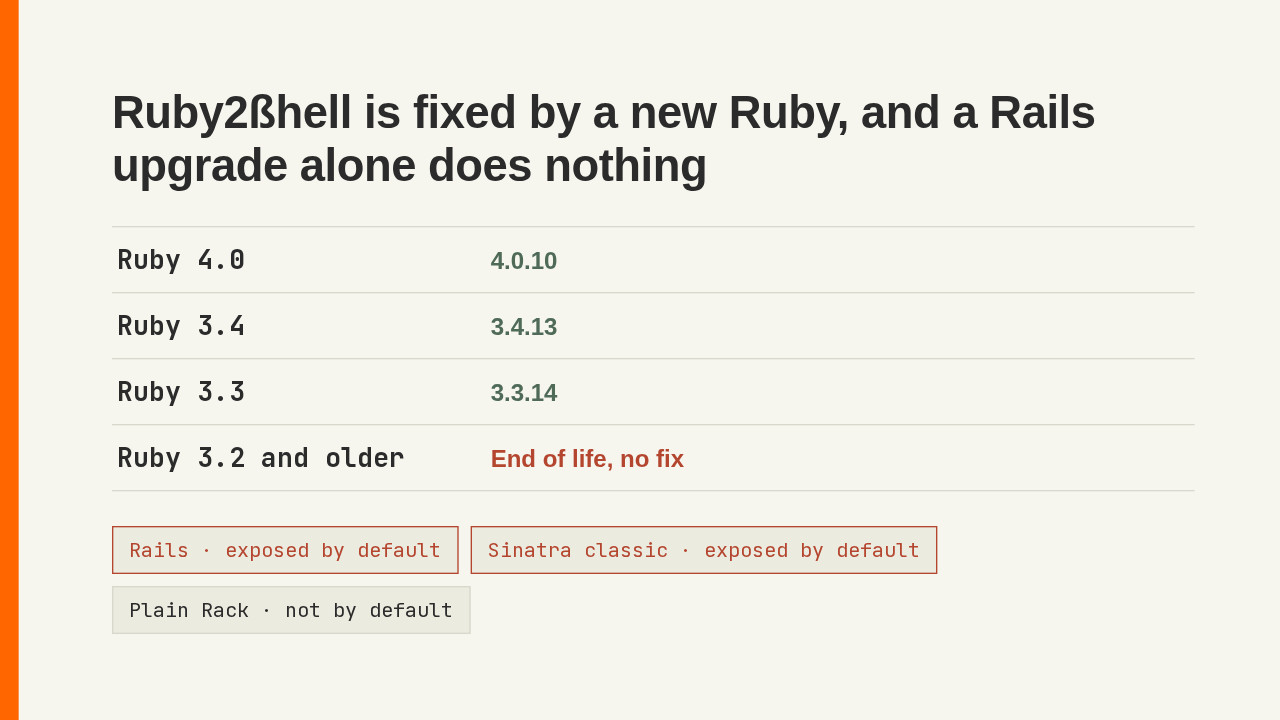
Ruby2ßhell reaches Rails and classic-style Sinatra in their default setup, so if you run either one, upgrade the Ruby underneath it. Each supported line has a patch release out. Ruby 3.2 and older are past end of life and stay vulnerable. The same releases fix six more memory bugs, most of them in the regular expression engine, which matter to any app that compiles a pattern a user typed. A working exploit for stock Rails goes public on November 25th.
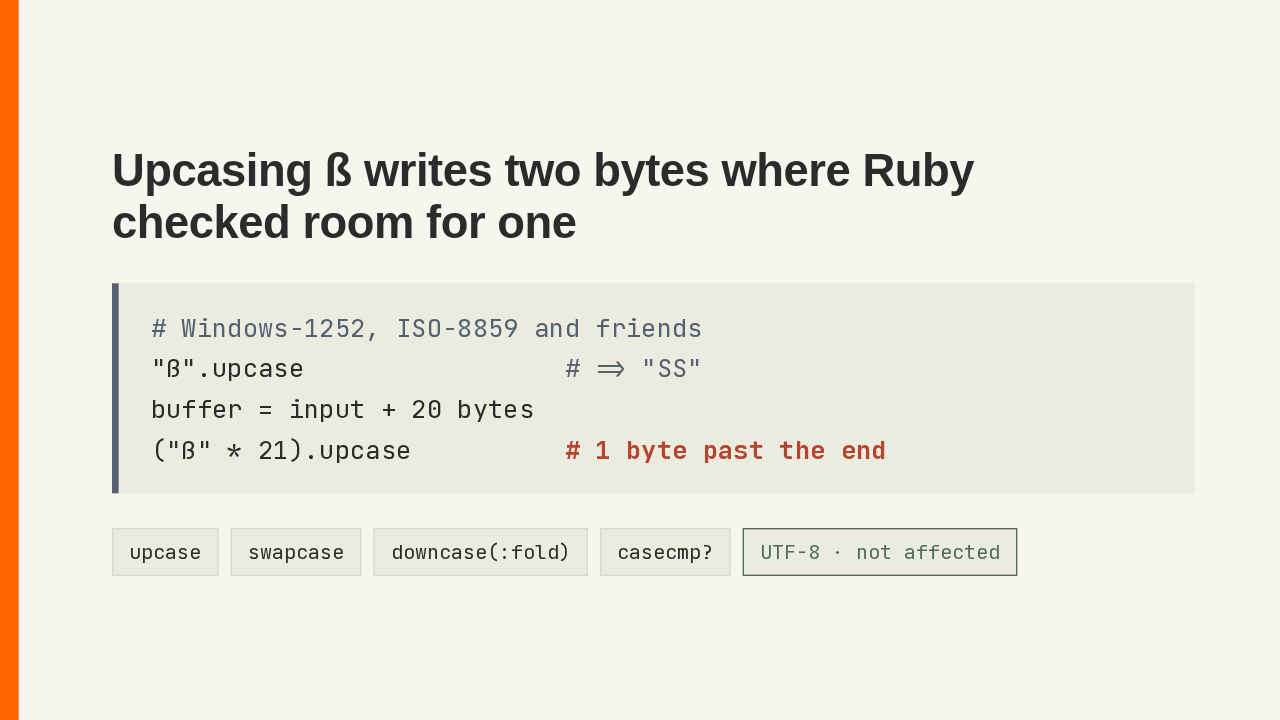
Most of Ruby's single-byte encodings, Windows-1252 among them, have no capital sharp S. So upcasing one writes two letters, double S, while the loop checks for room one byte at a time. The output buffer gets twenty spare bytes, so a string with twenty-one of them writes one byte past the end. Swapping or folding case reaches the same loop. Strings in UTF-8 take a different path and are safe.
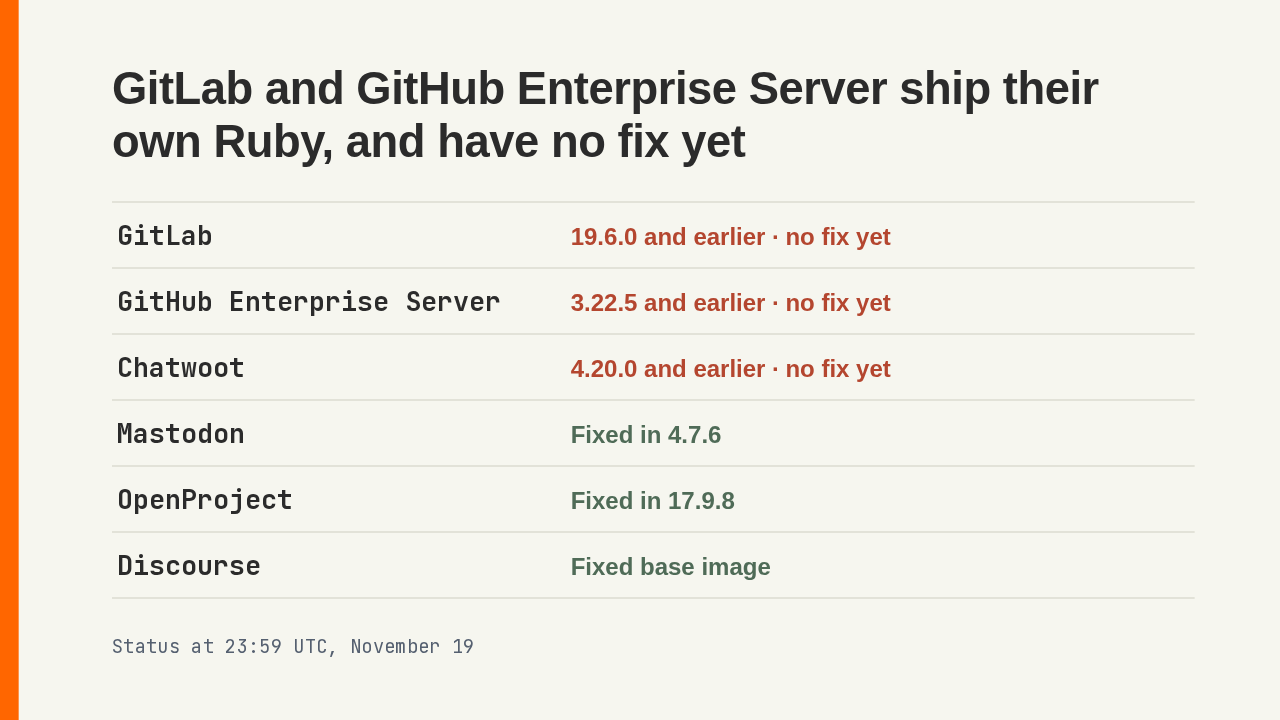
Self-hosted apps that bundle their own Ruby ignore the one on the server, so the fix has to come from the vendor. Mastodon, OpenProject and Discourse have shipped one. GitLab, GitHub Enterprise Server and Chatwoot are still vulnerable in every current version, six days before the exploit is due.
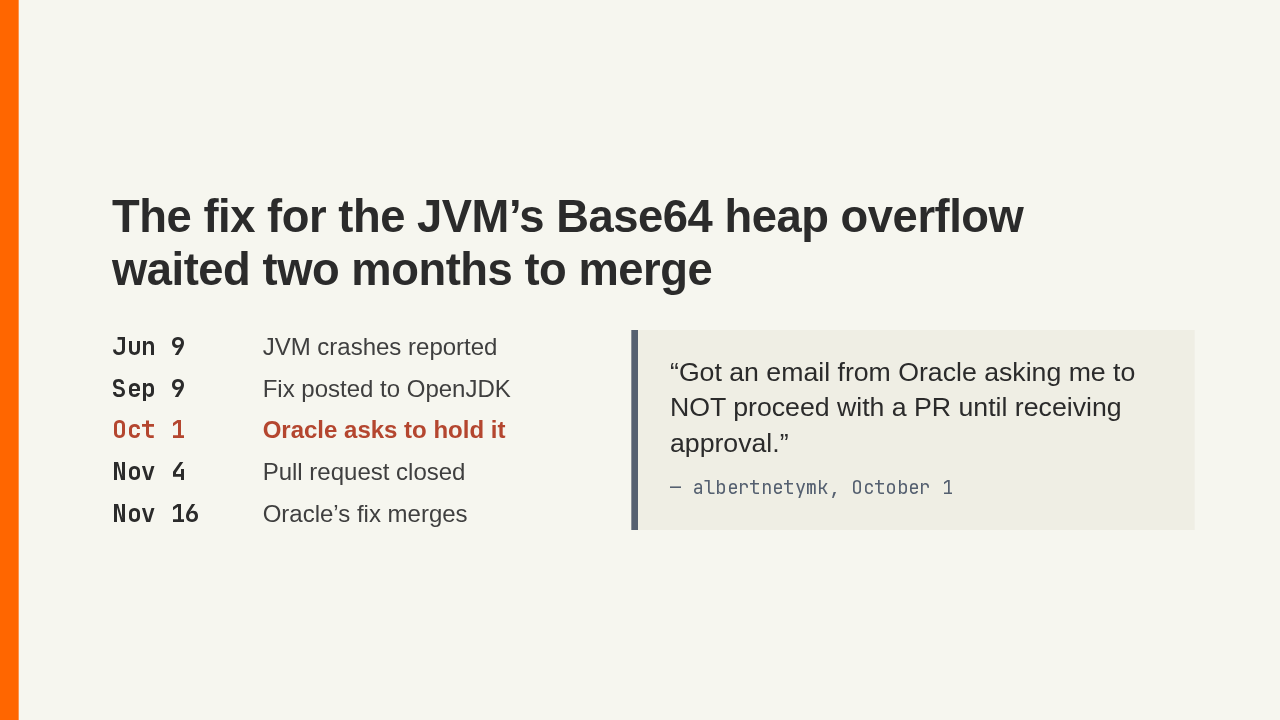
The bug now called java4shell is in the JVM's fast Base64 decoder for x86 chips with AVX-512. A malformed input with a short tail makes it write past its output buffer and corrupt the heap. Albert Yang, an OpenJDK developer, posted a fix in September, linked to crash reports from June. On October 1st, Oracle asked Yang to hold the pull request. Oracle's own fix, with Yang as co-author, merged on November 16th, under the title Base64 optimization improvements.
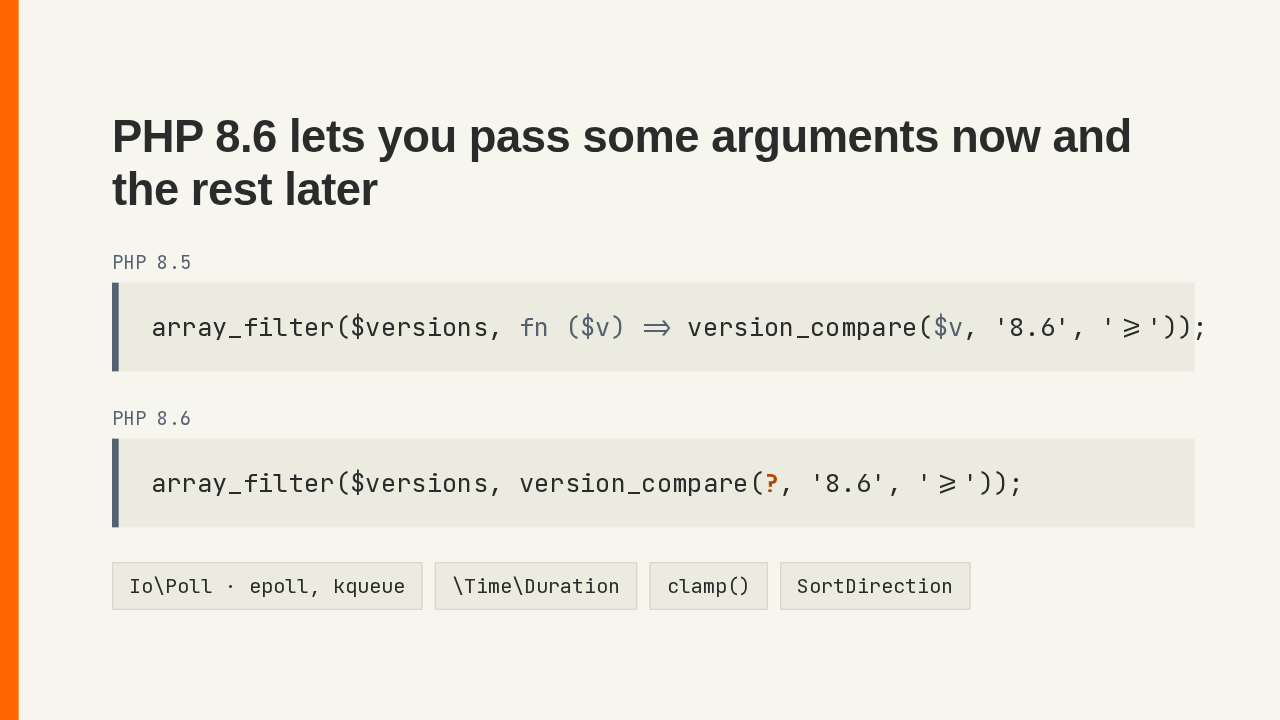
PHP 8.6 adds partial function application. Put a question mark where an argument goes, and the call hands back a closure that waits for it, so the arrow function goes away. The release also adds a polling API on epoll and kqueue, which lets PHP event loops get past the old limit of about a thousand connections. In the thread, williamdclt likes partials but worries that one now looks almost exactly like a function call.
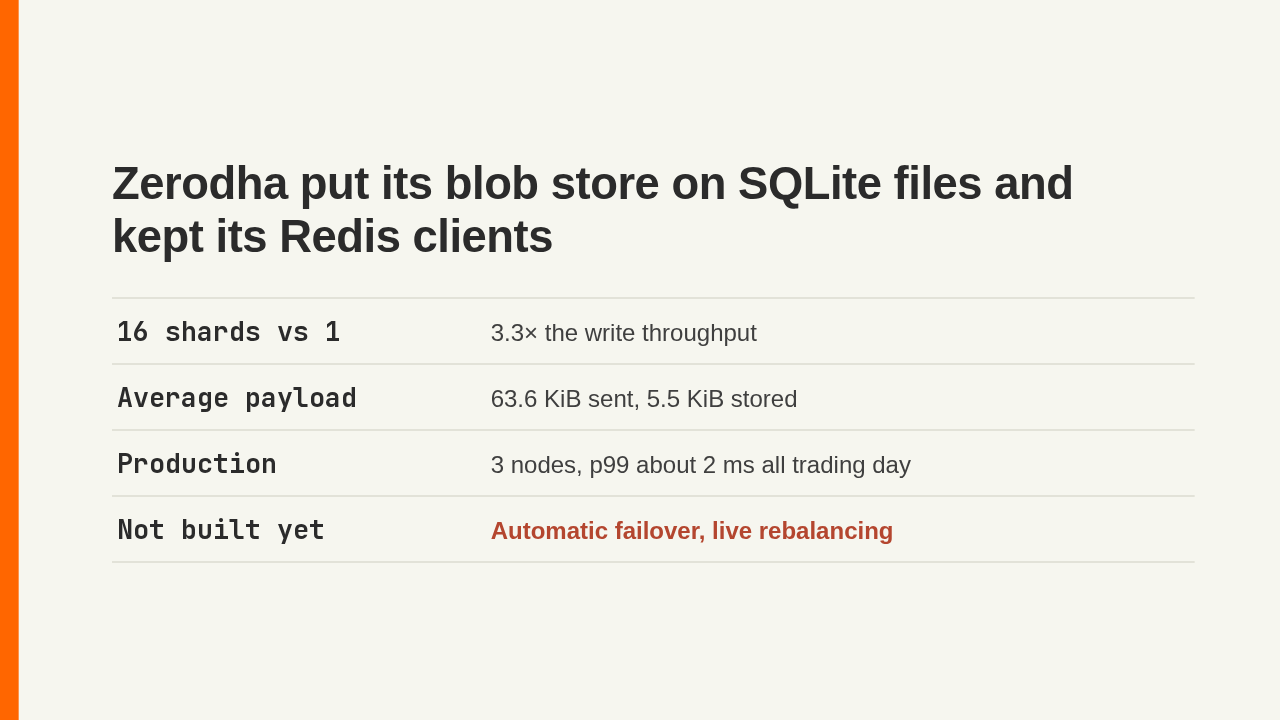
The trading platform Zerodha saves chart layouts and workspaces for about twenty million customers. Its new server, Blobasaur, is written in Rust and speaks the Redis protocol, so every service kept its client library. SQLite allows one writer per file, so each node spreads keys across many files and compresses every blob first. Three small nodes keep latency near two milliseconds through a whole trading session. In the thread, CyrusGrissom points out that the post never mentions replication.
Up next
 3:49
Nginx bugs let anyone run code on your server, ONNX Runtime goes dark, and Quad9 leaves France
@hacker-news
1 day ago
 4:15
Optimizely served malware on Zoom and GitLab, and Windows 11 logs your coding agents
@hacker-news
2 days ago
 4:10
uBlock Origin fixes a one-click XSS, ParadeDB joins, and free CMU courses
@hacker-news
2 days ago
 4:01
All AI code should be open source, and a chlorine alarm lost in a Microsoft 365 outage
@hacker-news
2 days ago
 4:19
Lovable apps leak passports, ggml hits 1.0, and Qwen3.8 27B fits a 24 GB Mac
@hacker-news
5 days ago
 3:43
Edge0-145B runs on one 16 GB NVIDIA card, and Brave sells search to AI agents
@hacker-news
6 days ago
 4:20
Apache’s HTTP/2 bug lets anyone run code, and Gemini 4 Hydrogen replaces Flash
@hacker-news
1 week ago
 4:01
AWS Emulator puts AWS on your laptop, and Apple's Harbor pools Macs for AI
@hacker-news
1 week ago
 3:40
Claude Fable 5.2 gets cheaper, and Amazon swaps Sonnet for Strands Decider
@hacker-news
1 week ago
 3:37
Claude Fable 5.2 runs faster for less, a number plate unlocks cars, and a $385 Raspberry Pi
@hacker-news
1 week ago
 4:15
Pi replaces Claude Code, Goldman cuts its traders off, and DeepSeek fits in 64 GB
@hacker-news
1 week ago
 4:12
Libghostty 1.0 is stable, your Mac maps your family, and Discord drops Electron
@hacker-news
1 week ago