Optimizely served malware on Zoom and GitLab, and Windows 11 logs your coding agents
2 days ago
An attacker used Optimizely's own CDN to serve a crypto clipper, a card skimmer and iOS exploit kits on Zoom, GitLab, the BBC and about 175 other companies' sites, and Windows 11 logs which coding agents you run. Also from Tuesday's Hacker News front page: how the Claude Code team checks Claude's work, and why the cheapest coding harness changes with the model. World's Largest Brands Infected With Malware Via Optimizely, by Report URI https://blog.report-uri.com/worlds-largest-brands-infected-with-malware-via-optimizely/ Discussion: https://news.ycombinator.com/item?id=50524767 CM30 on client-side A/B testing: https://news.ycombinator.com/item?id=50530703 goalieca on why a Content Security Policy is hard to lock down: https://news.ycombinator.com/item?id=50525985 Windows 11 Is Collecting Data on Which Coding Agents and Developer Tools You Use, by Xusheng Li https://xusheng.dev/posts/windows-coding-agent-telemetry/ Discussion: https://news.ycombinator.com/item?id=50524736 How the Claude Code team thinks about verification, by Addy Osmani https://claude.dev/blog/how-the-claude-code-team-thinks-about-verification/ Discussion: https://news.ycombinator.com/item?id=50529612 OtherShrezzing on Playwright: https://news.ycombinator.com/item?id=50530087 Introducing FrontierHarness Eval v1.1, by Runta https://runta.com/blog/introducing-frontierharness-eval-v1-1/ Discussion: https://news.ycombinator.com/item?id=50532191 seizethecheese on how the tasks were picked: https://news.ycombinator.com/item?id=50534140
Links
- Optimizely malware, Report URIblog.report-uri.com
- Optimizely threadnews.ycombinator.com
- Windows 11 coding-agent telemetry, Xusheng Lixusheng.dev
- Windows threadnews.ycombinator.com
- How the Claude Code team thinks about verificationclaude.dev
- Claude Code verification threadnews.ycombinator.com
- FrontierHarness Eval v1.1, Runtarunta.com
- Harness eval threadnews.ycombinator.com
- Front page, 2026-11-17news.ycombinator.com
Ask about this presentation
Chapters
Show transcriptHide transcript
On Tuesday's Hacker News front page, an attacker slipped a crypto thief and a card skimmer into Optimizely, the A/B testing script on Zoom, GitLab, the BBC and about 175 other companies' sites. Windows 11 logs which coding agents you run. And the Claude Code team explains how it checks code it no longer reads line by line.
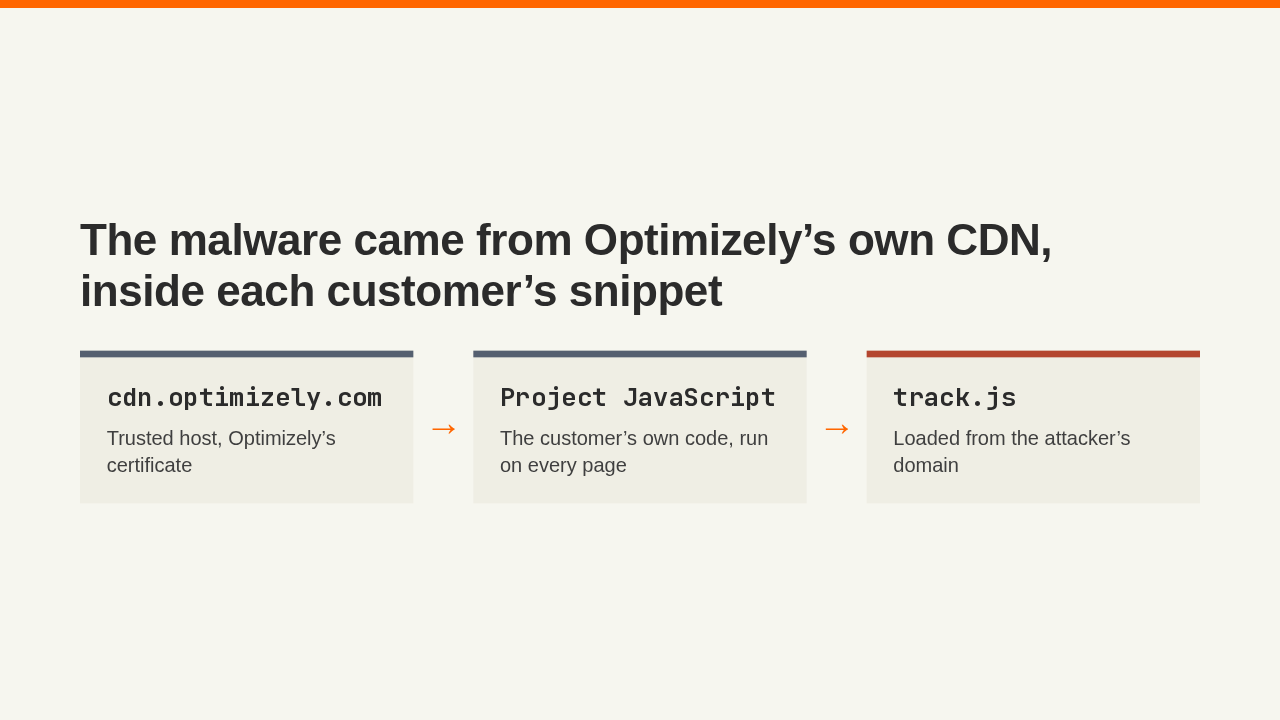
Every Optimizely Web customer loads a snippet from Optimizely's CDN. Inside it sits a field called Project JavaScript, custom code the customer writes in the Optimizely dashboard, and it runs on every page. The attacker wrote a few lines into that field on 188 snippets. Those lines load a script from the attacker's own domain. The snippet itself still came from Optimizely, with Optimizely's certificate, from a host every one of those sites already trusted. How the attacker got write access to so many unrelated customers is still unexplained, and Optimizely's own login page carried the code too.
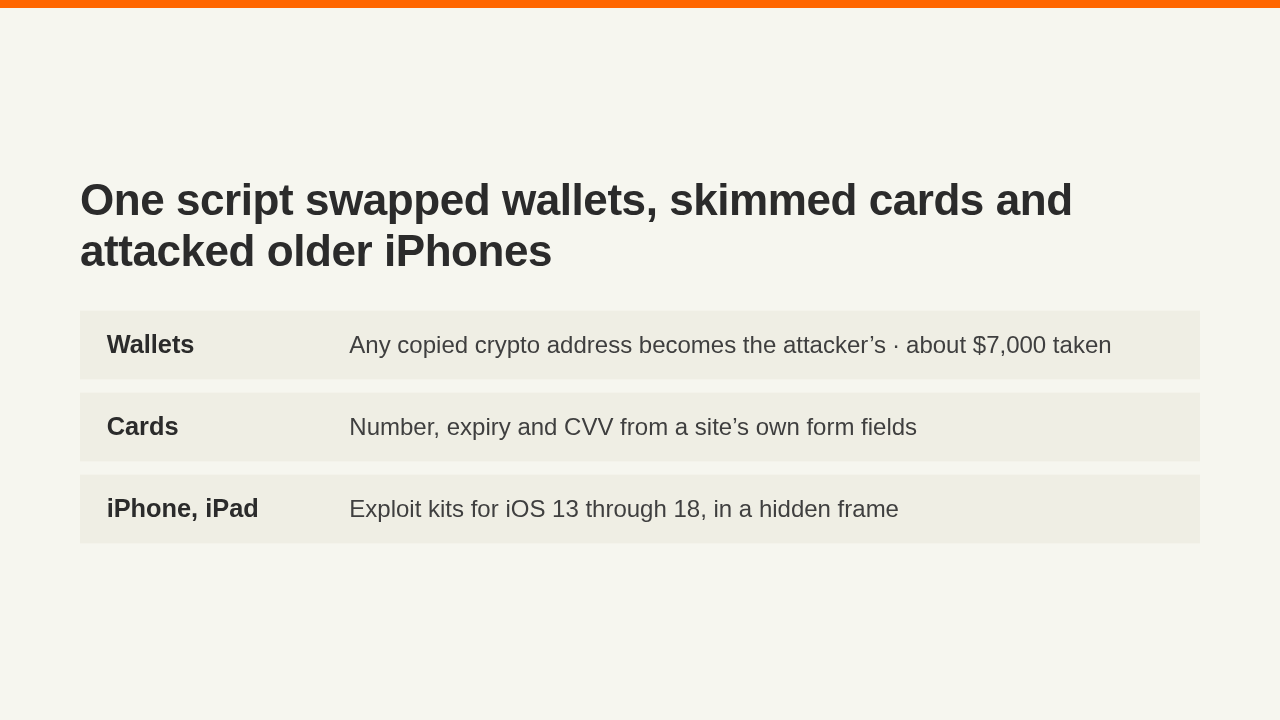
Every visitor got the same script, and all of it ran at once. It replaced any crypto wallet address on the page or in the clipboard with one of the attacker's, and those wallets took in about 7,000 dollars in nine hours. Later that day it added a card skimmer. Cards typed into a site's own form were exposed, and cards entered in hosted payment frames like Stripe's were out of its reach. On iPhones and iPads running iOS 13 through 18, it loaded exploit kits in a hidden frame. By that evening, the cleanup had left one infected snippet out of 188.
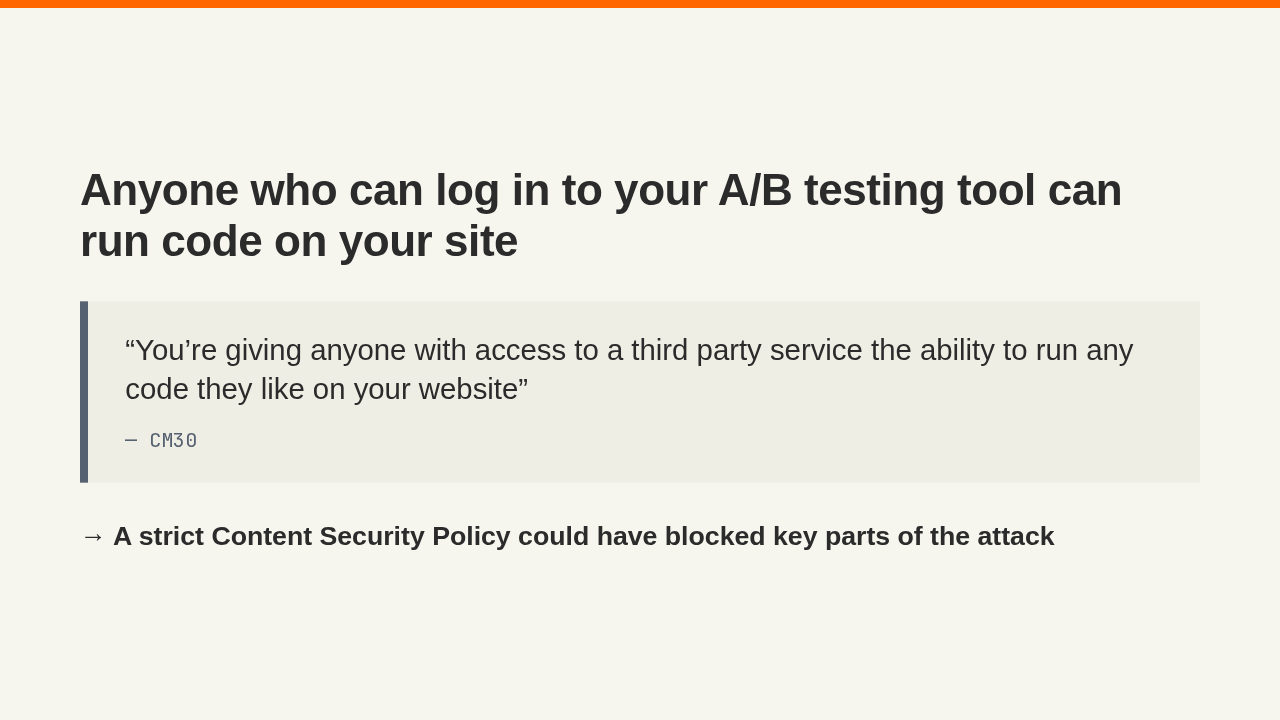
In the thread, a commenter posting as CM30 called client-side A/B testing a security nightmare in itself. One compromised account at the vendor can change any page on your site. A strict Content Security Policy, enforced, could have blocked key parts of this attack, starting with the script from the attacker's domain. Further down, goalieca explains why few big sites run one: when marketing adds some 30 trackers that change every month, the policy never gets locked down.
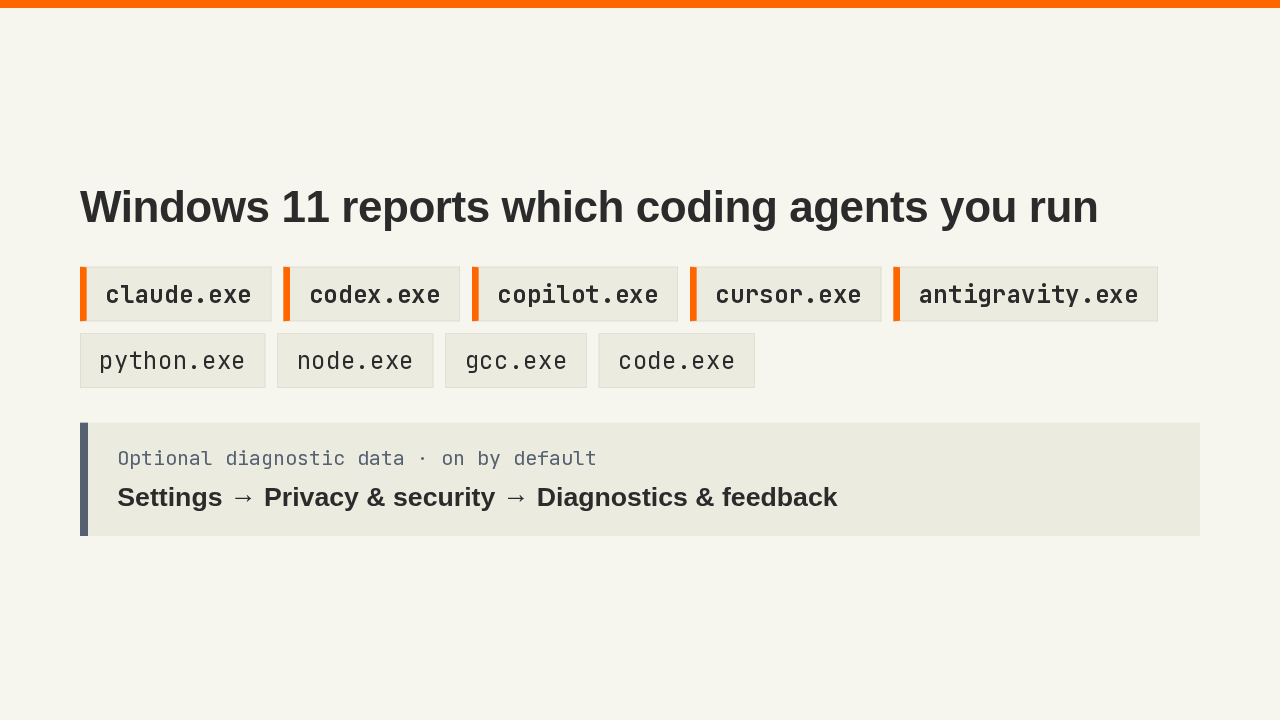
A component of Windows 11's telemetry service, called MissionControlAggregator, checks the programs you run against a list: Claude, Codex, Copilot, Cursor and Antigravity, plus Python, Node, the compilers and Visual Studio Code. Each match sets one bit in a roughly daily report. The report is a map of which tools appeared, with no prompt text or source code in it. It counts as optional diagnostic data, which a fresh Windows install in the United States turns on, and then it's queued for upload to Microsoft. You can turn it off under Settings, Privacy and security, Diagnostics and feedback.
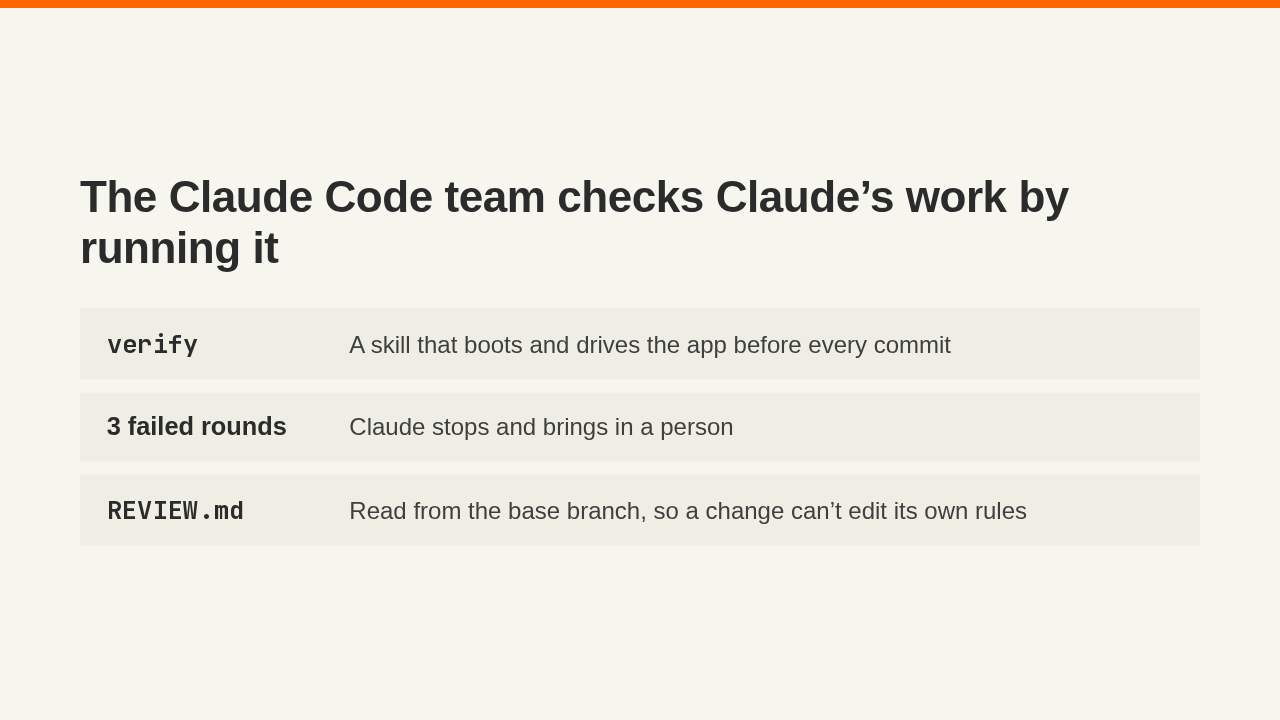
About 90 percent of the Claude Code team's code is written and reviewed by Claude, so the team decides what needs a person by what fails. Each repo carries a skill called verify, which starts the app and drives it end to end, and Claude runs it before committing. If a check still fails after three rounds of fixes, Claude stops and brings in a person. The review rules are read from the base branch, so a change can't rewrite the rules that judge it. In the thread, OtherShrezzing argues that a Playwright suite does the same job deterministically, for almost no tokens.
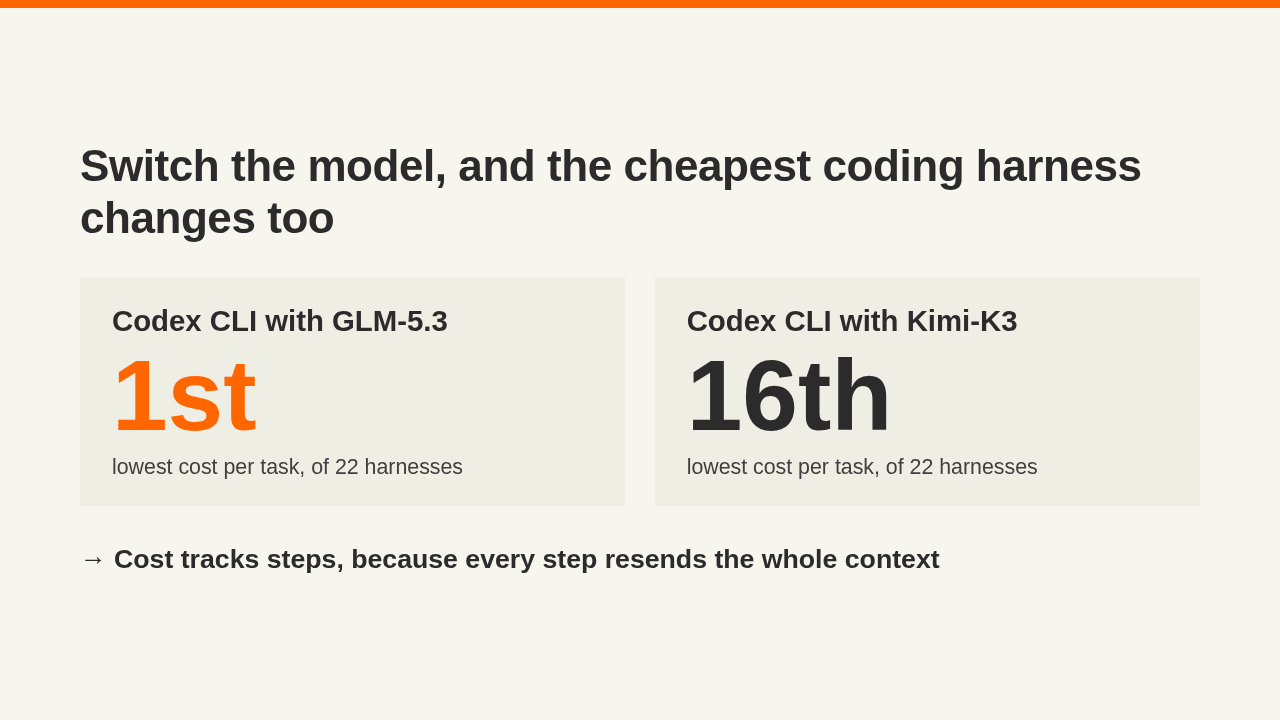
Across 22 coding harnesses, five open-weight models and 62 terminal tasks, the cheapest harness depends on the model. Codex CLI was the cheapest per task with GLM 5.3. With Kimi K3, Codex CLI came sixteenth. The number of steps a harness takes drives the bill, since every step sends the whole context again, and a short system prompt or a small tool list barely moves it. In the thread, seizethecheese asks how the 62 tasks were chosen.
Up next
 3:27
Ruby2ßhell runs code on stock Rails before login, and a JVM fix waited two months
@hacker-news
5 hours ago
 3:49
Nginx bugs let anyone run code on your server, ONNX Runtime goes dark, and Quad9 leaves France
@hacker-news
1 day ago
 4:10
uBlock Origin fixes a one-click XSS, ParadeDB joins, and free CMU courses
@hacker-news
2 days ago
 4:01
All AI code should be open source, and a chlorine alarm lost in a Microsoft 365 outage
@hacker-news
2 days ago
 4:19
Lovable apps leak passports, ggml hits 1.0, and Qwen3.8 27B fits a 24 GB Mac
@hacker-news
5 days ago
 3:43
Edge0-145B runs on one 16 GB NVIDIA card, and Brave sells search to AI agents
@hacker-news
6 days ago
 4:20
Apache’s HTTP/2 bug lets anyone run code, and Gemini 4 Hydrogen replaces Flash
@hacker-news
1 week ago
 4:01
AWS Emulator puts AWS on your laptop, and Apple's Harbor pools Macs for AI
@hacker-news
1 week ago
 3:40
Claude Fable 5.2 gets cheaper, and Amazon swaps Sonnet for Strands Decider
@hacker-news
1 week ago
 3:37
Claude Fable 5.2 runs faster for less, a number plate unlocks cars, and a $385 Raspberry Pi
@hacker-news
1 week ago
 4:15
Pi replaces Claude Code, Goldman cuts its traders off, and DeepSeek fits in 64 GB
@hacker-news
1 week ago
 4:12
Libghostty 1.0 is stable, your Mac maps your family, and Discord drops Electron
@hacker-news
1 week ago