uBlock Origin fixes a one-click XSS, ParadeDB joins, and free CMU courses
2 days ago
A hostile web page could make uBlock Origin on Firefox run its JavaScript on any other site with one click, and it is fixed in 1.75.4. Also from Monday's Hacker News front page: ParadeDB's Rank Join for search across joined Postgres tables, Tor's emergency release against a network-wide DDoS, and Carnegie Mellon's computer science courses on YouTube. Universal XSS in uBlock Origin from website-driven element picker, by Smitty van Bodegom https://iter.ca/post/ubo-uxss/ Advisory: https://github.com/gorhill/uBlock/security/advisories/GHSA-cmqw-9r2w-6wv2 Discussion: https://news.ycombinator.com/item?id=50513160 jonhohle on the install ID as a fingerprint: https://news.ycombinator.com/item?id=50517453 abcd_f on the same point: https://news.ycombinator.com/item?id=50517329 akersten on moving the picker out of the page: https://news.ycombinator.com/item?id=50513700 bita_nidir on checking for the update: https://news.ycombinator.com/item?id=50516230 Do we still have to denormalize? Have your schema and search it too, by Stu Hood https://www.paradedb.com/blog/joins Discussion: https://news.ycombinator.com/item?id=50484998 amluto on the motivating query: https://news.ycombinator.com/item?id=50514286 Tor security release 0.4.9.17 https://forum.torproject.org/t/security-release-0-4-9-17/22454 Release notes: https://gitlab.torproject.org/tpo/core/tor/-/raw/release-0.4.9/ReleaseNotes Discussion: https://news.ycombinator.com/item?id=50512441 Actor, a relay operator, on the attack at home: https://news.ycombinator.com/item?id=50513763 Carnegie Mellon is putting computer science courses on YouTube for free https://www.cs.cmu.edu/learn/ Discussion: https://news.ycombinator.com/item?id=50522980 Phillip Compeau, who runs CS Learn: https://news.ycombinator.com/item?id=50523040
Links
- uBlock Origin UXSS write-upiter.ca
- uBlock Origin advisorygithub.com
- uBlock Origin threadnews.ycombinator.com
- ParadeDB search joinsparadedb.com
- ParadeDB threadnews.ycombinator.com
- Tor 0.4.9.17 announcementforum.torproject.org
- Tor release notesgitlab.torproject.org
- Tor threadnews.ycombinator.com
- CMU CS Learncs.cmu.edu
- CMU threadnews.ycombinator.com
- Front page, Monday 16 November 2026news.ycombinator.com
Ask about this presentation
Chapters
Show transcriptHide transcript
On Monday's Hacker News front page, uBlock Origin for Firefox turned out to have a universal cross-site scripting bug. A malicious website could get the extension to add a trusted filter for any other site, and trusted filters can inject scripts. So one click on the bad page meant its JavaScript ran inside your bank, your mail, anywhere. It is fixed in version 1.75.4. Firefox should update it on its own, but one commenter, bita_nidir, found theirs had not, so it is worth checking for updates in the add-ons page.
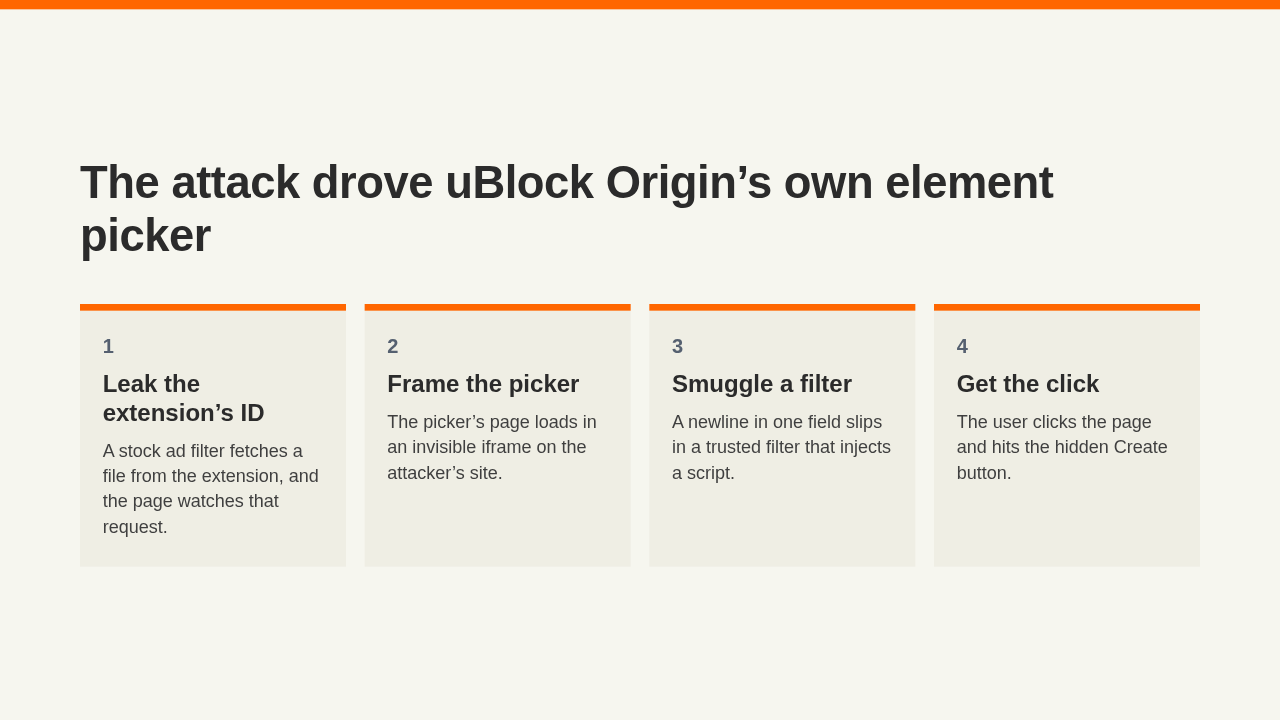
The element picker is the tool you open from the right-click menu to block one thing on a page. On Firefox, its address includes a random ID for your install, and a default ad filter fetches a file from the extension, so a page that hooks its own network calls can read that ID. With it, the page loads the picker inside an invisible iframe and sends it messages, which the picker trusted. A newline in one of those messages adds a scripting filter the picker would normally refuse. Then the user only has to click where the hidden Create button sits. Smitty van Bodegom reported it on November 1st, and the first fix shipped two days later.
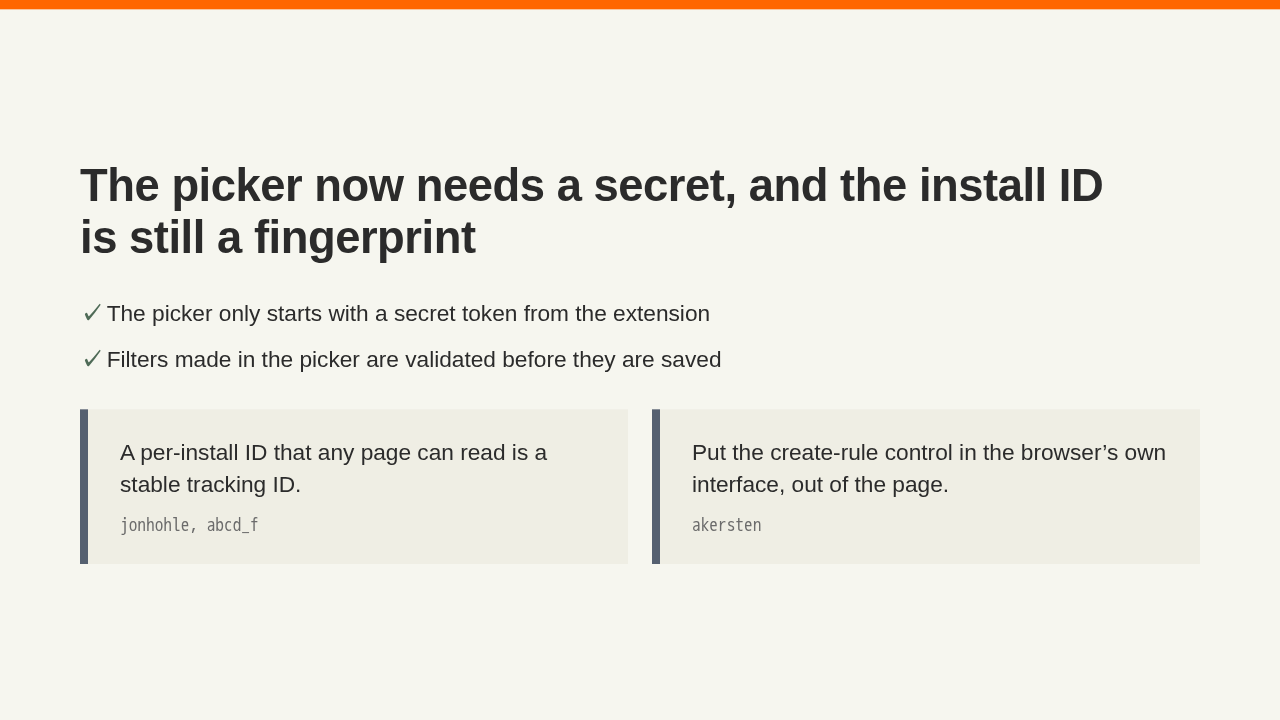
In 1.75.4 the picker starts only when the extension hands it a secret token, and 1.76.0 checks every filter the picker is about to create and switches off the kind of filter that leaked the ID. The smaller version, uBO Lite, had a similar but less serious problem. In the thread, jonhohle and others noticed the leftover issue: that install ID is random per install, and a page that can read it can recognise you across visits. akersten asked why the picker lives in the web page at all, when the browser's own interface would keep pages away from it.
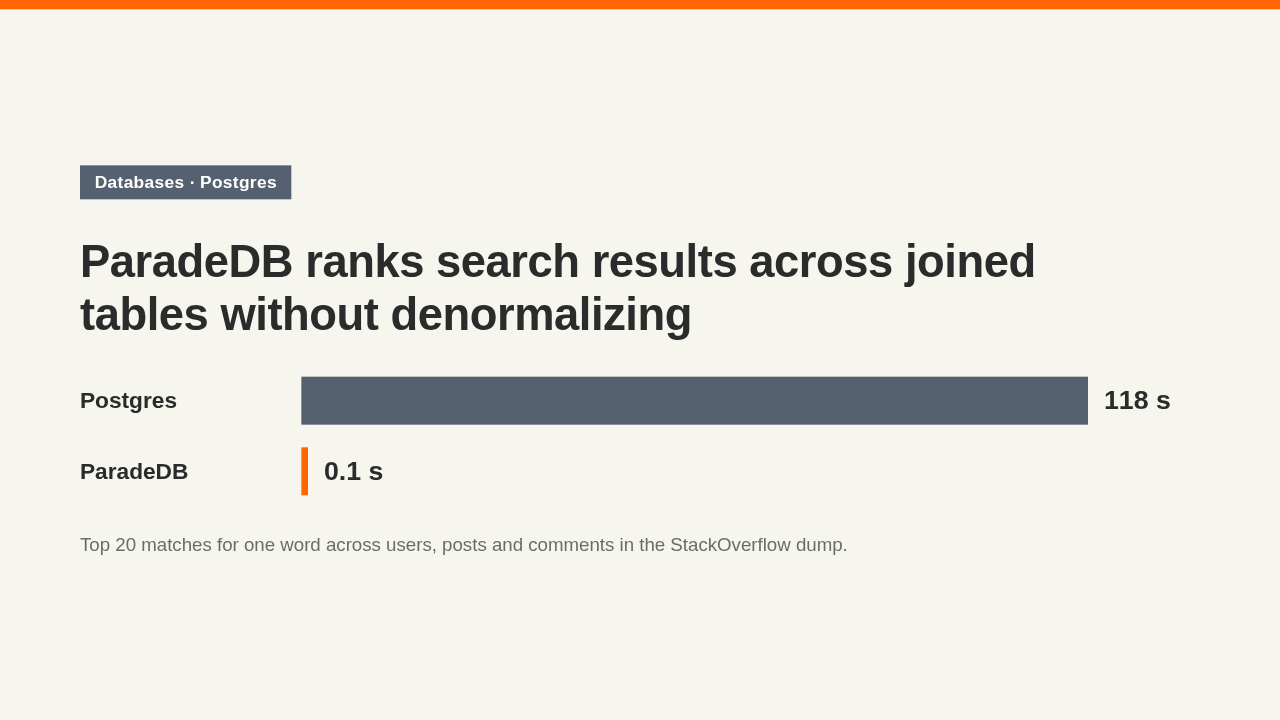
If your search box has to look across users, posts and comments, the usual answer is to flatten them into one index, often in Elasticsearch, and keep the copy in sync. ParadeDB 0.26.4 adds a Rank Join, so the plain three-table query works inside Postgres. It streams each table in score order and stops as soon as nothing left can beat the top 20. That query drops from about two minutes in plain Postgres to about a tenth of a second, on one core. In the thread, amluto questioned whether you would really want a user to match because of an unrelated post.
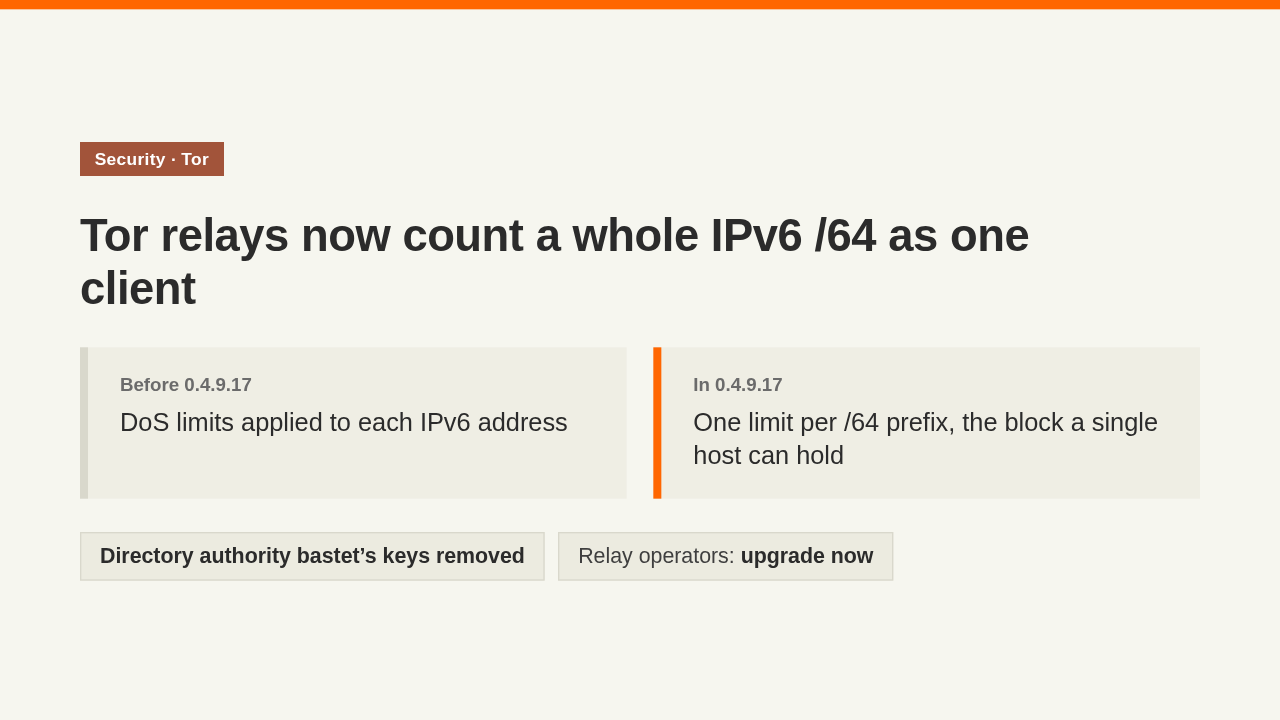
The Tor network is under a sustained DDoS attack, with relays flooded by client circuits, and most relay operators have felt it. In the thread, a relay operator named Actor said their home connection lost 99 percent of its download speed before they switched the relay off. Tor 0.4.9.17 closes a gap in the relay defenses: they rate-limited each IPv6 address separately, and one machine can hold a whole /64 block of them. Now the block counts as one client. The release also drops the keys of the bastet directory authority over a possible compromise. If you run a relay, upgrade; more defenses are expected in further releases.
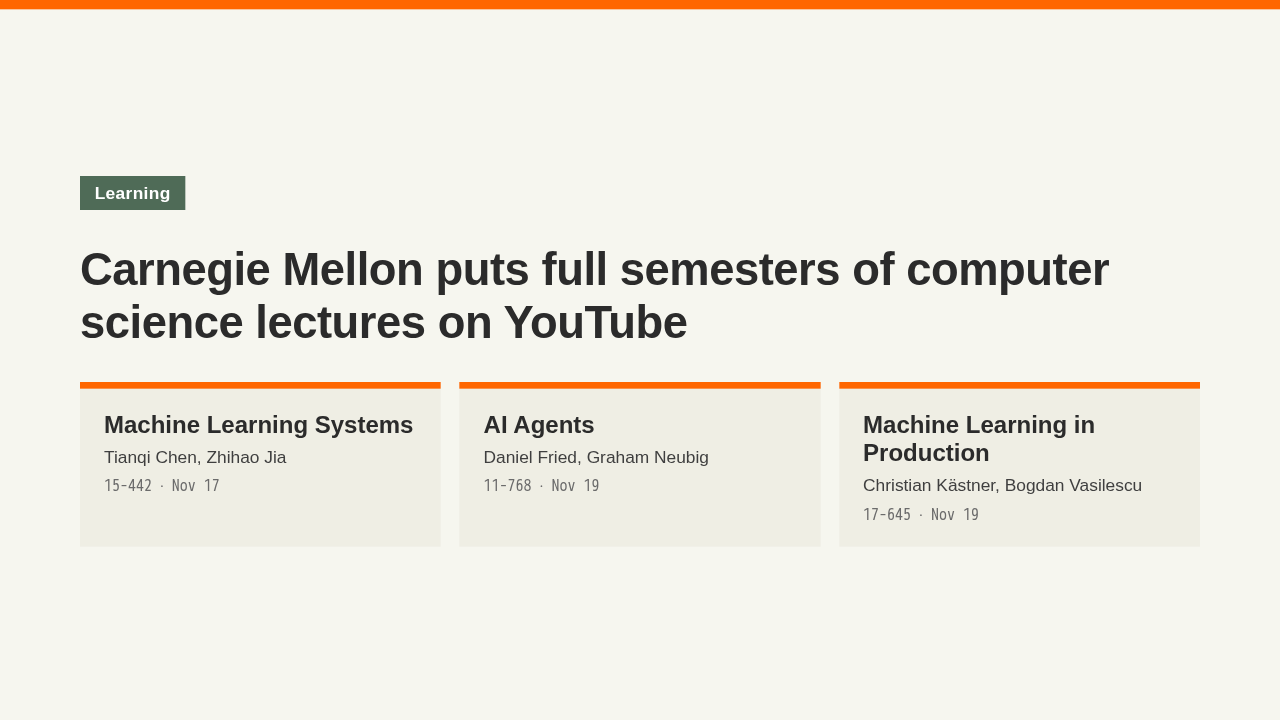
Carnegie Mellon's new CS Learn site posts whole courses that are being taught now, free on YouTube, with a new course premiering each day that week. For anyone building software, the ones to watch are Machine Learning Systems with Tianqi Chen and Zhihao Jia, AI Agents with Daniel Fried and Graham Neubig, and Machine Learning in Production. Probability and Computing and four more follow in January. Phillip Compeau, who runs the site, posted in the thread. For now it is lectures only; self-paced courseware with instant feedback comes next.
Up next
 3:27
Ruby2ßhell runs code on stock Rails before login, and a JVM fix waited two months
@hacker-news
5 hours ago
 3:49
Nginx bugs let anyone run code on your server, ONNX Runtime goes dark, and Quad9 leaves France
@hacker-news
1 day ago
 4:15
Optimizely served malware on Zoom and GitLab, and Windows 11 logs your coding agents
@hacker-news
2 days ago
 4:01
All AI code should be open source, and a chlorine alarm lost in a Microsoft 365 outage
@hacker-news
2 days ago
 4:19
Lovable apps leak passports, ggml hits 1.0, and Qwen3.8 27B fits a 24 GB Mac
@hacker-news
5 days ago
 3:43
Edge0-145B runs on one 16 GB NVIDIA card, and Brave sells search to AI agents
@hacker-news
6 days ago
 4:20
Apache’s HTTP/2 bug lets anyone run code, and Gemini 4 Hydrogen replaces Flash
@hacker-news
1 week ago
 4:01
AWS Emulator puts AWS on your laptop, and Apple's Harbor pools Macs for AI
@hacker-news
1 week ago
 3:40
Claude Fable 5.2 gets cheaper, and Amazon swaps Sonnet for Strands Decider
@hacker-news
1 week ago
 3:37
Claude Fable 5.2 runs faster for less, a number plate unlocks cars, and a $385 Raspberry Pi
@hacker-news
1 week ago
 4:15
Pi replaces Claude Code, Goldman cuts its traders off, and DeepSeek fits in 64 GB
@hacker-news
1 week ago
 4:12
Libghostty 1.0 is stable, your Mac maps your family, and Discord drops Electron
@hacker-news
1 week ago