Nginx bugs let anyone run code on your server, ONNX Runtime goes dark, and Quad9 leaves France
1 day ago
Two critical HTTP/2 bugs in Nginx let an unauthenticated attacker run code on the server; upgrade, or turn HTTP/2 off until you can. Also from Wednesday's Hacker News front page: Microsoft's ONNX Runtime repository going private while agent-framework releases on PyPI steal credentials, Quad9 leaving France on November 24, and why Gemini 4 Carbon is so slow at fixing bugs. Unauthenticated remote code execution in Nginx (CVE-2026-123633, CVE-2026-123007), by Wiz Research https://www.wiz.io/blog/nginx-http2-rce-vulnerabilities Fixed in Nginx 1.30.7 stable and 1.31.9 mainline. Workaround: http2 off; on Nginx 1.25.1 or later. Discussion: https://news.ycombinator.com/item?id=50547374 verst on gRPC services and disabling HTTP/2: https://news.ycombinator.com/item?id=50548865 Microsoft's ONNX Runtime has disappeared from GitHub https://github.com/microsoft/onnxruntime Discussion: https://news.ycombinator.com/item?id=50539610 nvader on evals failing: https://news.ycombinator.com/item?id=50539658 Heliodex on Intel's fork: https://news.ycombinator.com/item?id=50540243 robertknight on RTen: https://news.ycombinator.com/item?id=50543994 Microsoft's statement, in The Register: https://www.theregister.com/security/2026/11/18/microsofts-official-python-agent-framework-hijacked-to-distribute-malware/5310858 agent-framework 1.26.1 and 1.26.2 on PyPI compromised, by Socket: https://socket.dev/blog/agent-framework-pypi-package-compromised-with-credential-stealer DNS resolvers are the wrong place to fight piracy (Quad9 is leaving France), by Al Smith https://techstackups.com/articles/quad9-leaves-france-dns-blocking/ Discussion: https://news.ycombinator.com/item?id=50545958 Why is Gemini 4 Carbon taking so long?, by Kernel https://kernel.dev/blog/why-is-gemini-4-carbon-taking-so-long/ Discussion: https://news.ycombinator.com/item?id=50541790 bagacrap on the extra work as a feature: https://news.ycombinator.com/item?id=50547330
Links
- Wiz, Unauthenticated RCE in Nginxwiz.io
- Nginx threadnews.ycombinator.com
- ONNX Runtime repositorygithub.com
- ONNX Runtime threadnews.ycombinator.com
- The Register on agent-framework and Microsoft's statementtheregister.com
- Socket on agent-frameworksocket.dev
- Quad9 is leaving Francetechstackups.com
- Quad9 threadnews.ycombinator.com
- Why is Gemini 4 Carbon taking so long?kernel.dev
- Gemini threadnews.ycombinator.com
- Front pagenews.ycombinator.com
Ask about this presentation
Chapters
Show transcriptHide transcript
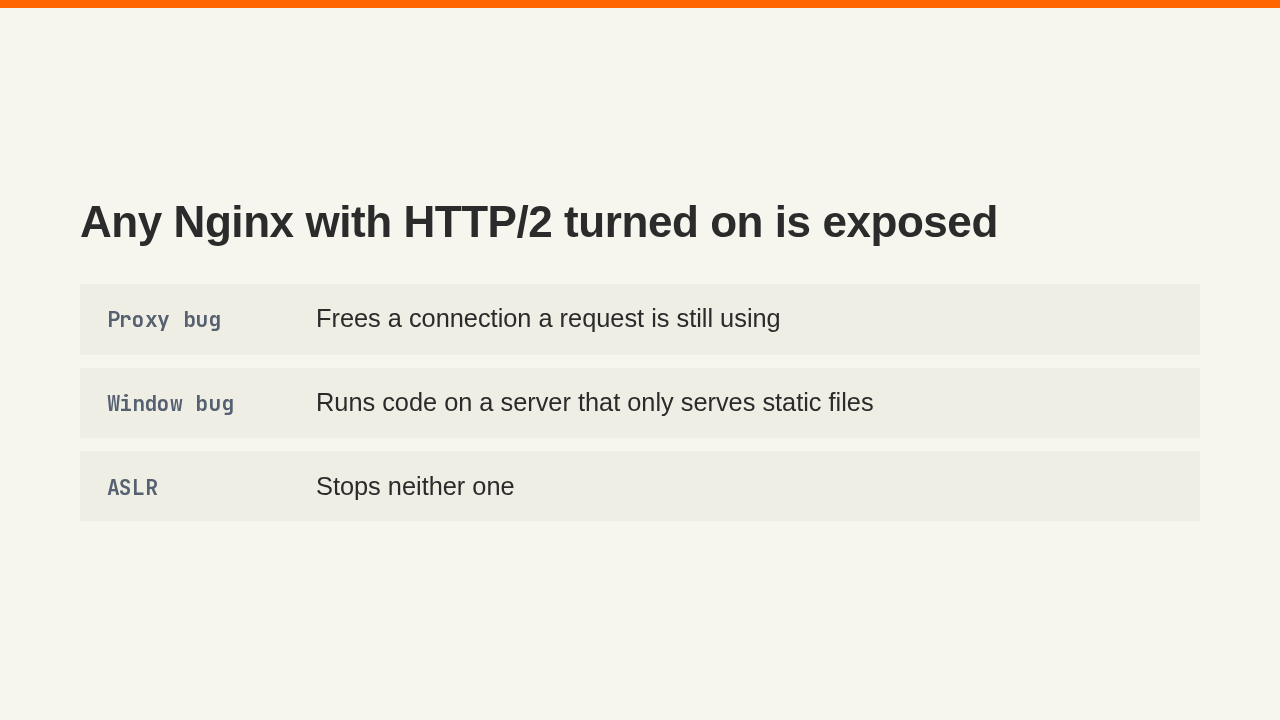
On Wednesday's Hacker News front page, Nginx shipped fixes for two critical bugs in its HTTP/2 code. Either one lets an attacker who never logs in run code on the server. One of them has been in Nginx since 2015, and five research teams found the same pair on their own, at least one of them with an AI code scanner doing the tracing.
Slide text

Nginx bugs let anyone run code on your server, ONNX Runtime goes dark, and Quad9 leaves France
Both bugs need HTTP/2 switched on, and that is the only setting that matters for the worse one. The first hits Nginx as a reverse proxy: when connection slots run low, it frees a connection that a request is still using. The second is an integer underflow in HTTP/2 flow control, and it ran code on a server serving plain static files, with no backend and no extra modules. Both leak memory before they write to it, so ASLR doesn't save you.
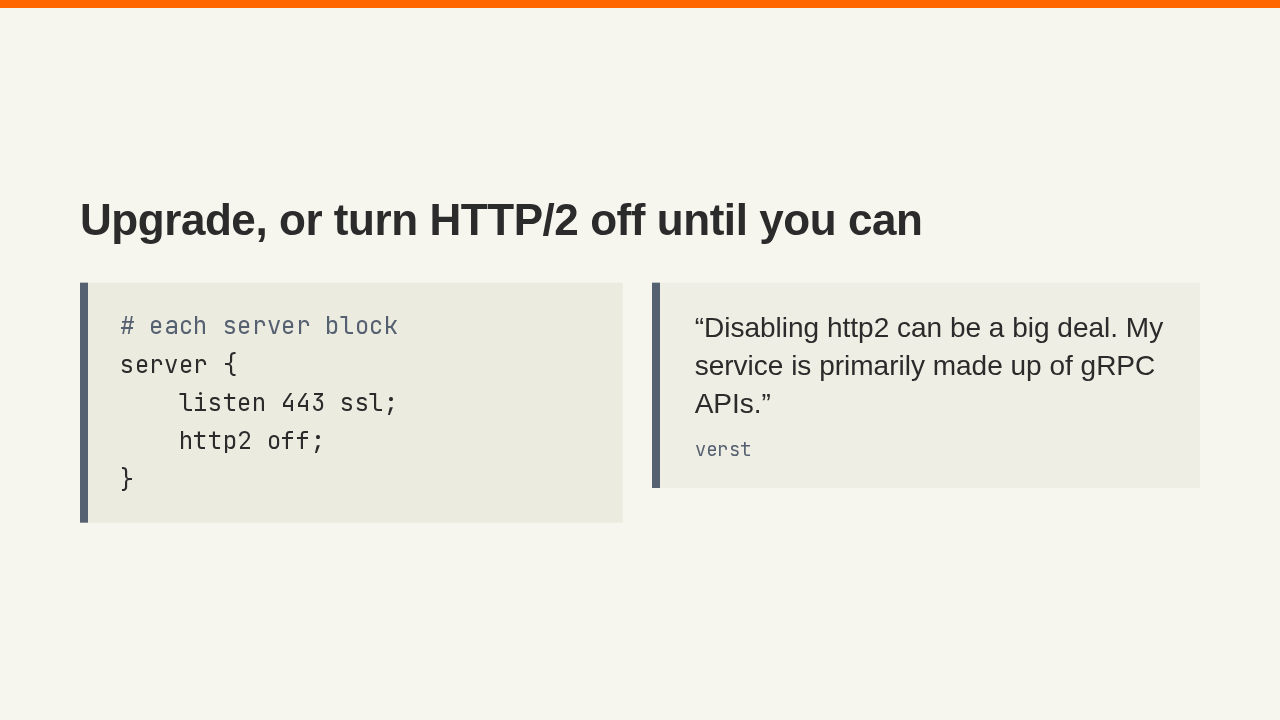
The fix is in the new stable and mainline releases of Nginx, and Nginx Plus has its own builds. If you can't upgrade yet, set http2 off in each server block, take http2 off every listen line, then reload and make sure the old workers have exited. That workaround costs some teams more than others. In the thread, verst points out that a service built on gRPC APIs can't simply turn HTTP/2 off, because gRPC runs over it.
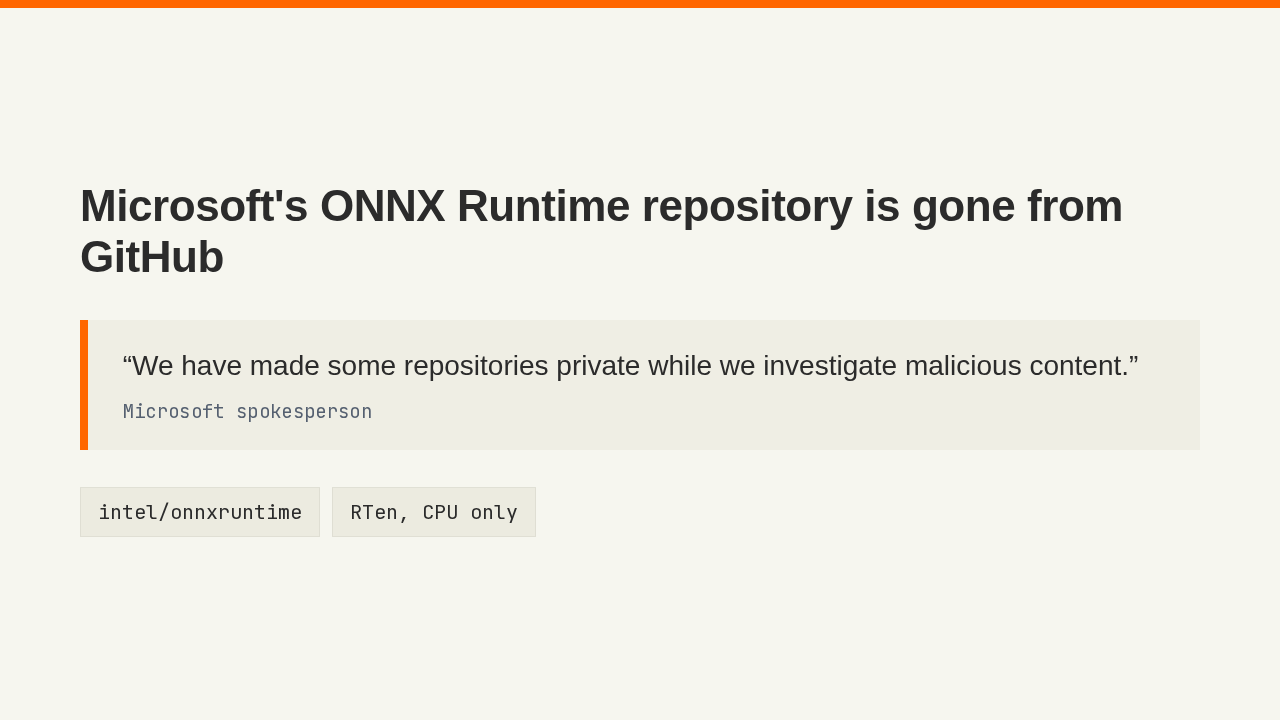
Microsoft's ONNX Runtime repository went private on GitHub without notice. nvader, who posted it, found out when evals started failing in their pipelines. Microsoft's explanation is one line: some repositories are private while it investigates malicious content. If you need the source in the meantime, Heliodex points to Intel's fork, which carries Intel's OpenVINO changes, and robertknight, who maintains RTen, offers RTen as a drop-in replacement for inference on the CPU.
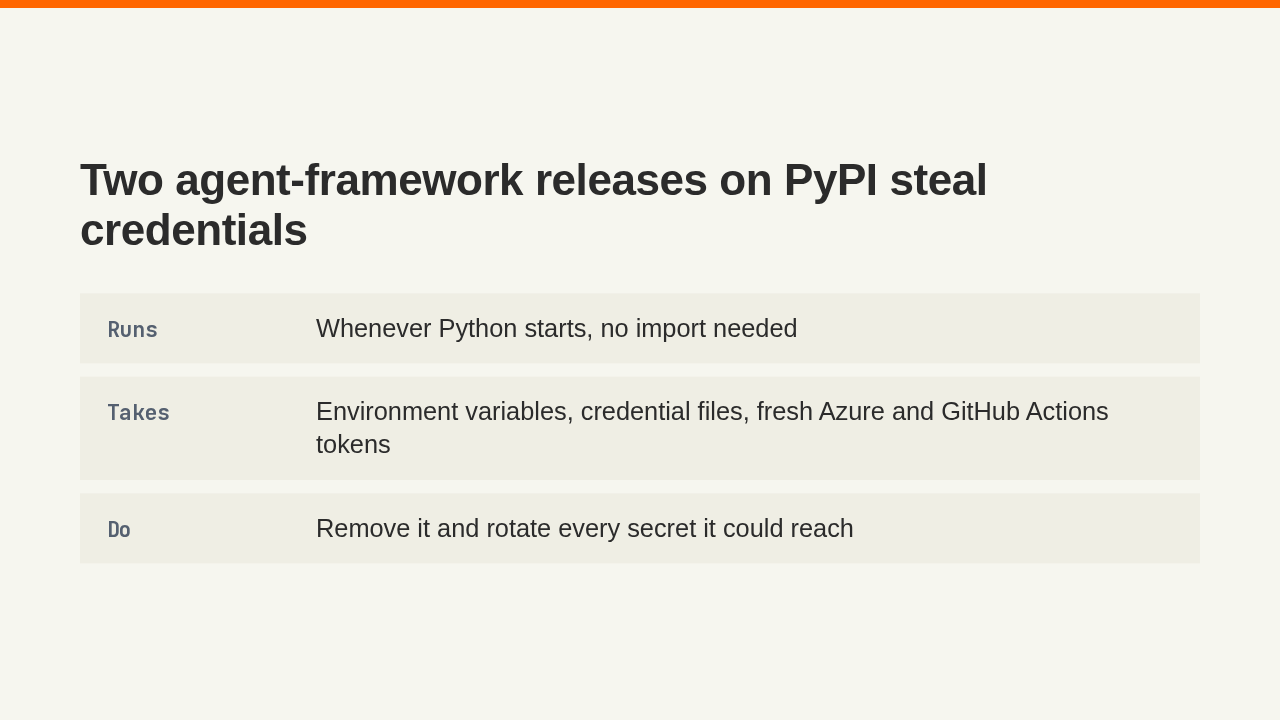
Microsoft's agent-framework repository is offline too. Two of the newest agent-framework releases on PyPI carry a credential stealer. A startup hook runs it whenever Python starts, so your code never has to import the package. It collects environment variables and credential files, then requests fresh Azure and GitHub Actions tokens and sends them out. If either release reached a build machine, remove it and rotate every secret that machine could reach. Microsoft hasn't tied this to ONNX Runtime.
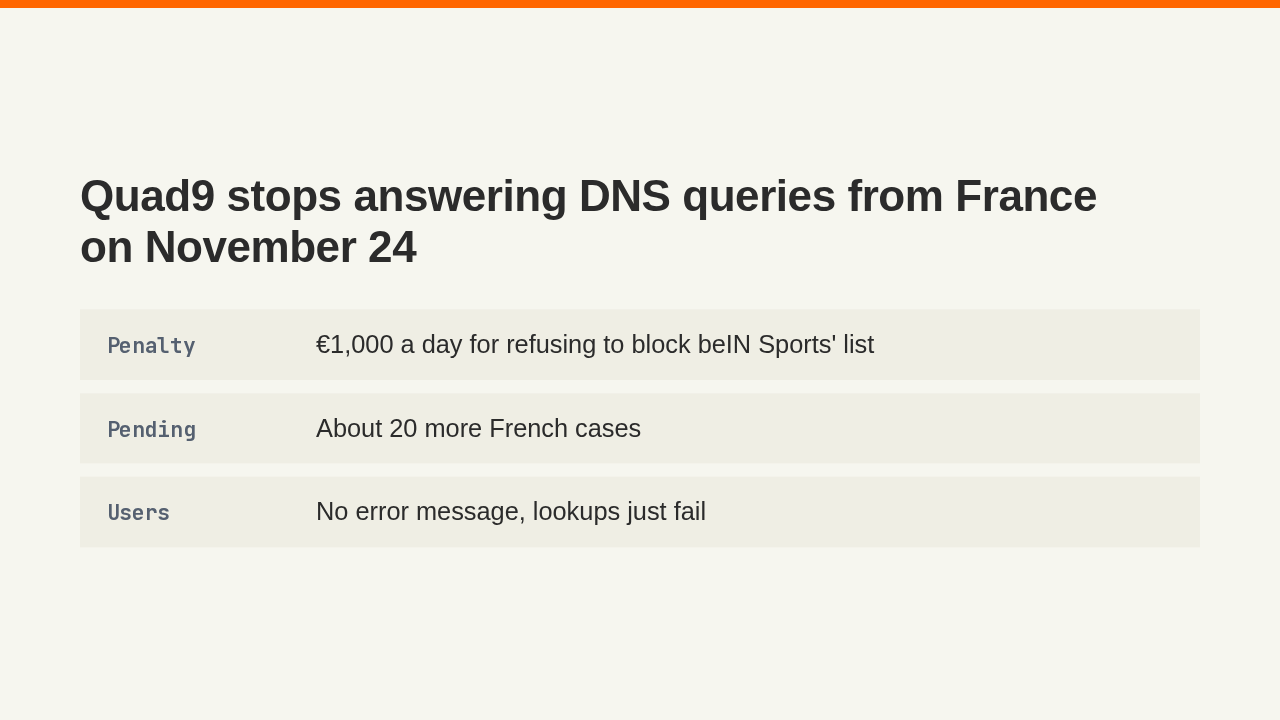
Quad9, the Swiss non-profit behind the 9.9.9.9 resolver, stops answering queries from France on Tuesday, November 24. A Paris court fined it 1,000 euros a day for refusing to block pirate streaming domains for beIN Sports, and about 20 similar cases are still pending. A device still pointed at Quad9 gets no error message after that date. Names just stop resolving. Mullvad Browser now defaults to Quad9 too, so if you run machines in France on it, move them to another resolver before the 24th.
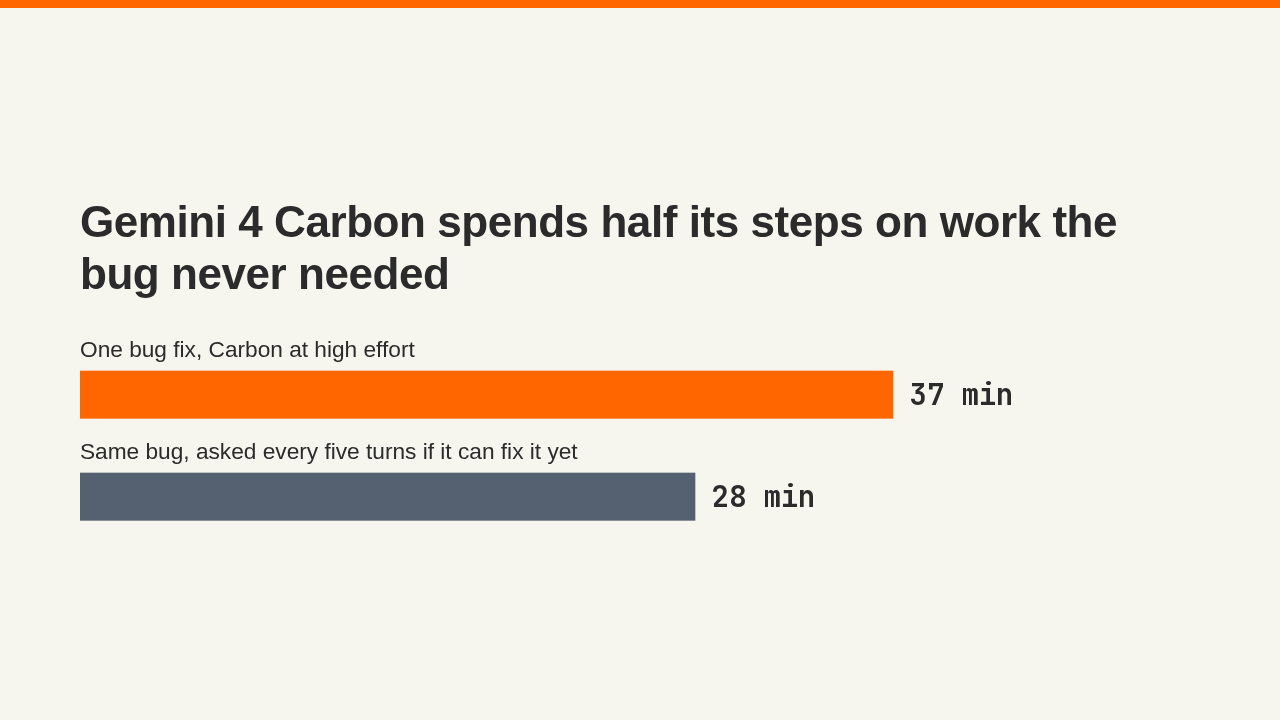
On hard bug fixes, Gemini 4 Carbon takes nearly an hour where Opus 5.5 and GPT-6 Astra take minutes. Slower inference explains part of that. About half of Carbon's steps go to auditing code the fix never touches and guarding against cases the bug report already ruled out. A harness that asks it every five turns whether it has enough to make the fix cut one run from 37 minutes to 28. In the thread, bagacrap counts that extra auditing as a feature, because it flags bugs in far-off code.
Up next
 3:27
Ruby2ßhell runs code on stock Rails before login, and a JVM fix waited two months
@hacker-news
5 hours ago
 4:15
Optimizely served malware on Zoom and GitLab, and Windows 11 logs your coding agents
@hacker-news
2 days ago
 4:10
uBlock Origin fixes a one-click XSS, ParadeDB joins, and free CMU courses
@hacker-news
2 days ago
 4:01
All AI code should be open source, and a chlorine alarm lost in a Microsoft 365 outage
@hacker-news
2 days ago
 4:19
Lovable apps leak passports, ggml hits 1.0, and Qwen3.8 27B fits a 24 GB Mac
@hacker-news
5 days ago
 3:43
Edge0-145B runs on one 16 GB NVIDIA card, and Brave sells search to AI agents
@hacker-news
6 days ago
 4:20
Apache’s HTTP/2 bug lets anyone run code, and Gemini 4 Hydrogen replaces Flash
@hacker-news
1 week ago
 4:01
AWS Emulator puts AWS on your laptop, and Apple's Harbor pools Macs for AI
@hacker-news
1 week ago
 3:40
Claude Fable 5.2 gets cheaper, and Amazon swaps Sonnet for Strands Decider
@hacker-news
1 week ago
 3:37
Claude Fable 5.2 runs faster for less, a number plate unlocks cars, and a $385 Raspberry Pi
@hacker-news
1 week ago
 4:15
Pi replaces Claude Code, Goldman cuts its traders off, and DeepSeek fits in 64 GB
@hacker-news
1 week ago
 4:12
Libghostty 1.0 is stable, your Mac maps your family, and Discord drops Electron
@hacker-news
1 week ago