Grok Bot inference hooks let your security server block a prompt before the model sees it
3 weeks ago
Grok Bot inference hooks send each model request, signed, to your organization's AI security server, which allows or denies it before the model runs. A beta for every Enterprise team: Shadow mode, fail-open or fail-closed modes, what blocked members see, and what the hook doesn't cover. Plus Pages, and Apply to MCP servers for the network allowlist. https://docs.x.ai/grok-bot/inference-hooks https://docs.x.ai/grok-bot/security https://docs.x.ai/grok-bot/files-and-results https://docs.x.ai/grok-bot/teams-and-enterprises https://docs.x.ai/developers/release-notes.md
Ask about this presentation
Chapters
Show transcriptHide transcript
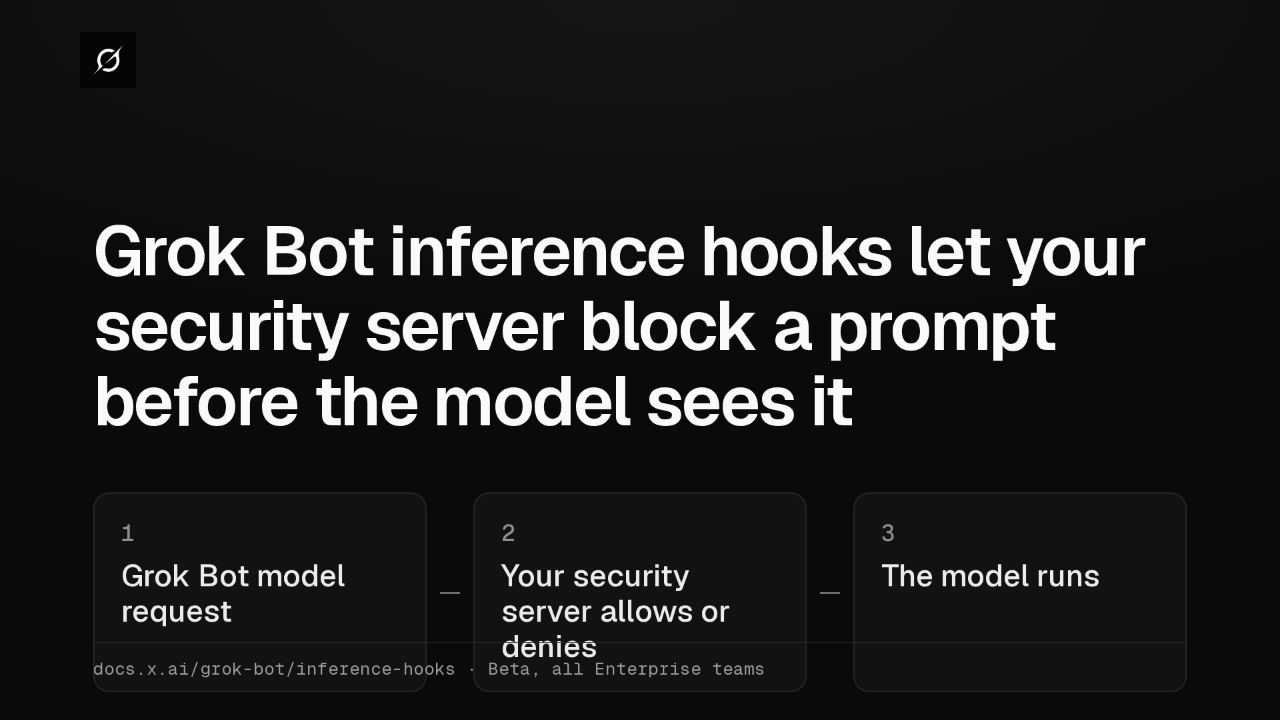
Grok Bot can now send each model request to your organization's AI security server. The request is signed, and your server allows or denies it before the model runs. It's a beta for every Enterprise team.
Slide text

Grok Bot inference hooks let your security server block a prompt before the model sees it
1 Grok Bot model request2 Your security server allows or denies3 The model runsdocs.x.ai/grok-bot/inference-hooks · Beta, all Enterprise teamsThe check covers what the Bot picks up, as well as what members type. Web pages, app results and command output reach your server before the next model call, so your data loss policy can stop them.
Slide text
Web pages and app results get checked too
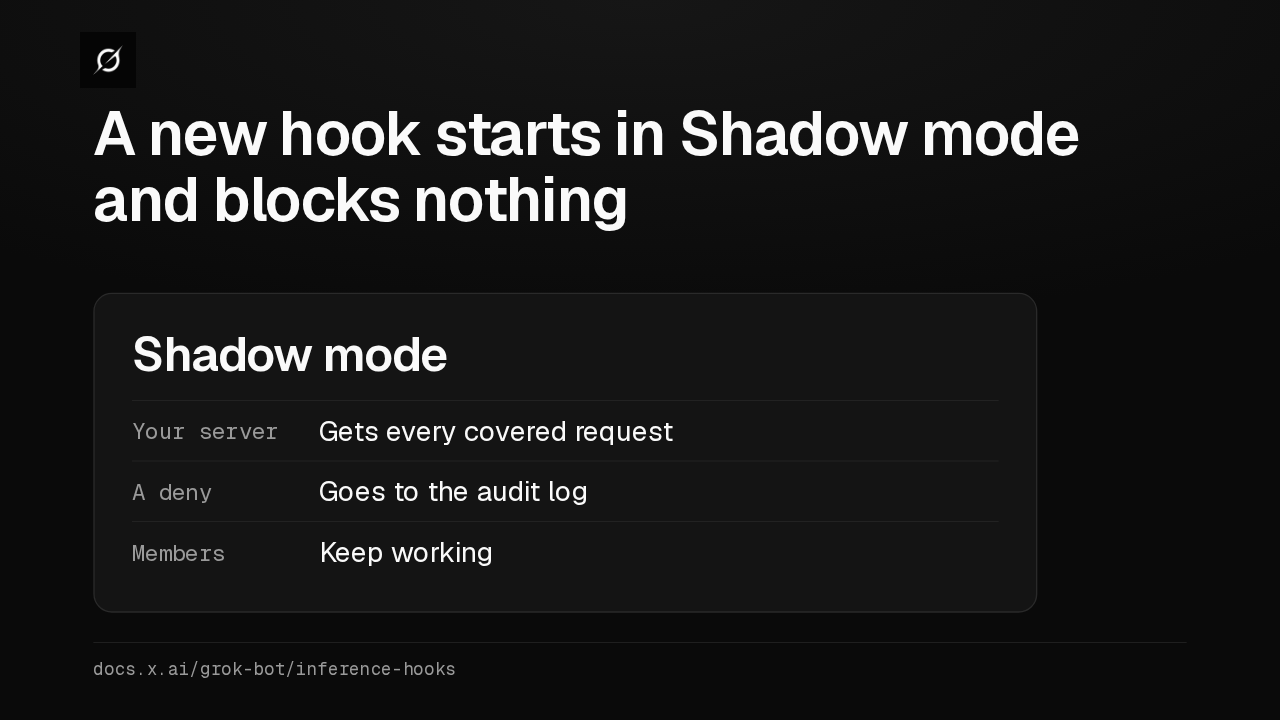
Prompts Web pages App results Command outputdocs.x.ai/grok-bot/securityA new configuration starts in Shadow mode. Your server sees every covered request and denials go to the audit log, while members keep working. Their conversations still reach your server, so tell members first.
Slide text
A new hook starts in Shadow mode and blocks nothing
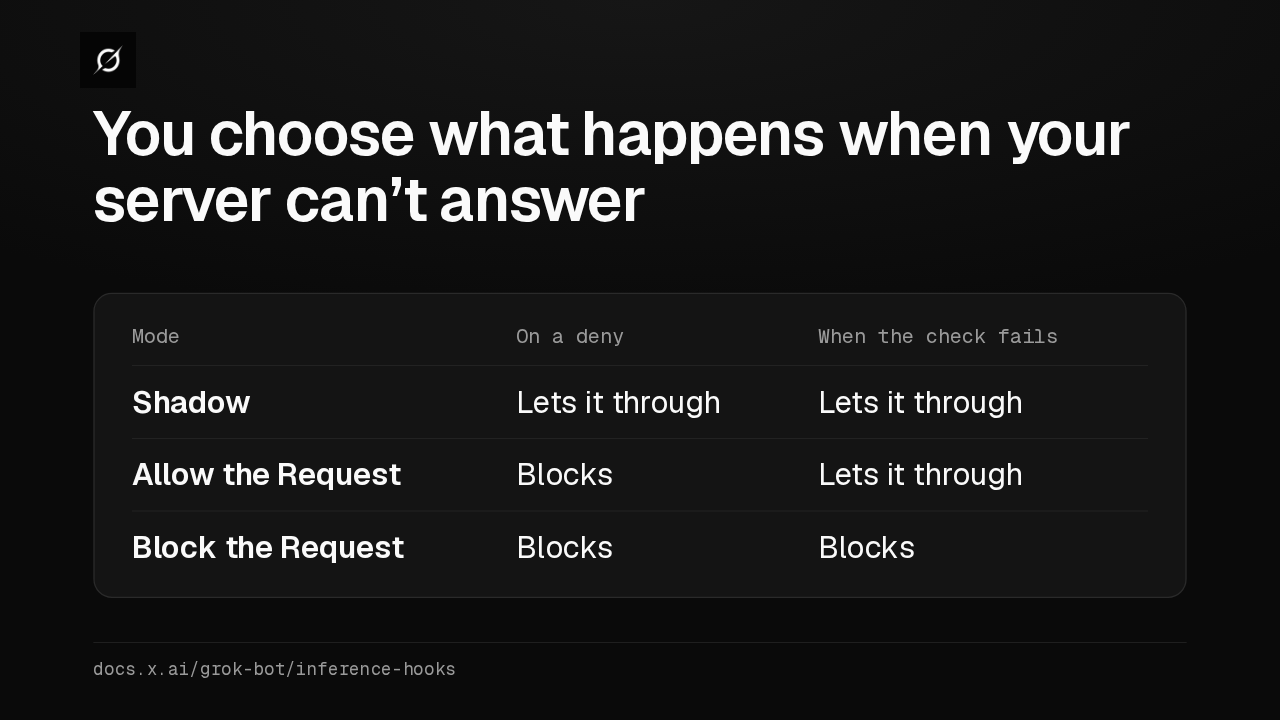
Shadow modeYour server Gets every covered requestA deny Goes to the audit logMembers Keep workingdocs.x.ai/grok-bot/inference-hooksOnce the verdicts look right, you pick a mode. Allow the Request lets traffic through when your server times out or errors, and Block the Request stops it. A failure never counts as a deny.
Slide text
You choose what happens when your server can’t answer
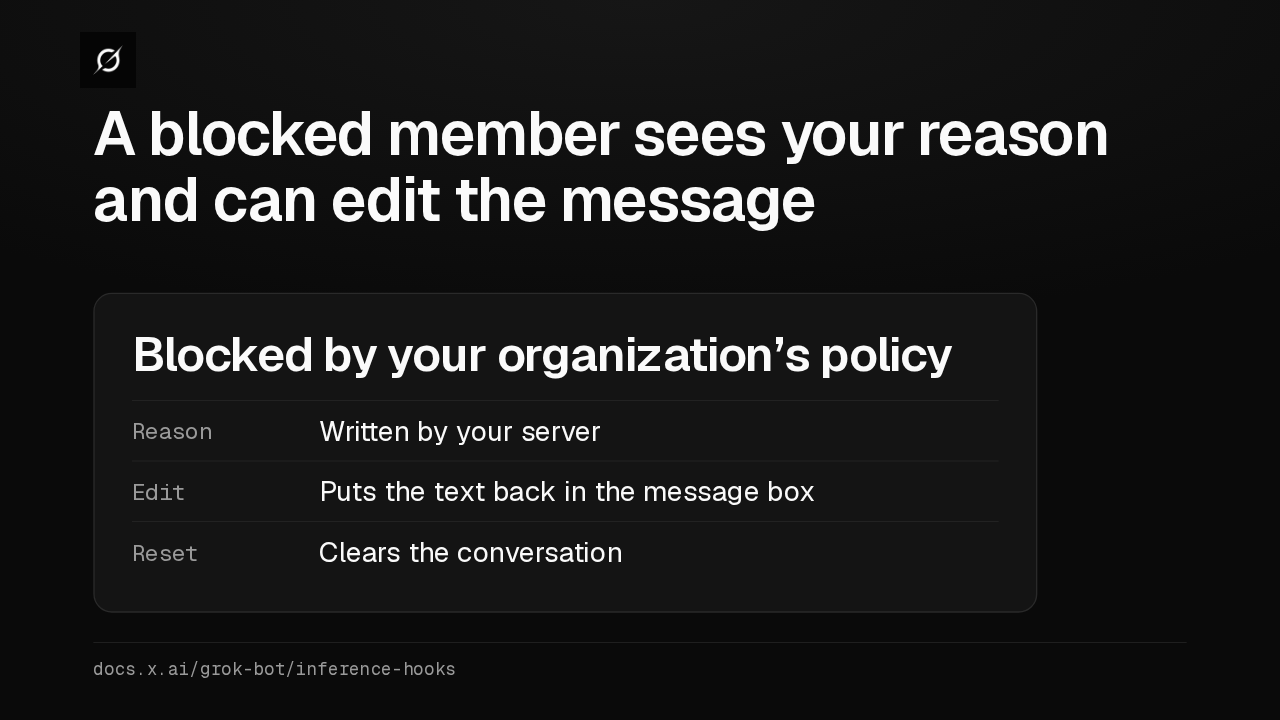
Mode On a deny When the check failsShadow Lets it through Lets it throughAllow the Request Blocks Lets it throughBlock the Request Blocks Blocksdocs.x.ai/grok-bot/inference-hooksOn a deny, the sender sees Blocked by your organization's policy, with your server's reason. Edit puts the text back so they can send something different, and Reset clears the conversation.
Slide text
A blocked member sees your reason and can edit the message
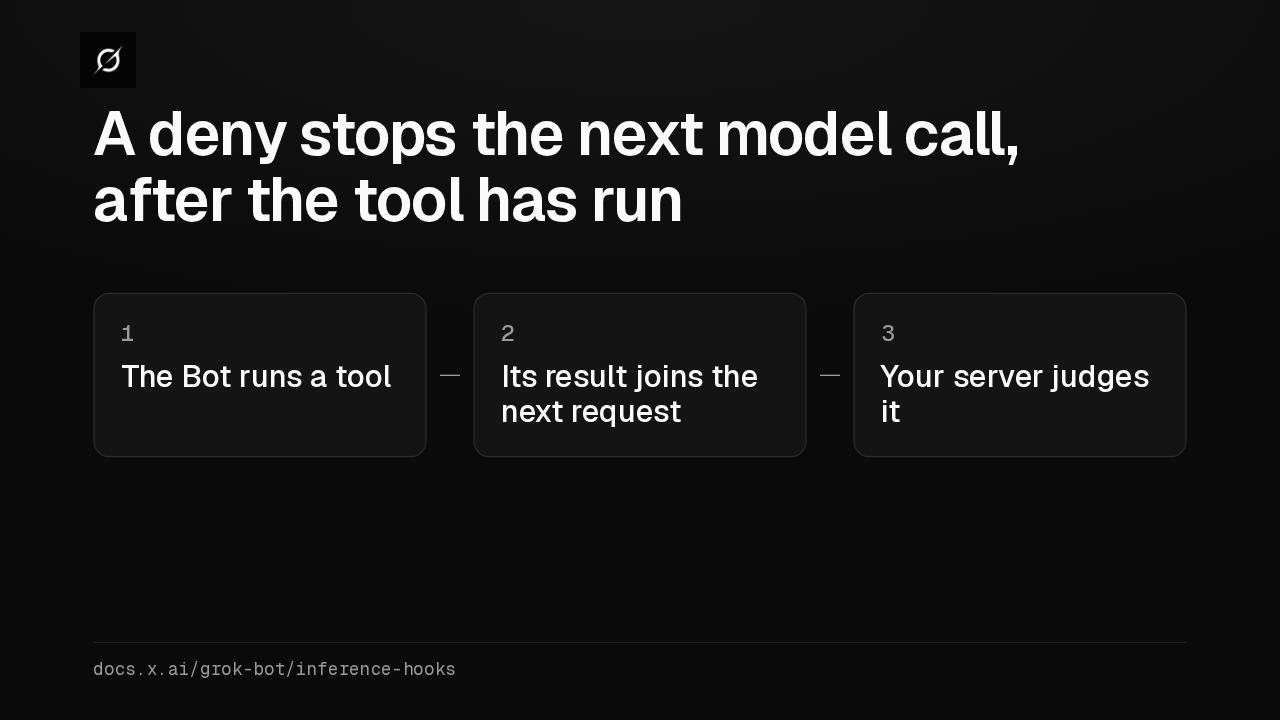
Blocked by your organization’s policyReason Written by your serverEdit Puts the text back in the message boxReset Clears the conversationdocs.x.ai/grok-bot/inference-hooksA tool call reaches your server only after it has run, and that includes the Bot's replies to members. So a deny stops the next model call. Keep the network policy and Auto Review in place to control actions.
Slide text
A deny stops the next model call, after the tool has run
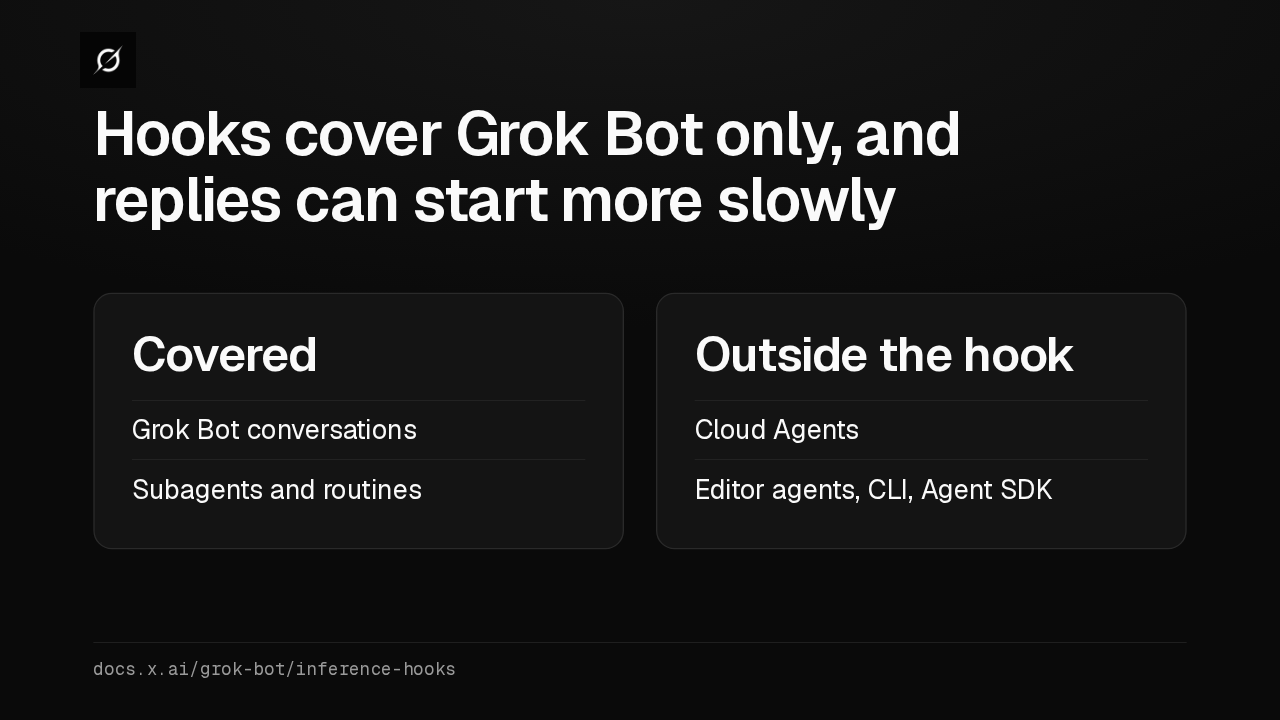
1 The Bot runs a tool2 Its result joins the next request3 Your server judges itdocs.x.ai/grok-bot/inference-hooksCoverage stops at Grok Bot. Cloud Agents, editor agents, the CLI and the Agent SDK go to the model unchecked. And with a hook on, Grok Bot skips some early model calls, so replies can start more slowly.
Slide text
Hooks cover Grok Bot only, and replies can start more slowly
CoveredGrok Bot conversationsSubagents and routinesOutside the hookCloud AgentsEditor agents, CLI, Agent SDKdocs.x.ai/grok-bot/inference-hooksA Page is a styled report, dashboard or tracker the Bot builds, like signups for the last 30 days. Self-serve plans can share one publicly, Enterprise plans with chosen people and teams, and routines can keep it updated.
Slide text
Your Bot can now build a Page you can share
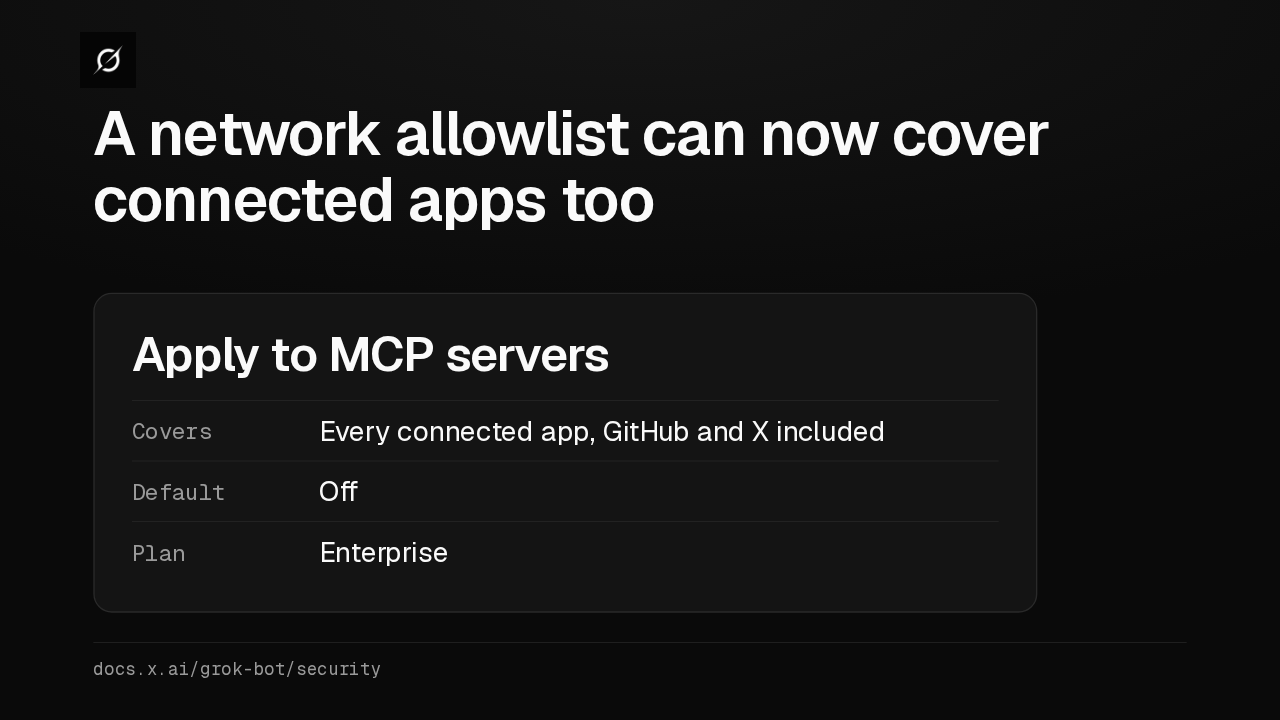
Reports Dashboards Trackers Charts and heat mapsdocs.x.ai/grok-bot/files-and-resultsGrok Bot reaches connected apps from Cursor's servers, so a network allowlist alone misses them. Turn on Apply to MCP servers and every app, GitHub and X included, must match an allowed host. It's off by default.
Slide text
A network allowlist can now cover connected apps too
Apply to MCP serversCovers Every connected app, GitHub and X includedDefault OffPlan Enterprisedocs.x.ai/grok-bot/securitySetup steps, the request format and the audit events are in the Grok Bot inference hooks guide. Which security server would your team point Grok Bot at?
Slide text
Which security server would your team point Grok Bot at?
Setup guide: Grok Bot inference hooksdocs.x.ai/grok-bot/inference-hooks
Up next
 1:52
Grok Bot's Vault lets Bots sign in and pay without seeing your passwords
@grok-bot
1 day ago
 1:06
Grok Bot now acts only as you, and keeps your passwords out of the model
@grok-bot
1 day ago
 2:29
Grok Bot now signs in with Okta FastPass on its own computers
@grok-bot
2 days ago
 2:19
Grok Bot now shares one Bot with your whole team, in Slack and Teams
@grok-bot
2 days ago
 1:59
Grok Bot Team Bots now learn for the team and join Microsoft Teams
@grok-bot
3 days ago
 1:56
Grok Bot buys your conference pass from memory and asks before it emails finance
@grok-bot
1 week ago
 1:04
Grok Bot now shuts idle computers after 30 days without a message
@grok-bot
1 week ago
 1:58
Grok Bot admins can now wipe a member's Bots and data in one step
@grok-bot
3 weeks ago
 1:47
Grok Bot lets Enterprise team admins recreate or terminate Bot computers in bulk
@grok-bot
1 month ago
 2:52
Grok Bot now deploys to your whole organization with Jamf, Intune and Ansible
@grok-bot
1 month ago
 1:19
Grok Bot plugins now install from Connect apps
@grok-bot
1 month ago
 1:43
Grok Bot Team Bots get managers, and Bots can read X
@grok-bot
1 month ago