Linux’s TCP bug can root Go servers, one ChatGPT link took your account, and HackerTube
1 hour ago
A Linux bug in the TCP handshake reaches the kernel before any login, Claude built a root exploit for it, and Ubuntu and RHEL have no fixed kernel yet. Also from Saturday's Hacker News front page: a ChatGPT share link that could take over the account that opened it, cfsolve's Cloudflare Turnstile solver, and Andrej Karpathy's HackerTube. TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8, by Atlas Security https://atlasum.net/blog/cve-2026-98432-linux-ipv4-tcp-uaf Discussion: https://news.ycombinator.com/item?id=50319143 Do the math: How we took over ChatGPT accounts, by Mukul Goyal at Parameter https://www.parameter.ai/labs/we-found-a-gap-at-openai Discussion: https://news.ycombinator.com/item?id=50314699 yellow_lead on the $5,000 bounty: https://news.ycombinator.com/item?id=50315474 Cloudflare Turnstile solver library (no headless browser required) https://github.com/chris124567/cfsolve Discussion: https://news.ycombinator.com/item?id=50277379 costco, the author, on European proxies: https://news.ycombinator.com/item?id=50311942 manofmanysmiles on bypassing at scale: https://news.ycombinator.com/item?id=50312421 HackerTube: YouTube built from videos recommended by HN, by Andrej Karpathy https://karpathy.bearblog.dev/hacker-tube/ Discussion: https://news.ycombinator.com/item?id=50319510 reorder9695 on the front page against YouTube's feed: https://news.ycombinator.com/item?id=50319961 The front page that day: https://news.ycombinator.com/front?day=2026-10-31
Ask about this presentation
Chapters
Show transcriptHide transcript
On Saturday's HN front page, the story for anyone who runs servers is a use-after-free in Linux's IPv4 TCP handshake. It sits in code every Linux server runs when it accepts a connection, before your application sees anything, and the attacker needs no login. It goes back to Linux 4.4, and it scores near the top of the severity scale. Upstream fixed it with a four-line change, in stable kernels released between October 11 and 15.
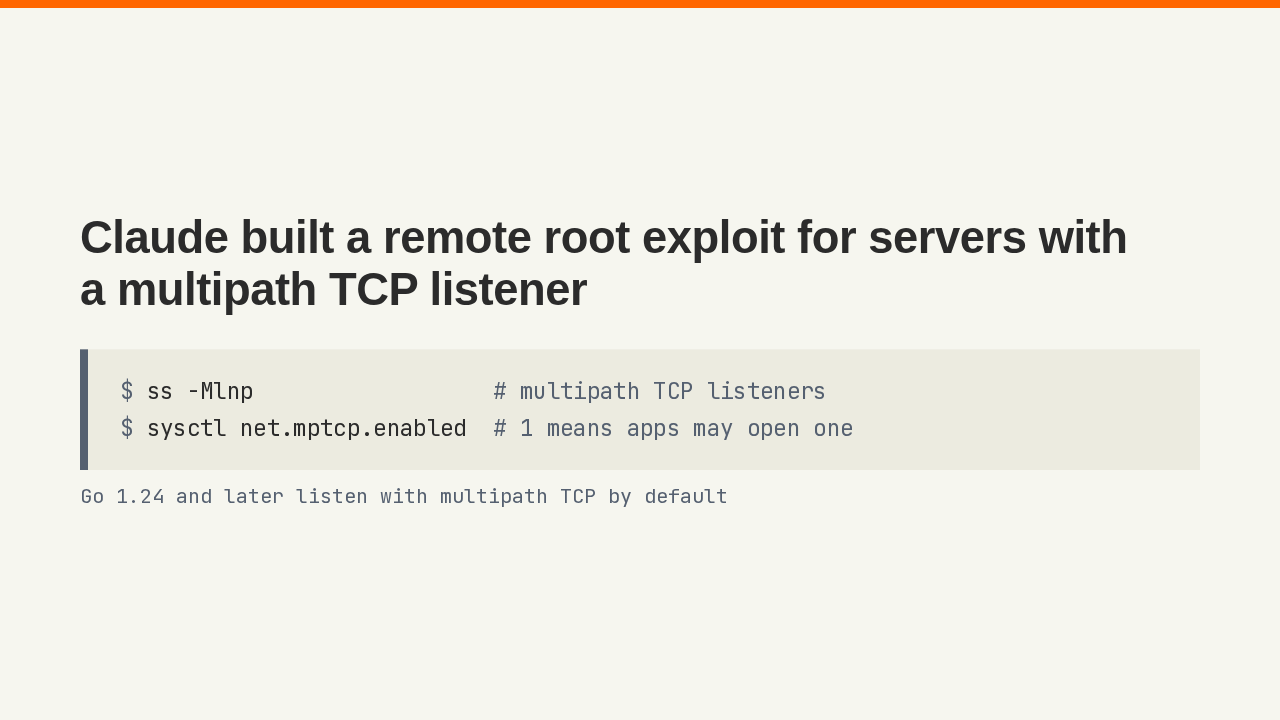
Anthropic's Claude wrote a working exploit that runs commands as root, with no credentials, on Linux servers with a multipath TCP listener. In the lab it leaked a kernel pointer in about 48 minutes and reached a shell five minutes later. The exploit is unpublished. Programs built with Go 1.24 or later open that kind of listener by default. These two commands show whether a host has one. Run them on the host itself, because a container uses the host's kernel.
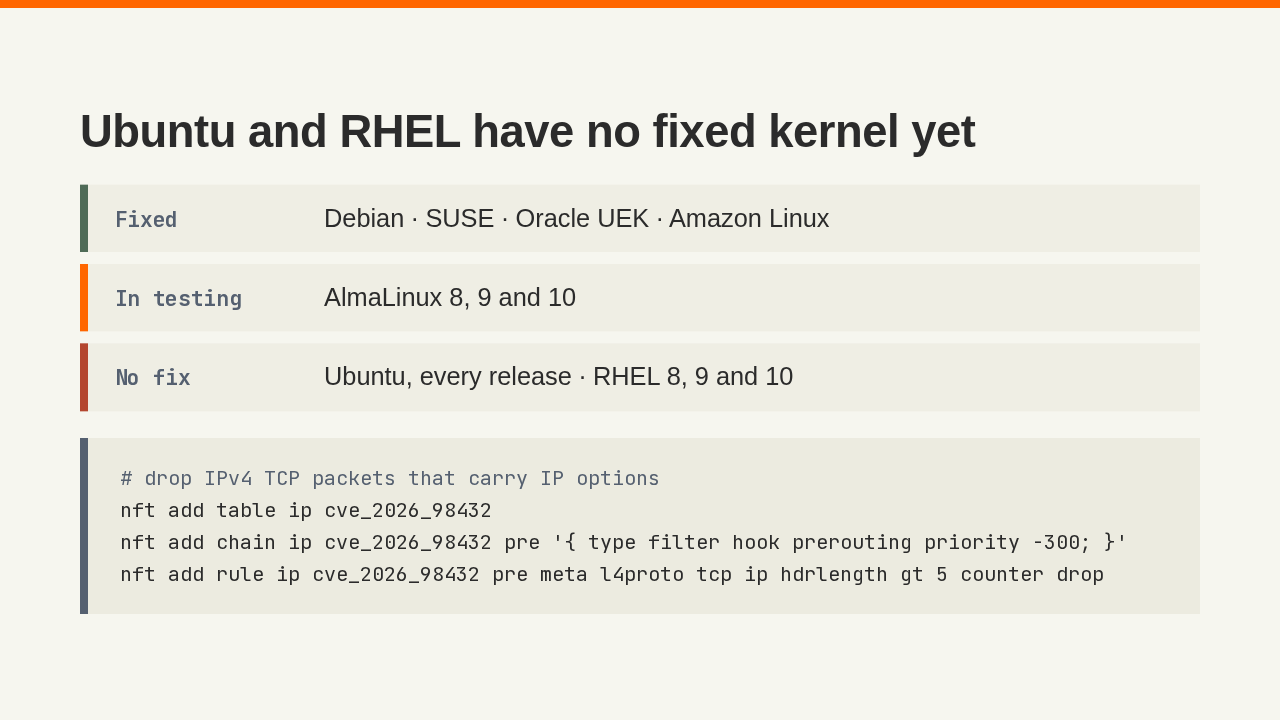
Debian, SUSE, Oracle and Amazon Linux ship fixed kernels, and a fix only takes effect after a reboot. Ubuntu and Red Hat Enterprise Linux are still waiting. Until they ship, drop incoming TCP packets that carry IPv4 options, which ordinary traffic almost never uses. This nftables rule does that. It narrows the exposure without fixing the kernel. If I ran Go services on Ubuntu, I would add this rule and turn off multipath TCP now, rather than wait for the kernel.
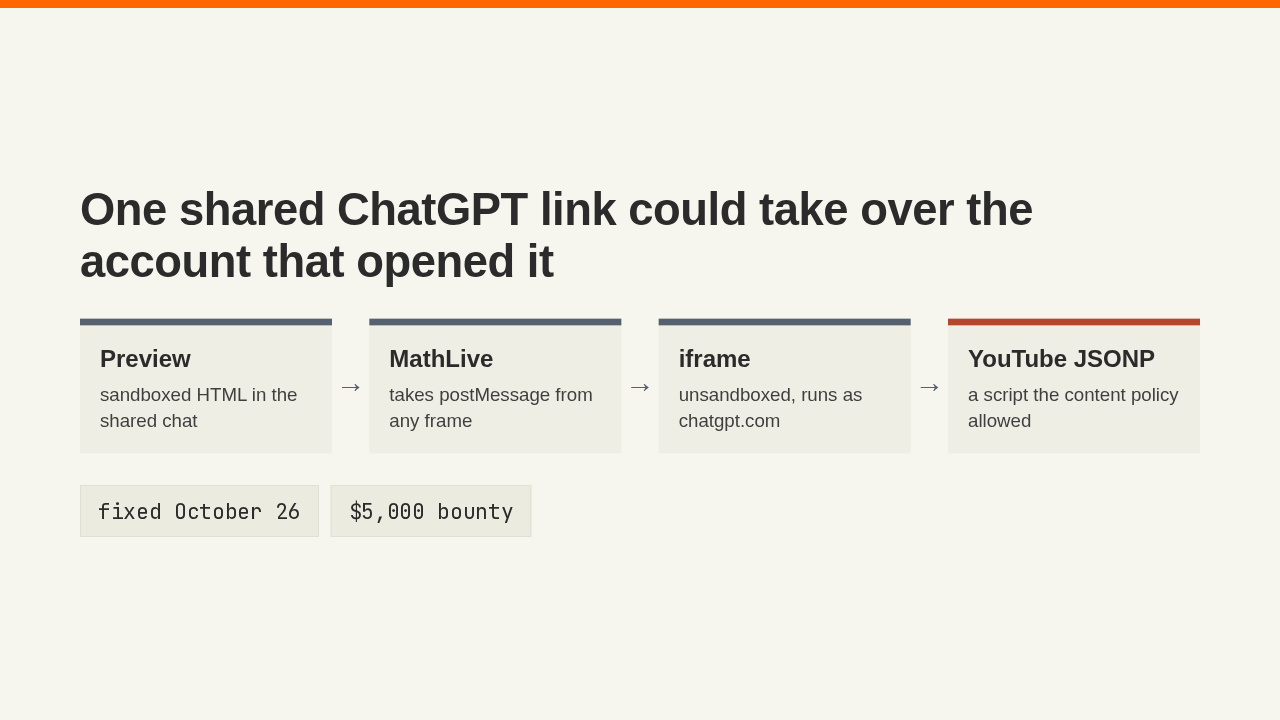
Researchers at Parameter turned a public ChatGPT share into JavaScript running in the signed-in session of whoever opened it. It could list your chats, read a private one and send it off-site. The Preview sandbox held. But a graph had loaded a math library called MathLive, which accepted messages from any frame and rendered the HTML inside them. That HTML opened an unsandboxed frame, and a YouTube endpoint the page's security policy allowed ran the script. If your page listens for postMessage, check the sender, and never take raw HTML from it. OpenAI fixed it on October 26 and paid 5,000 dollars, which yellow_lead in the thread calls very low.
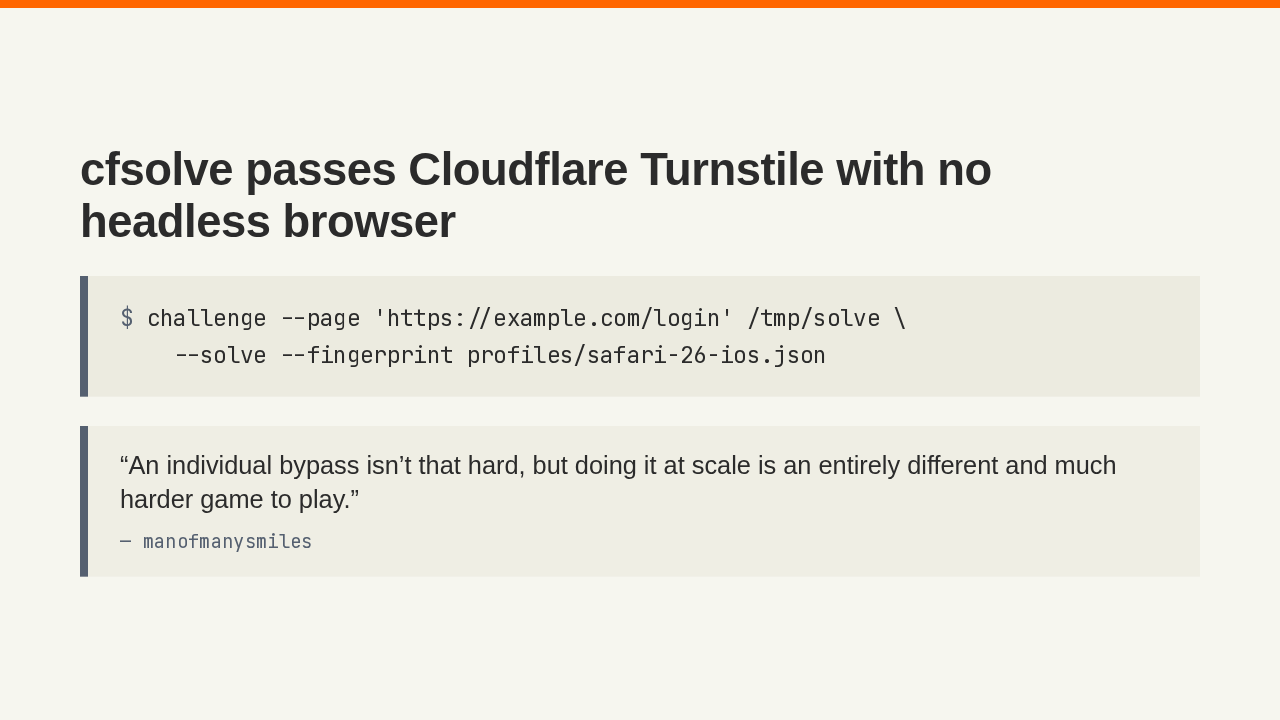
cfsolve is a Rust library and command line tool that hands back a Turnstile token, or the clearance cookie for a challenge page, with no browser running. It impersonates one recorded browser, Safari on iPhone, from a profile file. Its author, costco, wrote in the thread that it failed for one user on European proxies, and that Cloudflare constantly changes things. manofmanysmiles, who built something similar a year ago, says it worked until it didn't, because Cloudflare looks for patterns across its whole network.
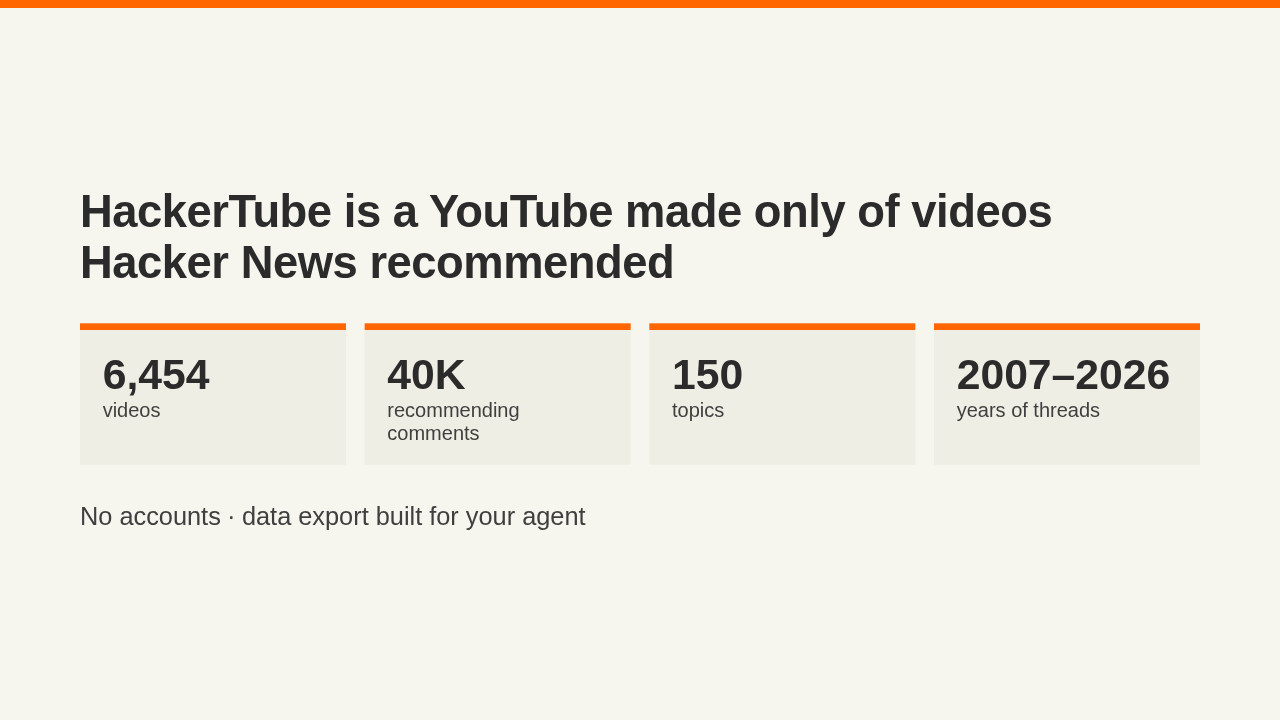
Andrej Karpathy had Claude Opus 5.5 build HackerTube in about two hours. Opus pulled every Hacker News comment, ran Sonnet over them to cut spam, and kept about 40,000 that recommend a YouTube video. That comes to nearly 6,500 videos across 150 topics. There are no accounts, and your recommendations stay in your browser. The whole dataset downloads as a zip with a guide written for coding agents, so you can build your own version. reorder9695 finds its front page closer to what they want to watch than YouTube's personalised feed.
Up next
 3:13
Anthropic files its S-1, coding agents cost up to 75% less to run, and Microsoft offers 60,000 buyouts
@hacker-news · 5 days ago
 3:50
Goose outruns safe Rust with no heap, and a 2015 CNN beats GPT-6 Astra at skin cancer
@hacker-news · 6 days ago
 4:10
Brotli needs patching in Node, Python and curl, Roc nears C, and uv check runs ty
@hacker-news · 1 week ago
 3:59
Claude proves 123 libraries' fuzz tests can't crash, Kimi K3.1 Pro, and Docker is weird
@hacker-news · 1 week ago
 4:04
eMudhra's CA key was 4, mitmproxy intercepts anything still trusting it, Quad9 leaves France
@hacker-news · 1 week ago
 4:04
PHP patches two RCE bugs, eMudhra’s CA key was the number 4, and LiteLLM shipped a stealer
@hacker-news · 1 week ago
 3:33
eMudhra’s one-byte CA keys, DeepSeek’s open DeepInfer engine, and WhatsApp’s hidden chatbot orders
@hacker-news · 1 week ago
 4:15
MiniMax M3.1 Flash cuts agent costs by 70%, Timestral forecasts on a CPU, and Wine reaches OpenBSD
@hacker-news · 1 week ago
 3:21
DeepSeek's $0.75 search API for agents, Lean's five-kernel proof check, and Pele
@hacker-news · 1 week ago
 3:32
DeepSeek V4.1 Flash reasons less for the same answers, llmspeed, and a web app built in Lean 4
@hacker-news · 2 weeks ago
 4:11
Claude traced NIST’s P-256 seed to a 1997 timestamp, Muse Spark Open runs on four Mac Studios, and UTC drops leap seconds
@hacker-news · 2 weeks ago
 3:37
Muse Spark Open runs on two Mac Studios, ads that deliver spyware, and a Wi-Fi bug TCP can’t see
@hacker-news · 2 weeks ago