Paste your app's URL: Perfai breaks in, then writes the fix

2 months ago

You paste your app's web address. An AI red team breaks in, finds the security holes, and writes the fix.

Ask

Ask about this presentation

Answers are generated from this presentation.

Chapters

  1. 0:00Slide 1
  2. 0:05Give it a live URL. No code, no config.
  3. 0:15Built for apps shipped fast with AI
  4. 0:22First it maps every permission. Then it attacks.
  5. 0:35Then it writes the fix into your own IDE
  6. 0:46The honest read: narrow, and day one
  7. 1:00Free to try. Ninety-nine a month for Pro.
  8. 1:13Slide 8
Show transcript

Slide 1

Paste your app's URL: Perfai breaks in, then writes the fix
It finds the security holes, and patches them.
AI red team AppSec access control

You paste your app's web address. An AI red team breaks in, finds the security holes, and writes the fix.

Give it a live URL. No code, no config.

Register an app by its URL, no source code, no configuration

You give it a live app's URL, no source code, no configuration. Its agents then act like a real attacker, probing what each user is allowed to touch. Perfai's Qutub Syed has been showing it off.

Built for apps shipped fast with AI

Works with the AI coding tools teams ship with

It's built for one moment. Teams now ship AI-built apps in an afternoon, and nobody can hand-check that every permission is right. That's where the holes hide.

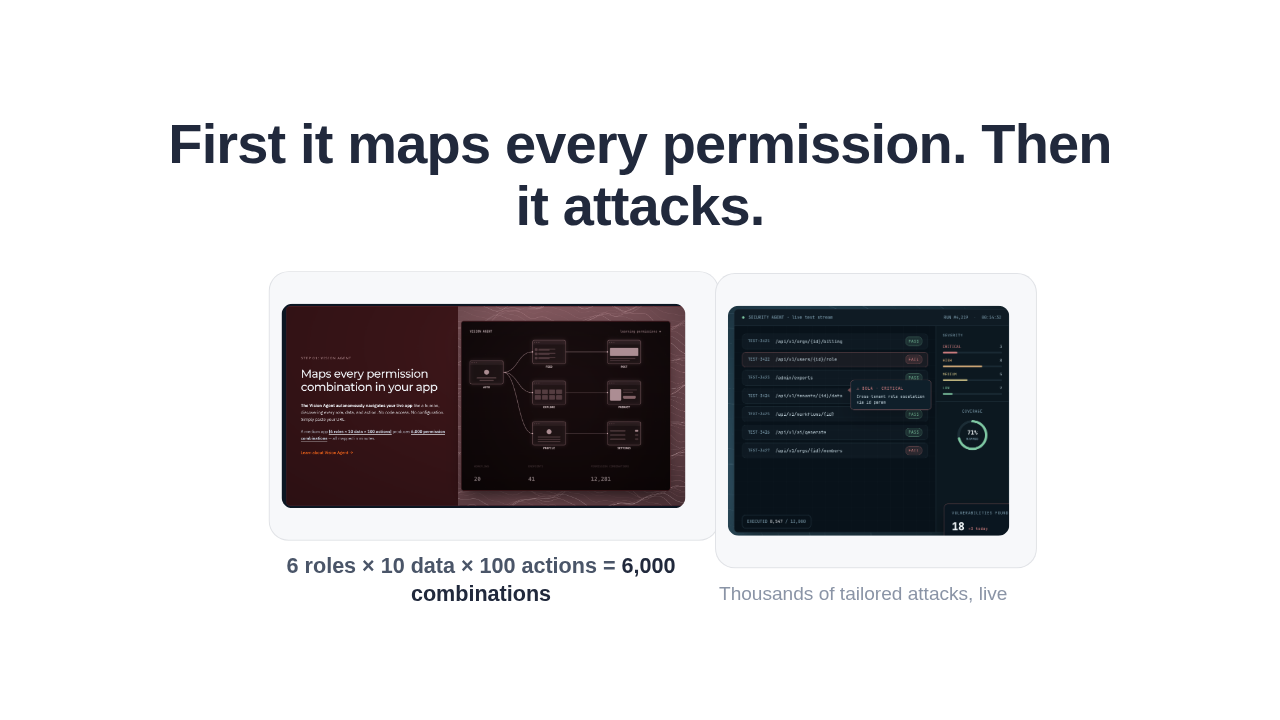
First it maps every permission. Then it attacks.

The Vision Agent permission map: roles across the top, data and actions down the side, wired into a diagram
6 roles × 10 data × 100 actions = 6,000 combinations
The Security Agent live test stream: tests firing at endpoints with pass and fail results and a critical access-control finding
Thousands of tailored attacks, live

It works in two moves. A Vision Agent walks the app and maps every role against every action. Six roles, ten data types, a hundred actions is six thousand combinations no human checks by hand. Then a Security Agent fires thousands of tailored attacks at that map.

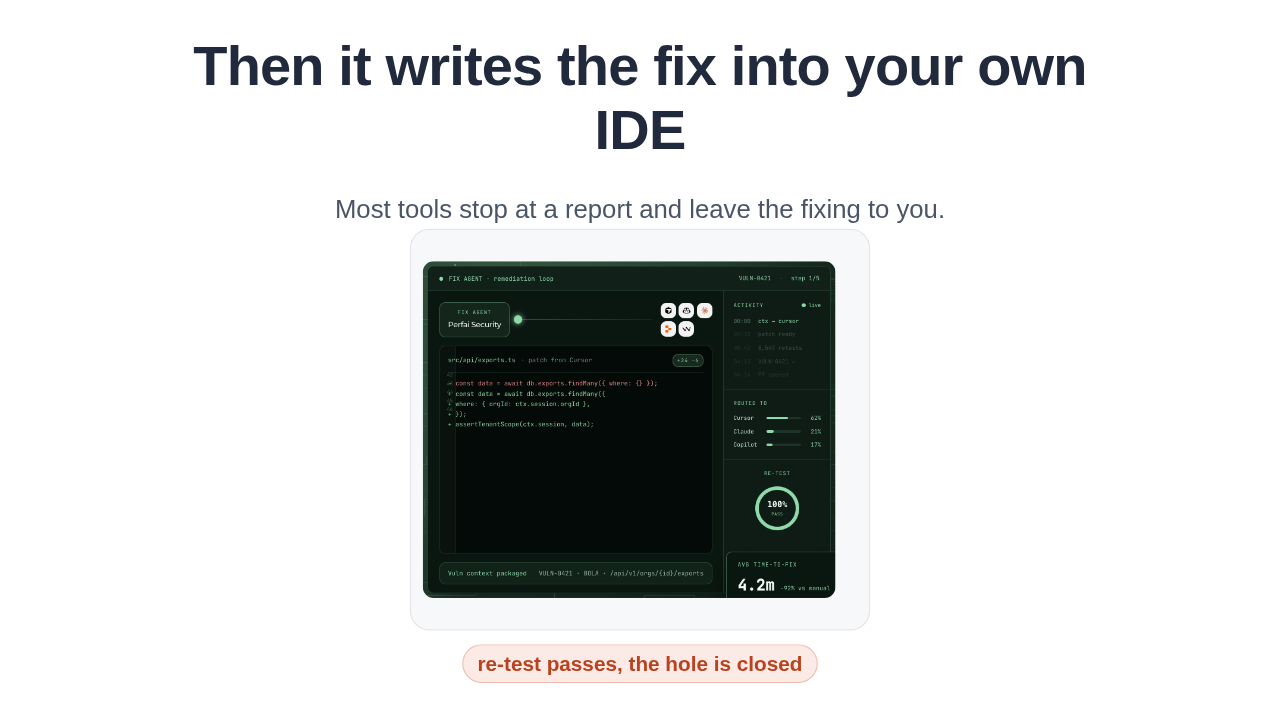
Then it writes the fix into your own IDE

Most tools stop at a report and leave the fixing to you.
The Fix Agent handing a tenant-scoping code patch to Cursor as a diff, then re-testing to a hundred percent pass and marking the vulnerability resolved
re-test passes, the hole is closed

Here's the part most tools skip. They stop at a report and leave the fixing to you. This one hands the problem and a fix plan to the AI assistant you already code with, as a ready patch. Then it re-runs every test to prove the hole is closed.

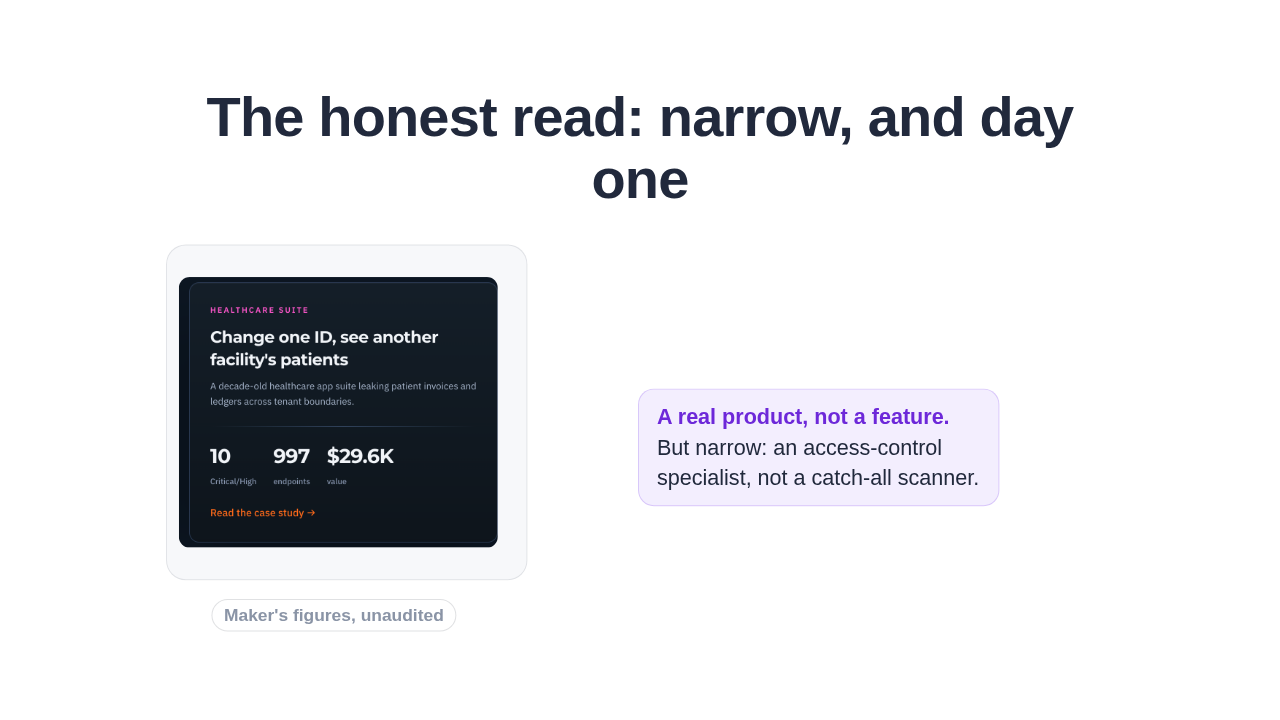
The honest read: narrow, and day one

A healthcare case card: change one ID and see another facility's patients, with ten critical findings, 997 endpoints, and a dollar value
Maker's figures, unaudited
A real product, not a feature. But narrow: an access-control specialist, not a catch-all scanner.

Now the honest read. It's a real product, not a feature, but it's narrow: an access-control specialist, not a catch-all scanner. The maker shows cases like changing one ID to see another facility's patient records. And the big savings numbers are the maker's own, day one, so take them as a claim.

Free to try. Ninety-nine a month for Pro.

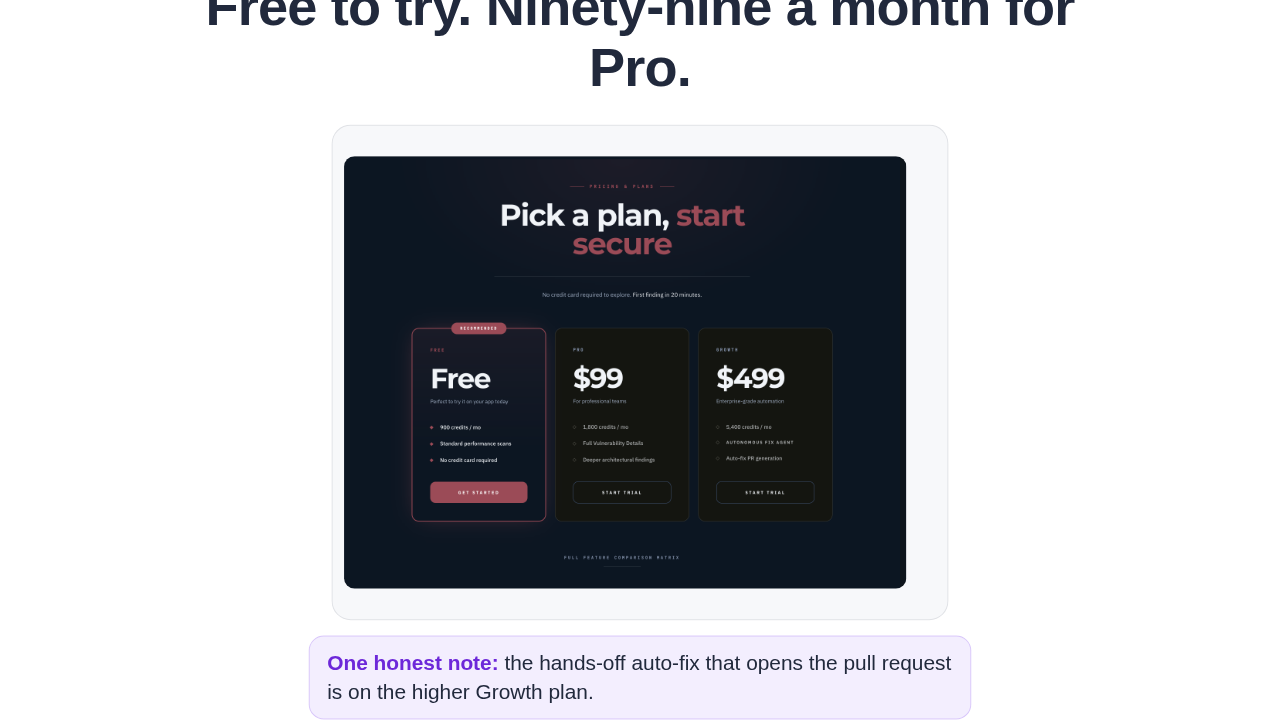
Pricing: a free tier with 900 credits a month, Pro at ninety-nine dollars, and Growth at four hundred ninety-nine dollars with an autonomous fix agent; first finding in twenty minutes
One honest note: the hands-off auto-fix that opens the pull request is on the higher Growth plan.

It's a web service. You register an app by its URL, no code needed. There's a free tier, with first findings in about twenty minutes, then ninety-nine dollars a month for Pro. One honest note: the hands-off auto-fix that opens the pull request lives on the higher Growth plan.

Slide 8

If you're shipping AI-built apps, let it break in before someone else does.
perfai.ai

So if you're shipping apps built with AI, this is the tool that breaks in before someone else does.