A Kasa Camera Answered One Packet With Its Owner's Location
A single unauthenticated packet to a Kasa Spot EC71 camera came back with the owner's precise home coordinates. It's patched now. The interesting part is how long it lasted.
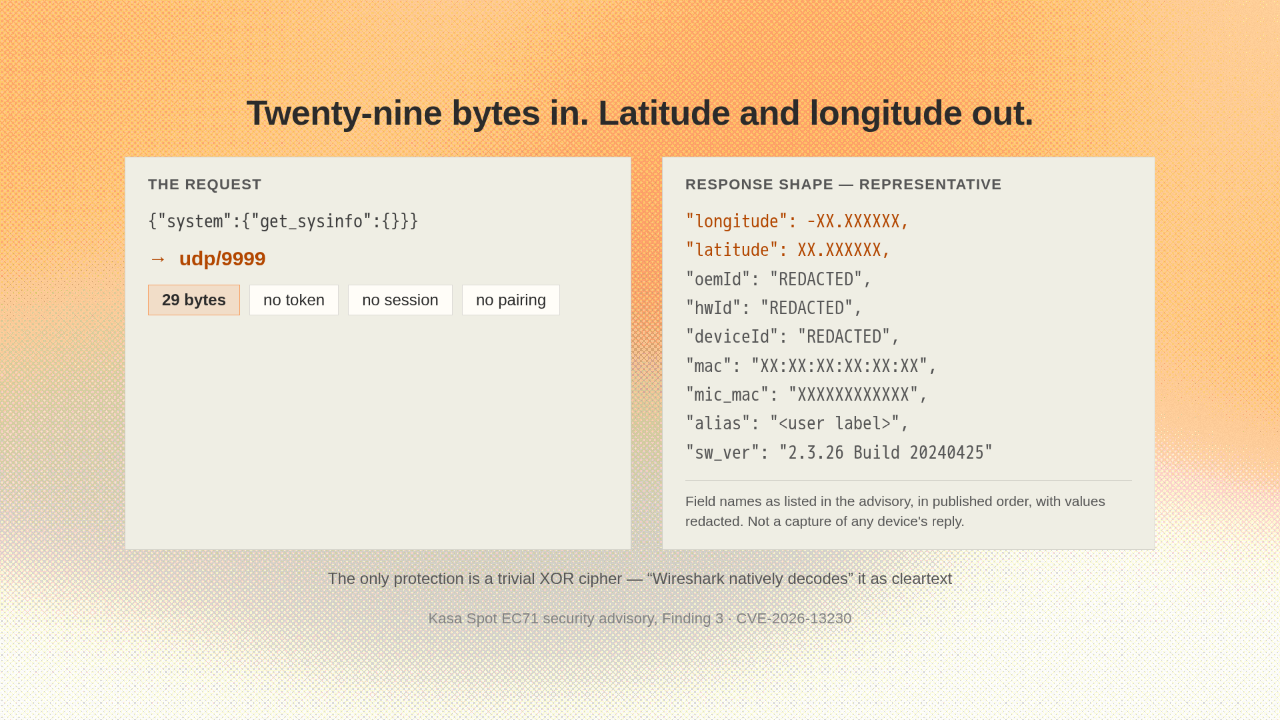
Twenty-nine bytes in. Latitude and longitude out.
"latitude": XX.XXXXXX,
"oemId": "REDACTED",
"hwId": "REDACTED",
"deviceId": "REDACTED",
"mac": "XX:XX:XX:XX:XX:XX",
"mic_mac": "XXXXXXXXXXXX",
"alias": "<user label>",
"sw_ver": "2.3.26 Build 20240425"
The request is twenty-nine bytes, sent to port nine nine nine nine. No token, no session, no pairing. What comes back is a JSON blob carrying the owner's longitude and latitude. The only protection is a trivial XOR cipher that Wireshark reads as cleartext.
But it only works from inside your network.
There's a fair objection, and early reactions raised it quickly. This only works from inside the local network. If someone's already on your Wi-Fi, they arguably know where you live.
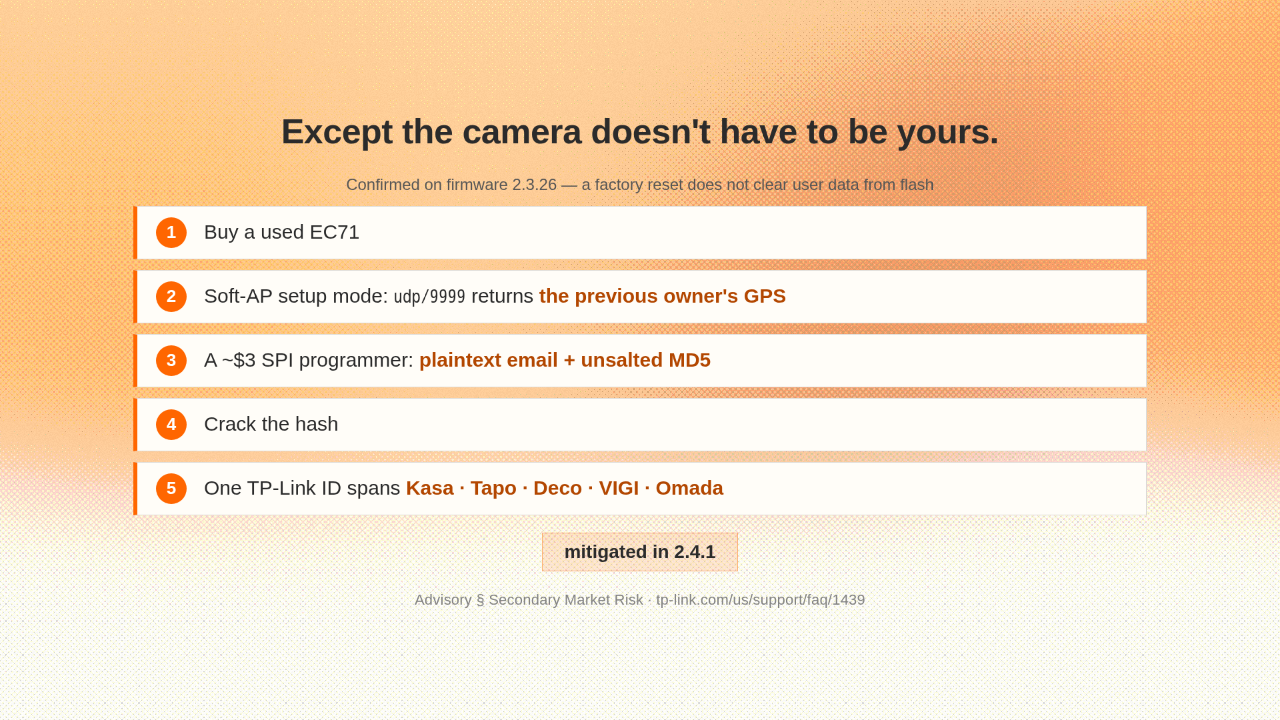
Except the camera doesn't have to be yours.
udp/9999 returns
the previous owner's GPS
Except the camera doesn't have to be yours. A factory reset didn't clear the user data. Buy a used one, send the same packet, and it returns the previous owner's coordinates. A three dollar programmer then pulls their account email and an unsalted MD5 of their password. And that login covers Tapo, Deco, VIGI and Omada. All of it is fixed in current firmware.
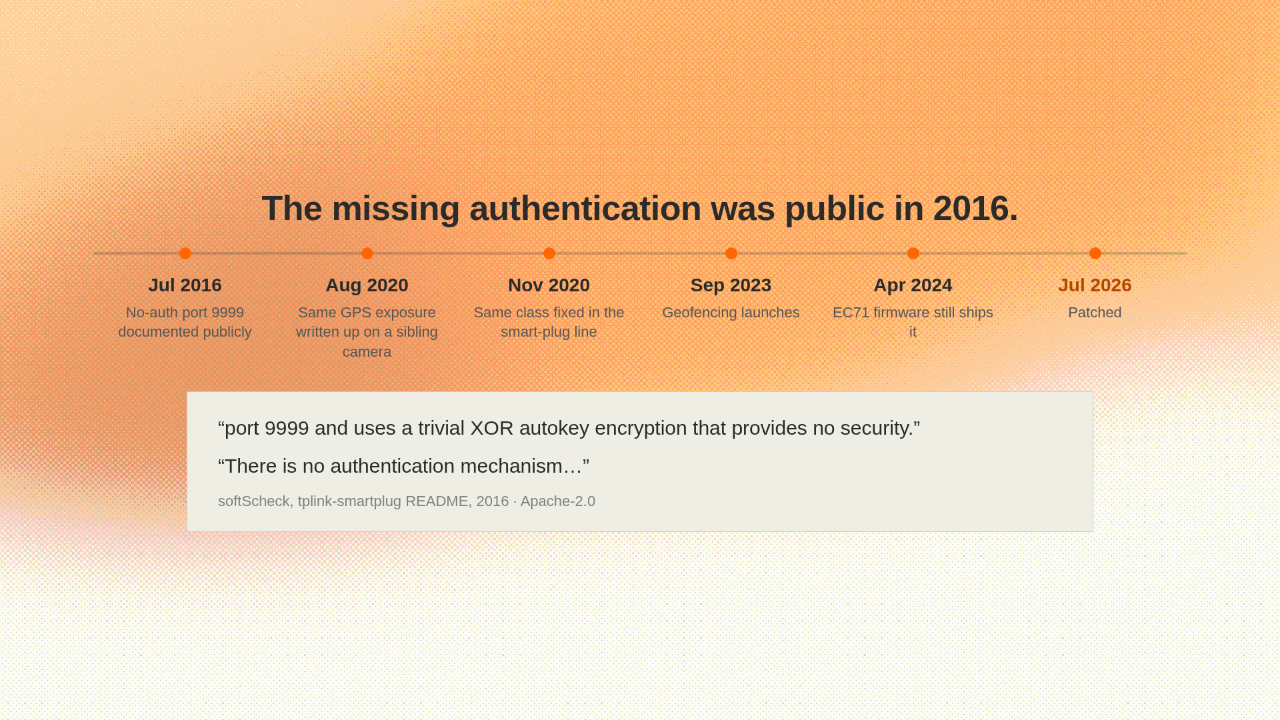
The missing authentication was public in 2016.
None of this was secret. In twenty sixteen, a reverse-engineering write-up documented the same port, the same trivial cipher, and no authentication mechanism at all. What followed, the advisory says, was targeted, incremental remediation rather than a comprehensive architectural review. The smart plug line lost its local interface in twenty twenty. Camera firmware built in April twenty twenty-four still shipped the behaviour.
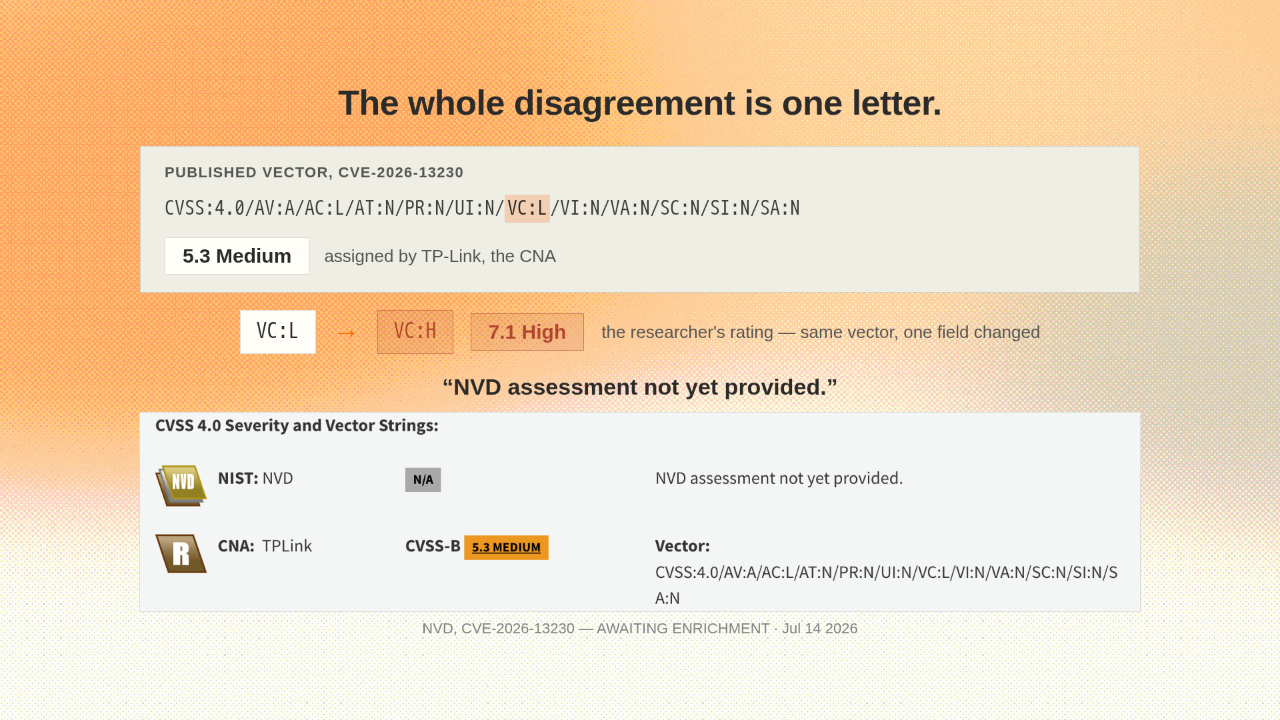
The whole disagreement is one letter.

The two sides scored it differently, and the gap is one value. TP-Link rated the location leak five point three, medium, calling the confidentiality impact low. Flip that one field to high, leave the rest of the vector alone, and the formula returns seven point one, the researcher's number. The national vulnerability database's own assessment, in its own words, is not yet provided.
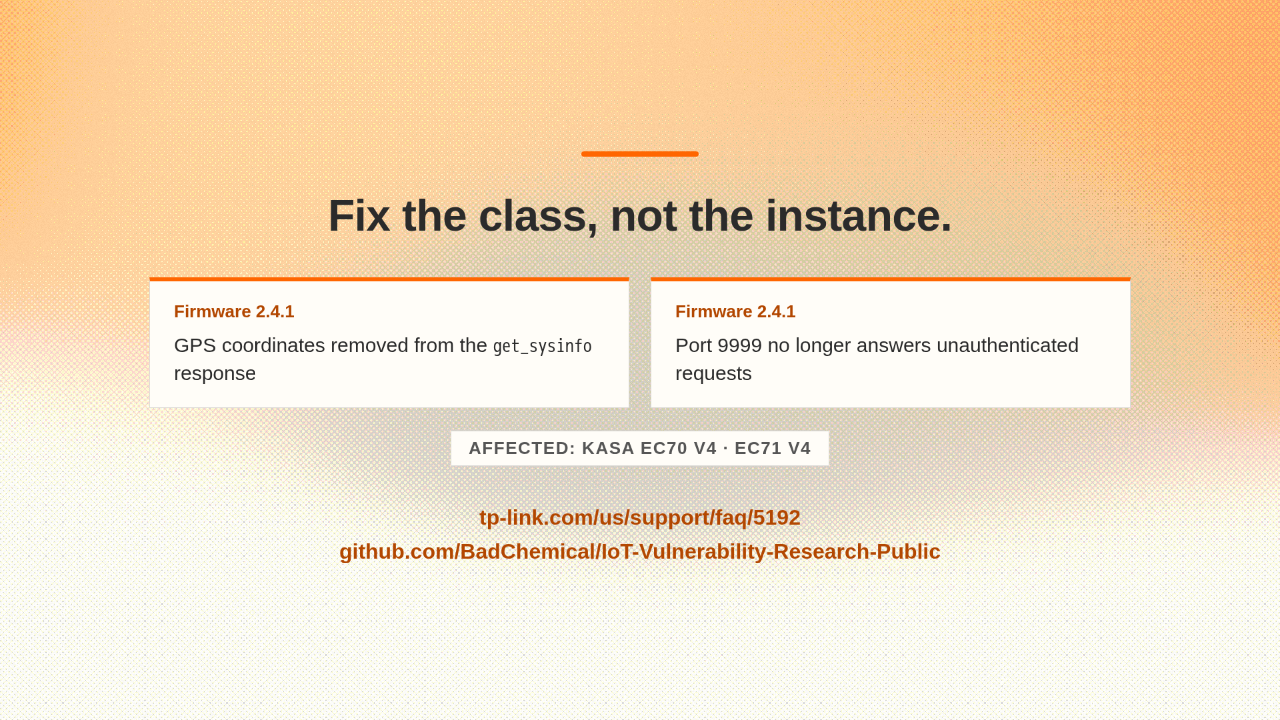
Fix the class, not the instance.
get_sysinfo response
github.com/BadChemical/IoT-Vulnerability-Research-Public
Current firmware removes the coordinates and stops the port answering unauthenticated requests. The part worth keeping isn't the camera. It's the difference between fixing an instance and fixing a class.