A Self-Spreading Worm Got Into the Code Behind Billions of Installs

2 months ago

Almost every app is built from thousands of small pieces of free, shared code. Your computer downloads and runs them automatically. This week, someone booby-trapped one of those pieces.

Ask

Ask about this presentation

Answers are generated from this presentation.

Chapters

  1. 0:00A Self-Spreading Worm Got Into the Code Behind Billions of Installs
  2. 0:12More than 400 packages. Over 2 billion installs a month.
  3. 0:24One hijacked account poisoned eight packages at once.
  4. 0:38One hidden line, then it hunts for your keys.
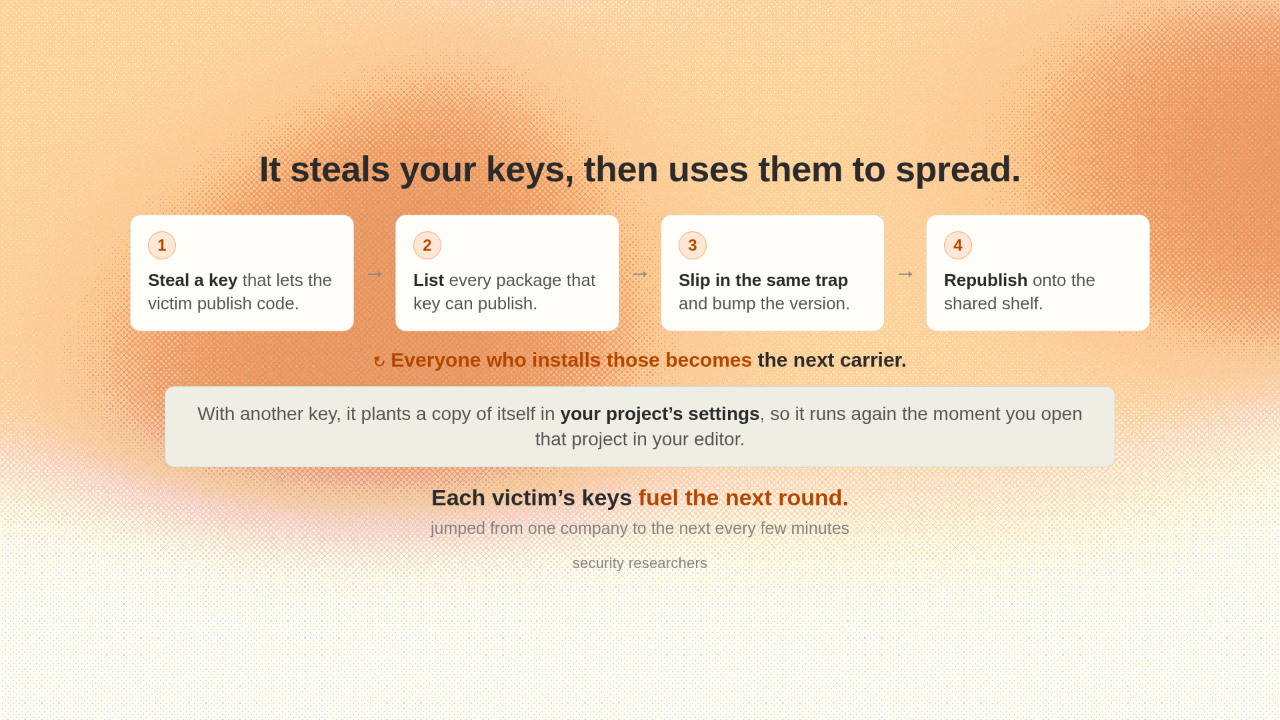
  5. 0:57It steals your keys, then uses them to spread.
  6. 1:25It signs its own loot: “Here We Go Again.”
  7. 1:34One hijacked account. A worm that spreads on your own keys.
Show transcript

A Self-Spreading Worm Got Into the Code Behind Billions of Installs

One hijacked account booby-trapped the everyday code millions of apps are built from.
supply-chain attack security researchers

Almost every app is built from thousands of small pieces of free, shared code. Your computer downloads and runs them automatically. This week, someone booby-trapped one of those pieces.

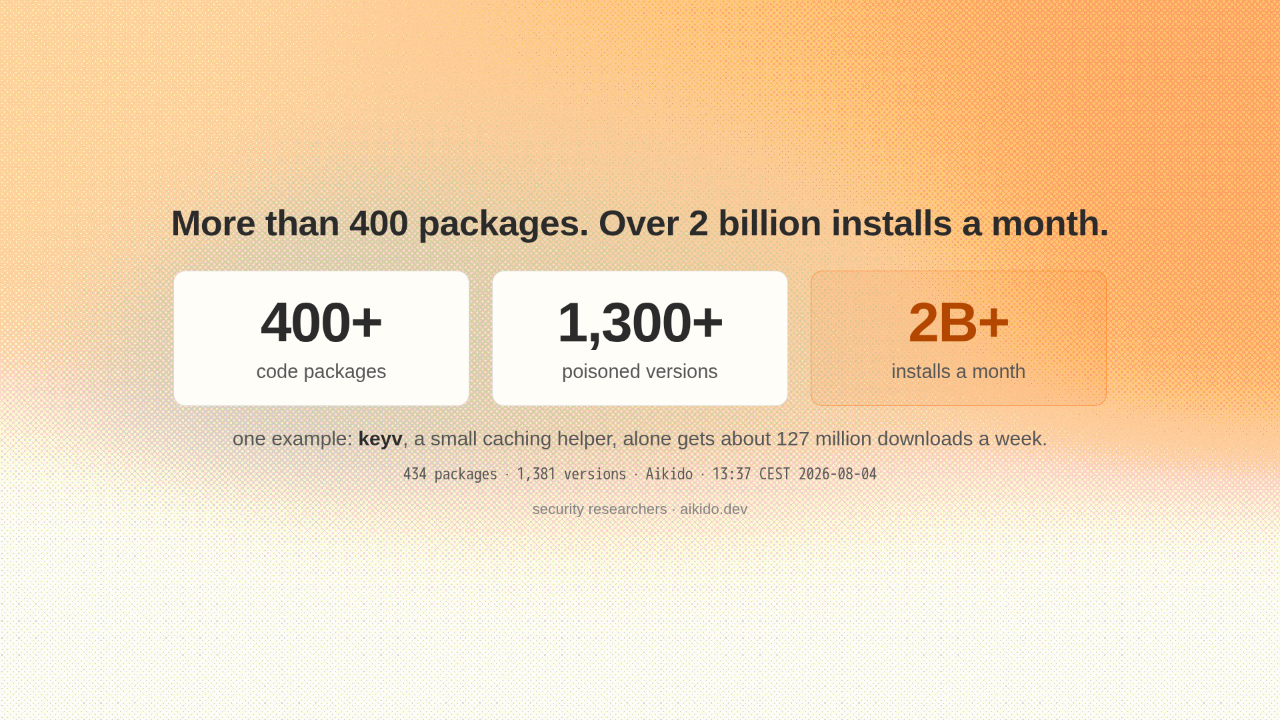
More than 400 packages. Over 2 billion installs a month.

400+
code packages
1,300+
poisoned versions
2B+
installs a month
one example: keyv, a small caching helper, alone gets about 127 million downloads a week.
434 packages · 1,381 versions · Aikido · 13:37 CEST 2026-08-04
security researchers · aikido.dev

The trap is a worm: code that copies itself from victim to victim on its own. Within hours, it reached more than four hundred code packages, installed over two billion times a month.

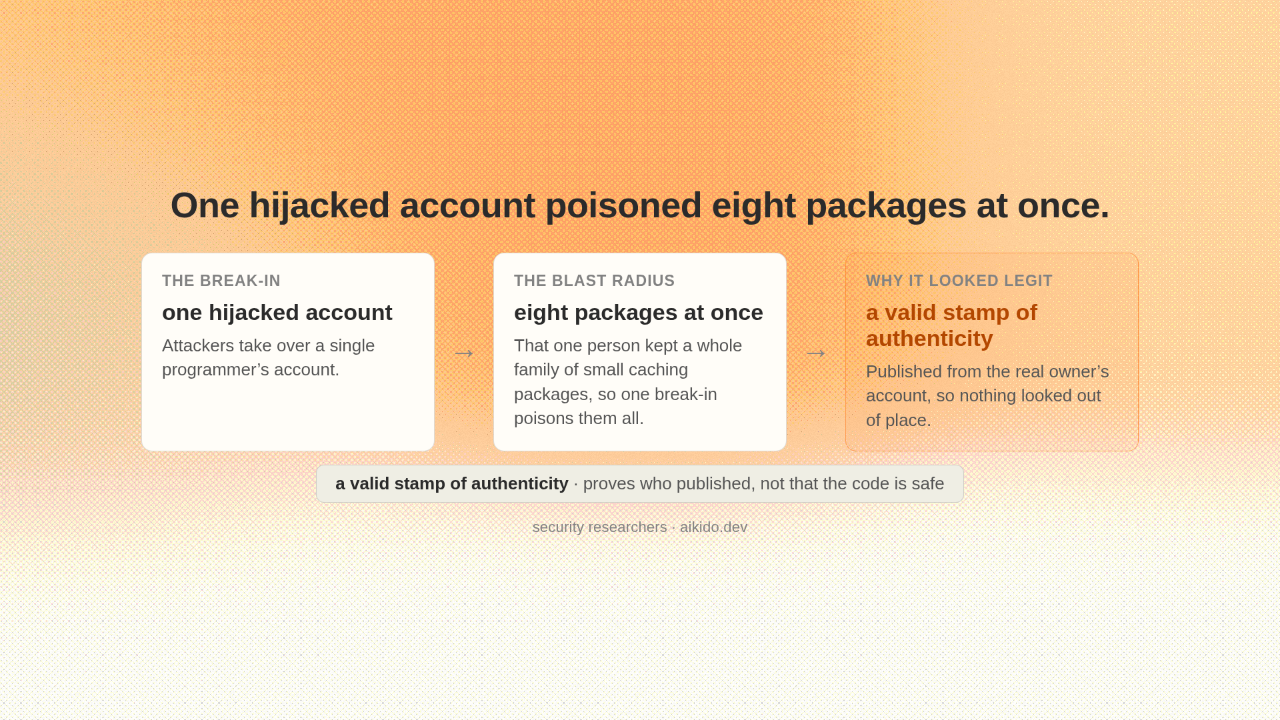
One hijacked account poisoned eight packages at once.

the break-in
one hijacked account
Attackers take over a single programmer’s account.
→
the blast radius
eight packages at once
That one person kept a whole family of small caching packages, so one break-in poisons them all.
→
why it looked legit
a valid stamp of authenticity
Published from the real owner’s account, so nothing looked out of place.
a valid stamp of authenticity · proves who published, not that the code is safe
security researchers · aikido.dev

The attackers took over one programmer’s account. That person maintained a family of small packages, so one break-in poisoned eight at once. Because the poisoned versions came from the real owner’s account, they looked completely legitimate.

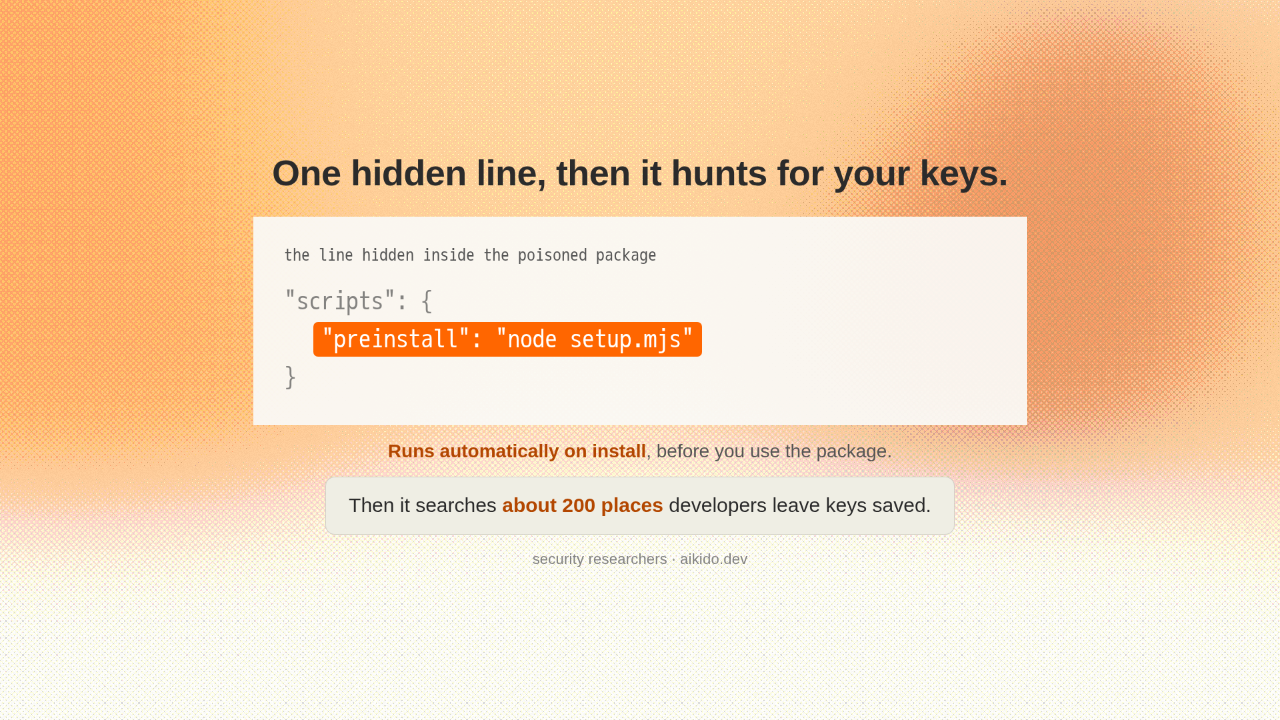
One hidden line, then it hunts for your keys.

the line hidden inside the poisoned package
"scripts": {
"preinstall": "node setup.mjs"
}
Runs automatically on install, before you use the package.
Then it searches about 200 places developers leave keys saved.
security researchers · aikido.dev

Each poisoned package hides one extra line. It tells your computer to run the package’s own code automatically, the moment you download it, before you use anything. That code searches two hundred places developers hide their keys. Those keys unlock a company’s cloud, its payments, its chat. The code steals them.

It steals your keys, then uses them to spread.

1
Steal a key that lets the victim publish code.
→
2
List every package that key can publish.
→
3
Slip in the same trap and bump the version.
→
4
Republish onto the shared shelf.
↻ Everyone who installs those becomes the next carrier.
With another key, it plants a copy of itself in your project’s settings, so it runs again the moment you open that project in your editor.
Each victim’s keys fuel the next round.
jumped from one company to the next every few minutes
security researchers

Among the keys the worm steals are the ones that let the victim publish code. It uses those to poison more packages: it lists every package that key can publish, slips in the same trap, bumps the version, and republishes. Everyone who installs those becomes the next carrier. With another key, the worm plants a copy of itself in your project’s settings, so it runs again the moment you open that project in your editor. Each victim’s keys fuel the next round.

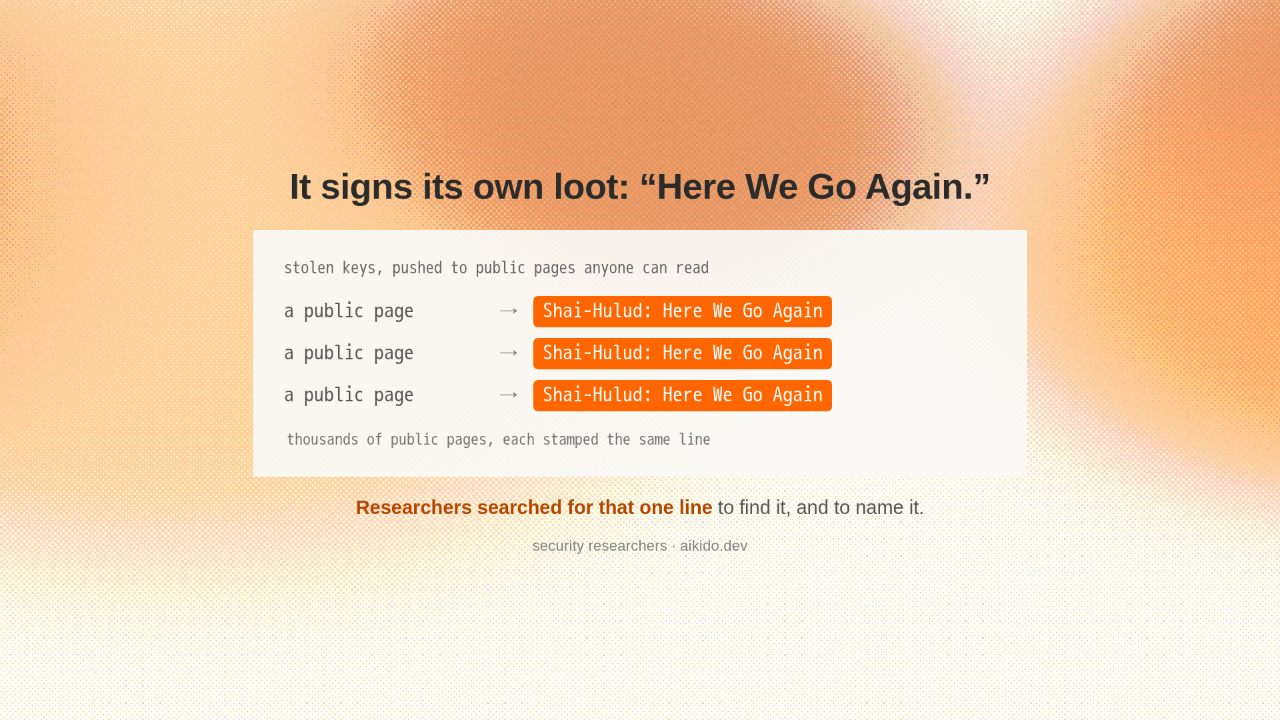
It signs its own loot: “Here We Go Again.”

stolen keys, pushed to public pages anyone can read
a public page → Shai-Hulud: Here We Go Again
thousands of public pages, each stamped the same line
Researchers searched for that one line to find it, and to name it.
security researchers · aikido.dev

The worm posts the stolen keys to public pages anyone can read, each stamped “Shai-Hulud: Here We Go Again.” That tag is how it was found, and named.

One hijacked account. A worm that spreads on your own keys.

security researchers · aikido.dev

So the everyday act of adding a piece of code became a machine that steals your keys and spreads itself. The cleanup is still under way.