Gemini CLI v0.58.0

v0.58.0
A tighter macOS sandbox, ignore rules that follow symlinks, and a cancel that leaves the conversation clean.

Gemini CLI v0.58.0 shipped on the first of September. The biggest change closes a hole in the macOS sandbox that let a sandboxed process reach Docker.
01: The macOS sandbox
Start with the sandbox on macOS.
The container sockets are denied
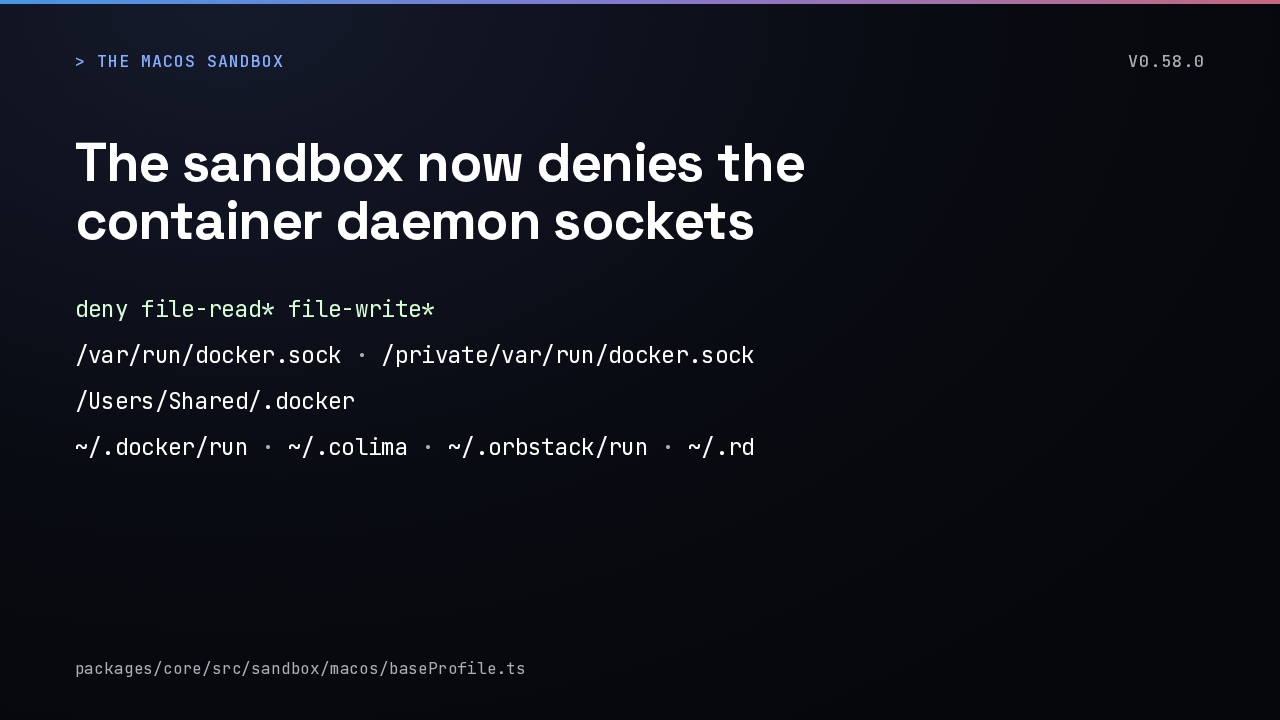
The sandbox now denies the container daemon sockets
A process inside the Seatbelt sandbox could reach the Docker daemon socket, start a privileged container, and mount your whole filesystem through VirtioFS, right around the sandbox boundary. Reads and writes to those sockets are now denied, and so are the Colima, OrbStack and Rancher Desktop ones.
The container binaries are denied too
Running the container binaries is blocked as well
Blocking the socket leaves the binaries. So the profiles also deny executing docker, podman and the rest from their usual install paths, plus the Mach service lookups and the shared memory the daemons talk over. All six built-in profiles carry the same rules.
02: Ignore rules and symlinks
Which files the agent is allowed to touch.
Ignore rules follow a symlink
An ignore rule now follows a symlink to its target
File discovery now checks whether a path is a symbolic link. Your ignore patterns are matched against the literal path and against the path it resolves to, and either match ignores the file. A dangling link is caught and skipped.
read_file checks both paths
read_file checks the link and the file it points at
The read file tool validates the path you gave it and the path that resolves to, so a link is no longer a side door into an ignored file. Grep, glob and read many files get the same behaviour.
03: Cancelling and retrying
What happens when you press stop.
Cancelling rolls the history back
Cancelling a tool call rolls the history back
Cancelling a tool call used to append a synthetic cancellation turn. Those piled up in your context and generated more requests. The CLI now remembers where the history stood after your prompt and slices back to that point.
Retry nudges keep the prefix cache
Retry nudges moved off the system instruction
When a reply comes back empty, or with thinking and no text, the model gets a nudge to try again. That nudge used to go into the system instruction, which changed the prefix and threw the cache away. It now rides on the last user turn instead.
Legacy sessions nudge on an empty tool response
Legacy sessions recover from an empty tool response
Legacy agent sessions picked up the same recovery. When a turn follows a tool response and comes back without visible text, the session nudges the model rather than ending the turn quietly.
04: Policy and the agent server
Two fixes further down the stack.
The path checker is registered again
Auto-edit gets its allowed-path checker back
The write policy declared its safety checkers nested under each rule, and the loader's schema drops a sub-table it does not recognise. So the allowed path checker was missing for write file and replace in auto-edit mode. Moving the declarations to the top level fixes it.
A stale cancellation stops killing the next prompt
A stale cancellation stops killing your next prompt
On the A2A server, pressing stop recorded a cancellation error on the cached task, and that task stayed in memory. Your very next prompt picked up the same object, hit the old error, and aborted. Accepting a new user message now clears it.