mxcheck 2.0.1 retries DNS lookups that time out and installs as a Go v2 module
3 hours ago
mxcheck checks e-mail servers for DNS and configuration errors. This run looks up the A, PTR and SPF records, and each one is a DNS query. Version 2.0.1 retries those lookups when a query times out. It also fixes the Go module path so Go can install the 2.0 line, and updates dependencies for security fixes.
Ask about this presentation
Chapters
Show transcriptHide transcript
mxcheck checks e-mail servers for DNS and configuration errors. This run looks up the A, PTR and SPF records, and each one is a DNS query. Version 2.0.1 retries those lookups when a query times out. It also fixes the Go module path so Go can install the 2.0 line, and updates dependencies for security fixes.
Slide text

mxcheck 2.0.1 retries DNS lookups that time out
It also installs as a Go module at …/mxcheck/v2, with security-updated dependencies.

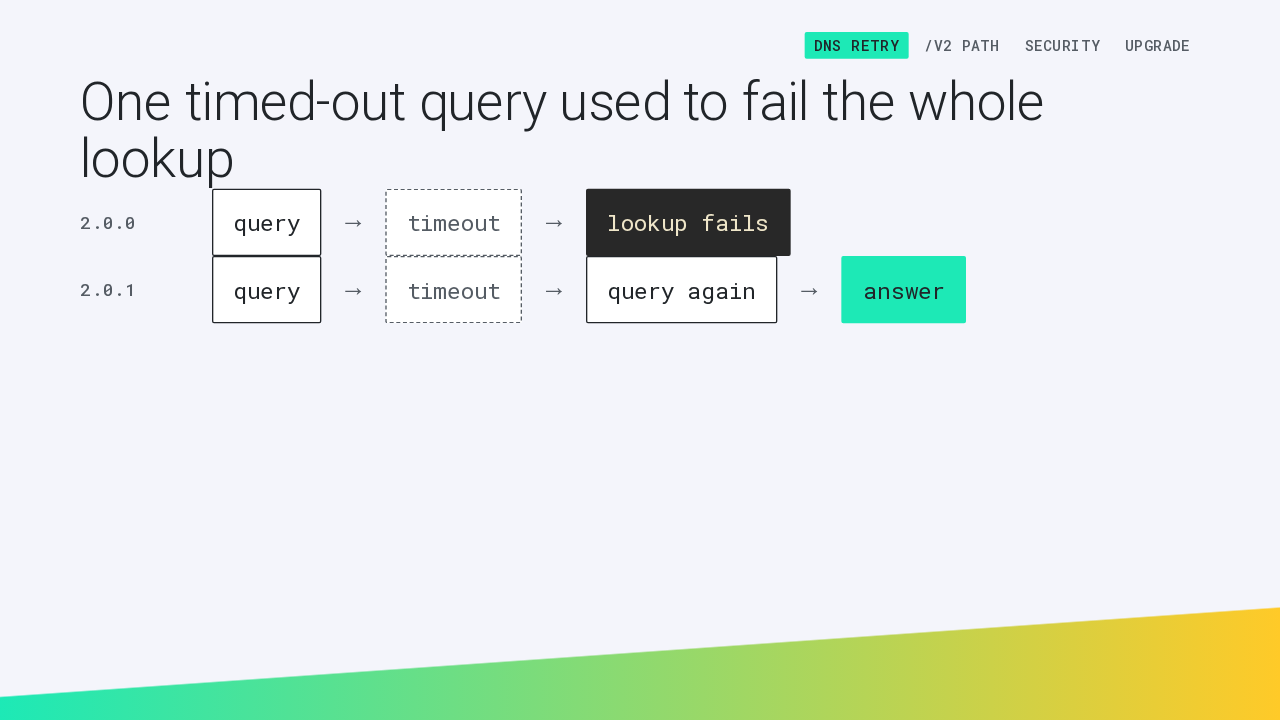
Up to 2.0.0, mxcheck sent each DNS question once. If a single UDP packet got lost, or the upstream resolver was slow, that query timed out and the whole lookup failed, which made lookups flaky. Now a query that times out is sent again, and a later attempt can still get the answer.
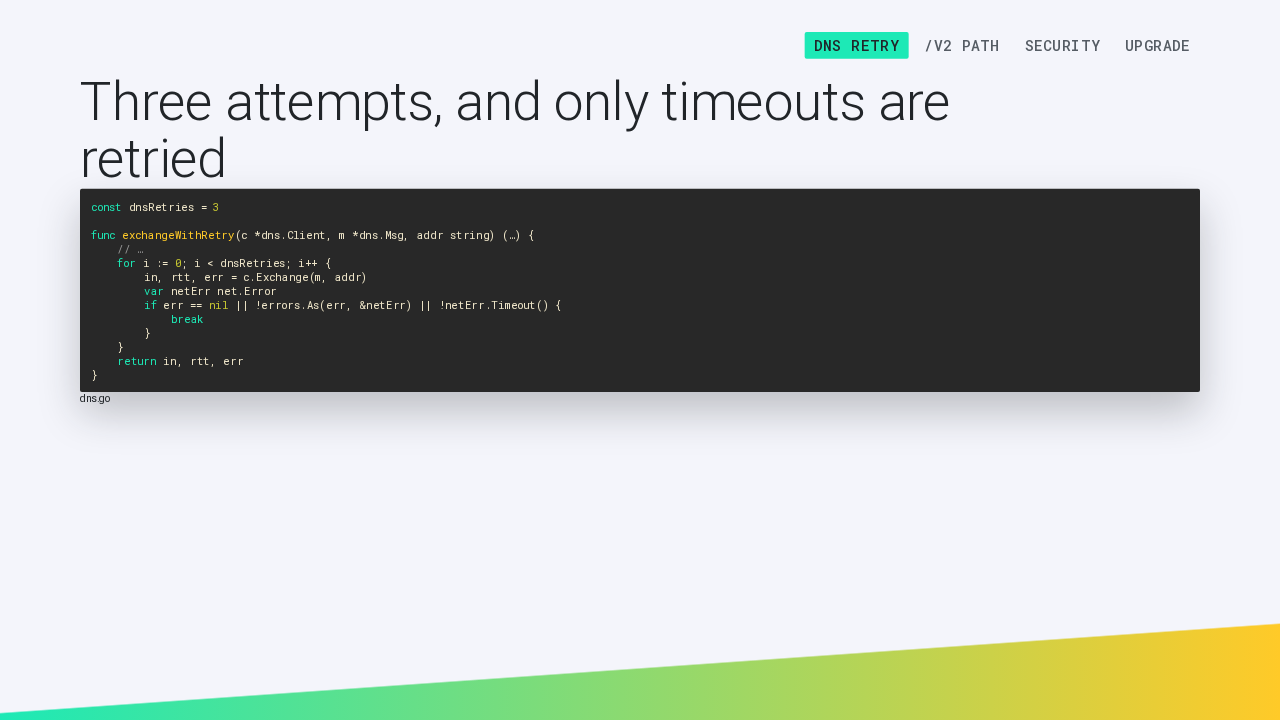
The fix is one new helper in dns.go, called exchangeWithRetry. It allows three attempts in total. Each attempt is the same exchange call mxcheck made before. The loop stops as soon as there is an answer, or as soon as the error is anything other than a timeout. So every other error comes back right away, exactly as it did in 2.0.0.
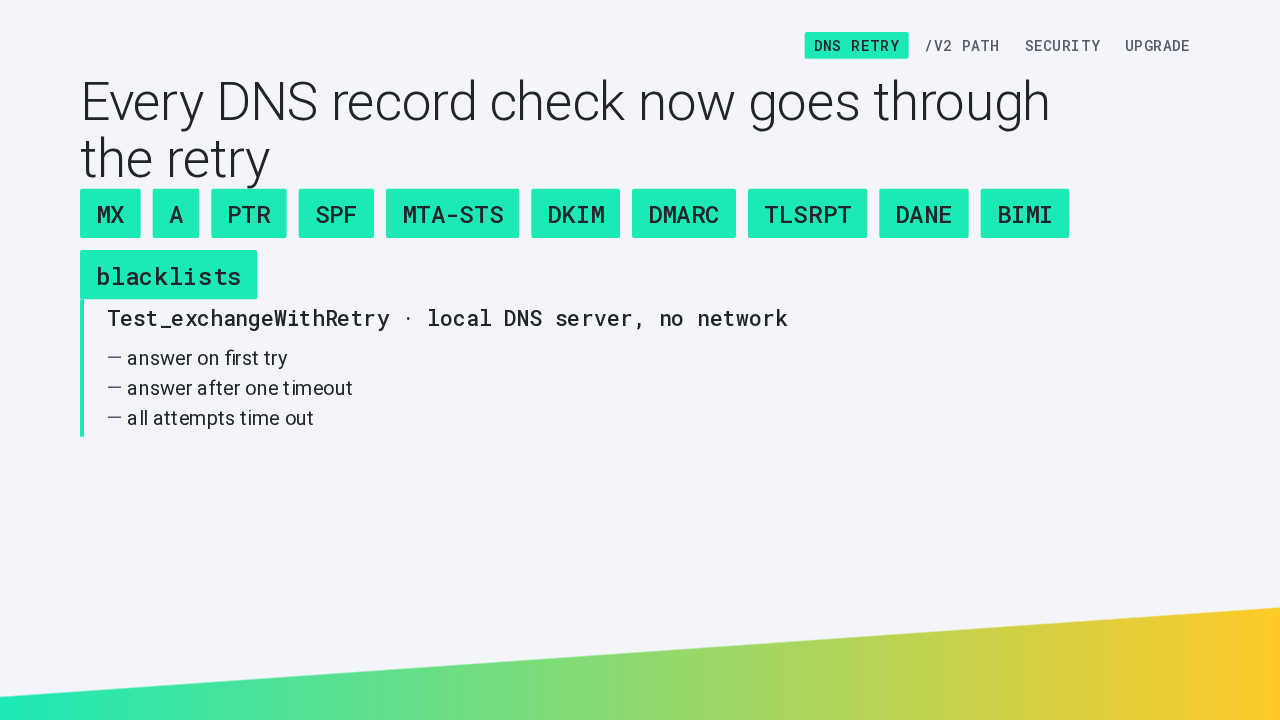
The helper replaces the direct exchange call in every record lookup in dns.go, from MX and SPF to DKIM, DMARC, DANE and BIMI, plus the blacklist check. A new test runs a local DNS server that drops queries on purpose. It checks an answer on the first try, an answer after one timeout, and every attempt timing out, with no network needed.
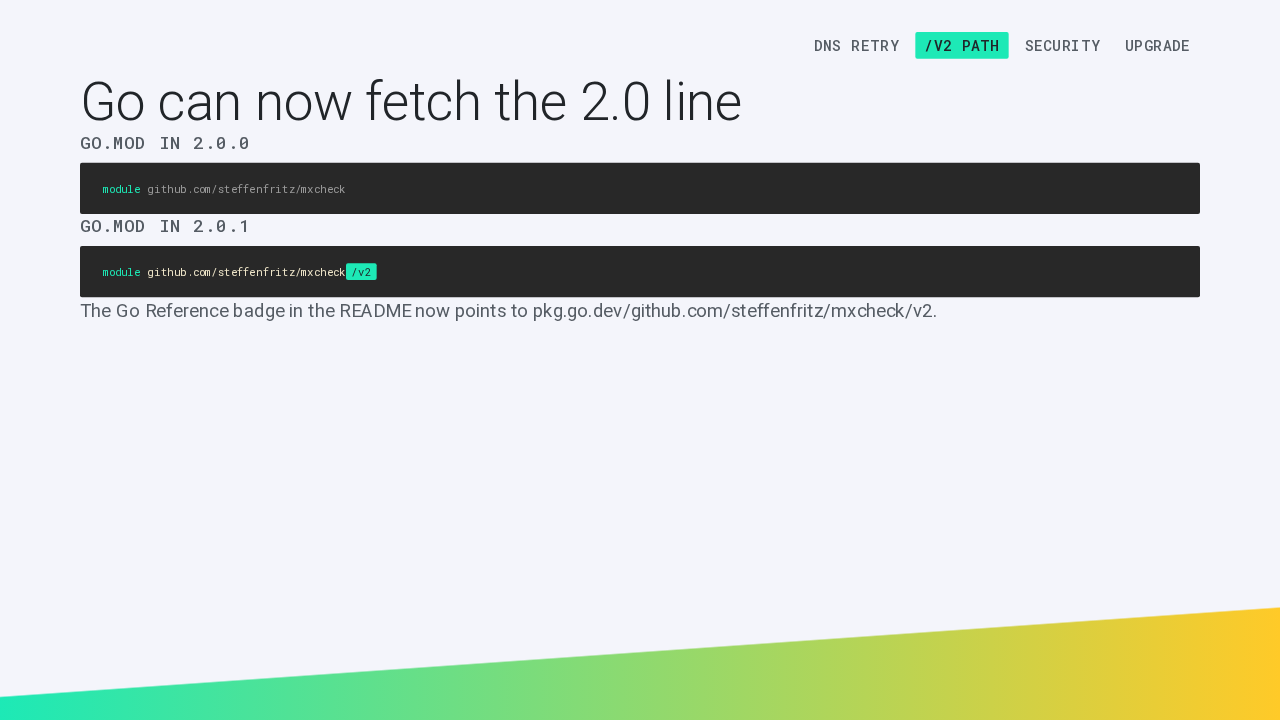
Go expects a module at version 2 or higher to end its path in slash v2. The 2.0.0 release kept the old path, so Go's module tooling couldn't fetch it, and the package page on pkg.go.dev still listed 1.8.0. Version 2.0.1 declares the module as mxcheck slash v2, and the Go Reference badge in the README now points to that path.
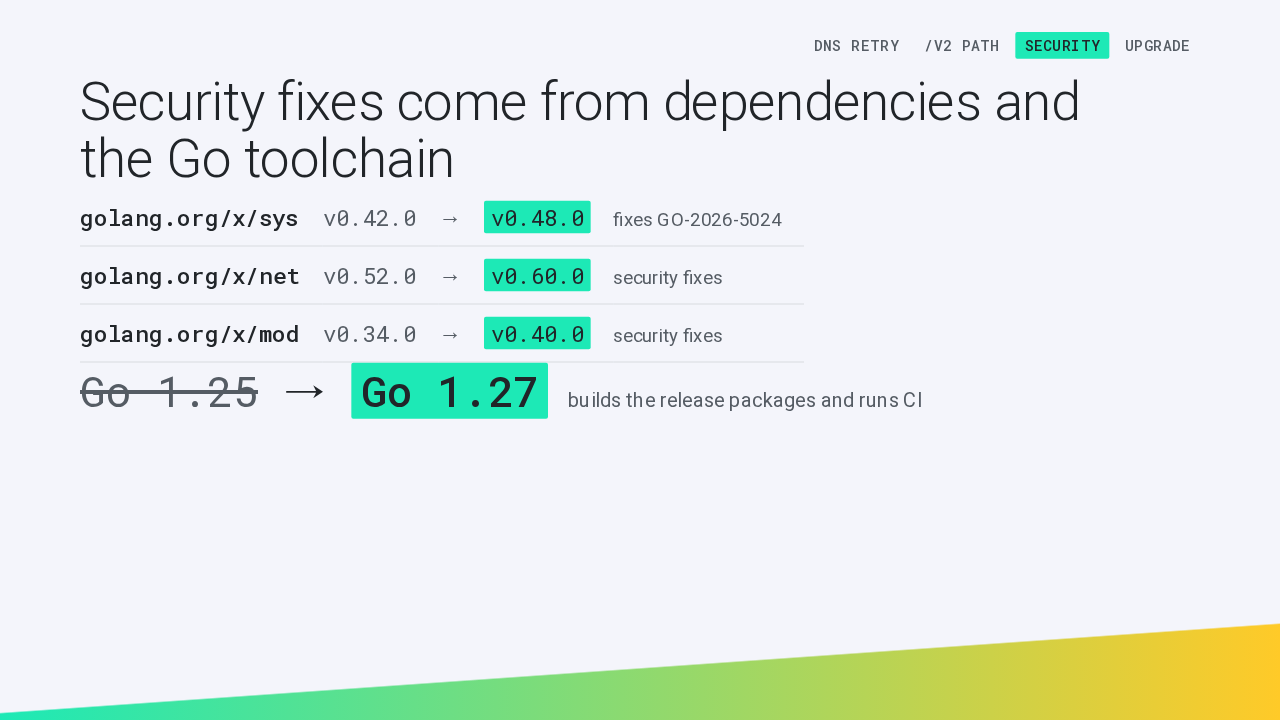
The security work in this release is all in dependencies and the toolchain. The x/sys update fixes a vulnerability listed in Go's vulnerability database, and x/net and x/mod move up for security fixes as well. The release packages are now built with Go 1.27 instead of Go 1.25, which no longer receives security fixes.
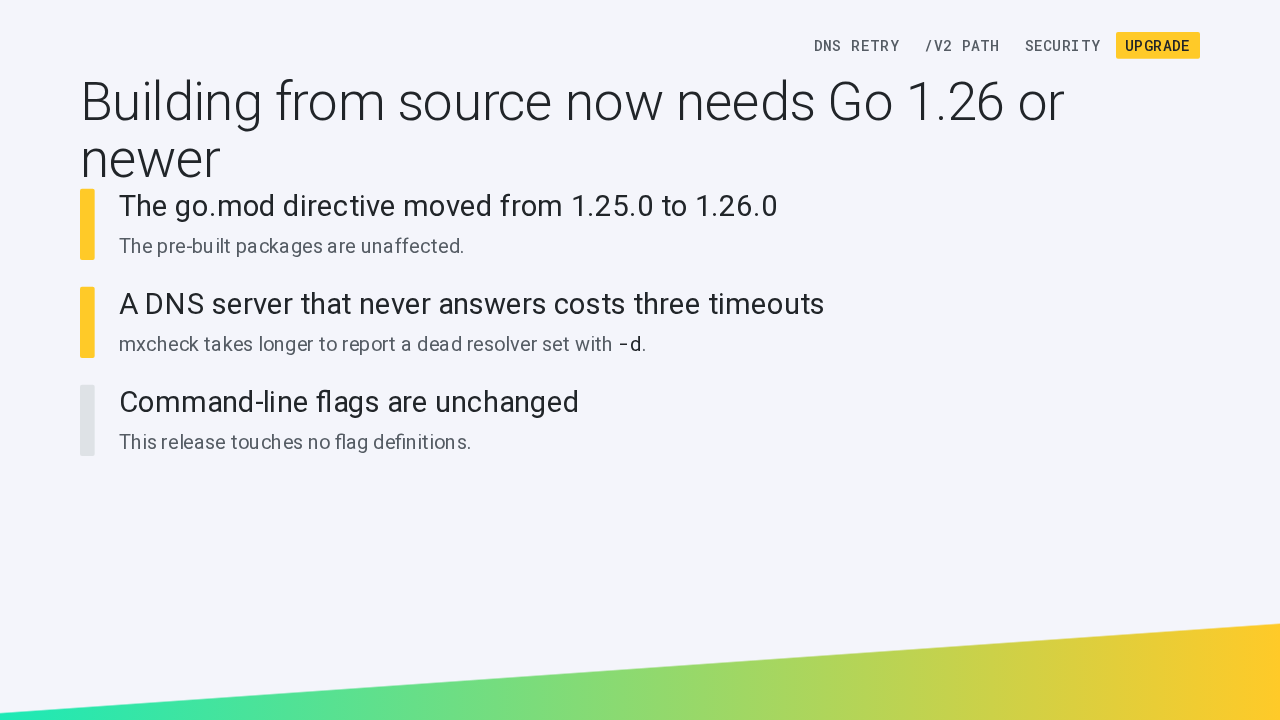
The go directive in go.mod moved from 1.25 to 1.26, so building or installing mxcheck from source now needs Go 1.26 or newer. A DNS server that doesn't answer at all now gets three tries, so mxcheck takes up to three timeouts to give up on it. The command-line flags are the same as in 2.0.0.
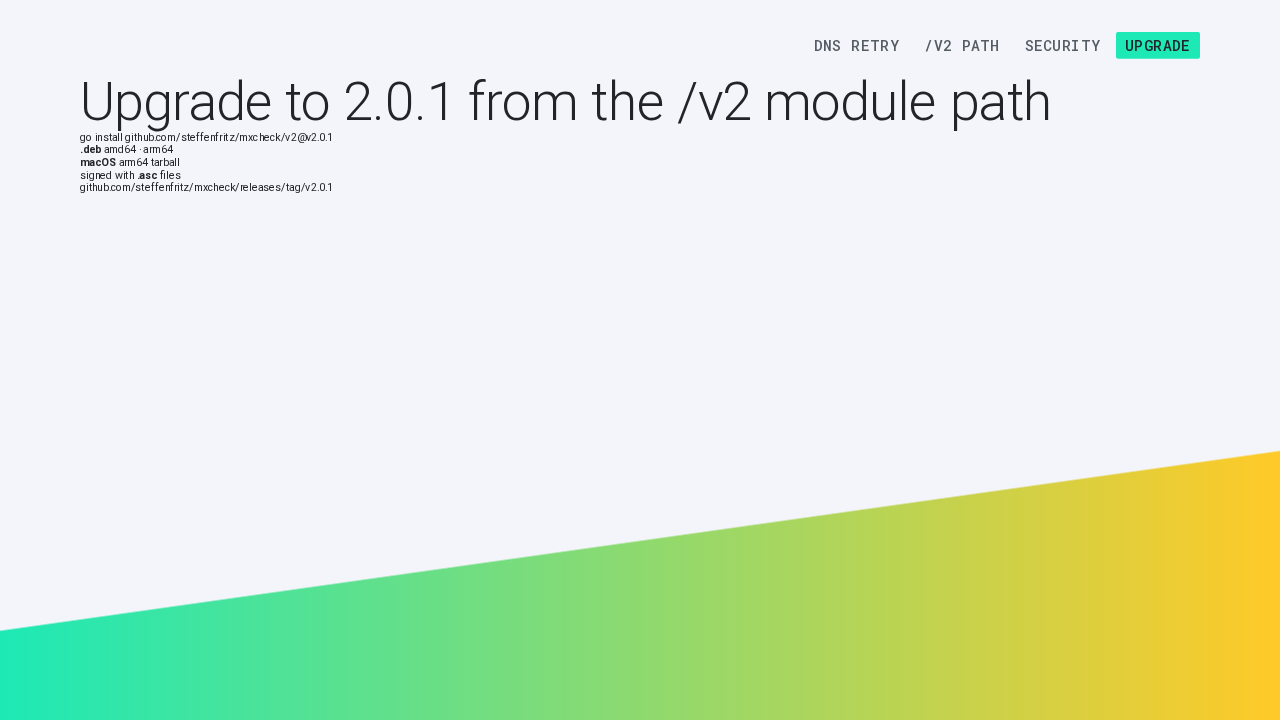
This is a maintenance release, and it adds no new checks. With Go, run go install on the module path that ends in slash v2, at version 2.0.1. The release page also carries Debian packages for amd64 and arm64 and a macOS arm64 tarball, each with a signature file. mxcheck 2.0.1 retries DNS lookups that time out.