skillsaw 0.22.0 lints Goose recipes and keeps CI logs short
2 hours ago
skillsaw lints the files that steer your AI coding agents. Version 0.22.0 starts reading Goose recipes, and a new quiet flag cuts a CI log down to the findings. It also checks Codex and Pi MCP servers, and brings the rule count to 110.
Ask about this presentation
Chapters
Show transcriptHide transcript
skillsaw lints the files that steer your AI coding agents. Version 0.22.0 starts reading Goose recipes, and a new quiet flag cuts a CI log down to the findings. It also checks Codex and Pi MCP servers, and brings the rule count to 110.
Slide text

skillsaw 0.22.0 lints Goose recipes and keeps CI logs short
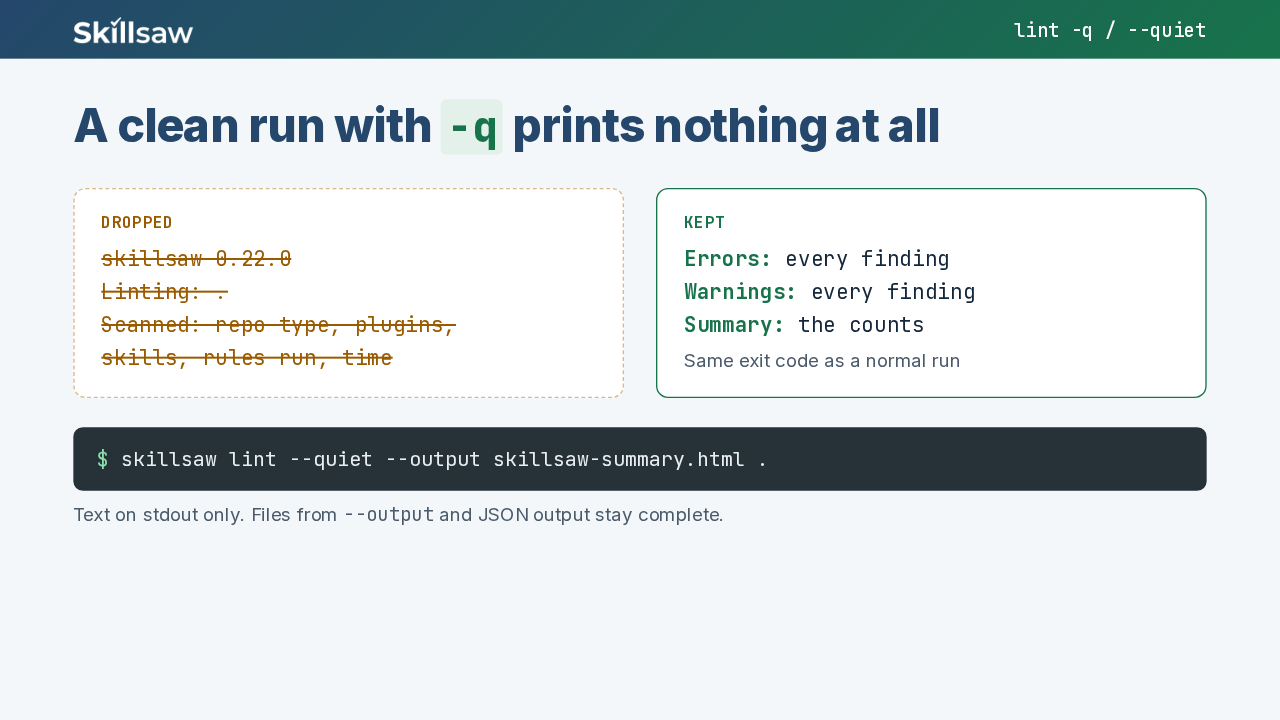
plus Codex and Pi MCP checks · 110 rulesWith -q, a clean run prints nothing. When there are findings, the banner and the scan stats go away, and you keep every finding, the summary and the same exit code. Only the text on screen is trimmed, so a report file from --output is still written in full.
Slide text
 lint -q / --quiet
A clean run with -q prints nothing at all
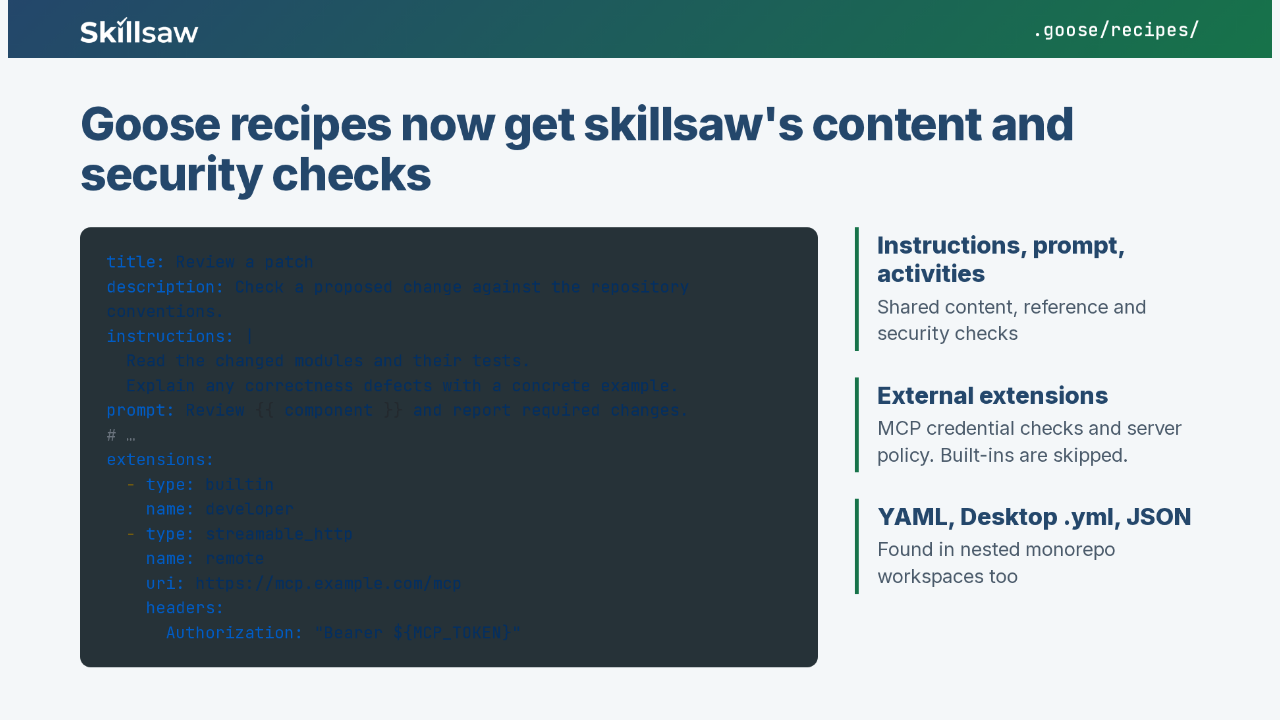
Droppedskillsaw 0.22.0Linting: .Scanned: repo type, plugins,skills, rules run, timeKeptErrors: every findingWarnings: every findingSummary: the countsSame exit code as a normal run$ skillsaw lint --quiet --output skillsaw-summary.html .Text on stdout only. Files from --output and JSON output stay complete.skillsaw now finds Goose recipes in the .goose/recipes folder. Instructions, prompts and activities get the same content and security checks as a skill. External extensions get the MCP credential checks, and built-in ones are skipped. YAML, Desktop and JSON recipes all count, including ones nested in a monorepo.
Slide text
.goose/recipes/
Goose recipes now get skillsaw's content and security checks
title: Review a patch
description: Check a proposed change against the repository conventions.
instructions: |
  Read the changed modules and their tests.
  Explain any correctness defects with a concrete example.
prompt: Review {{ component }} and report required changes.
# …
extensions:
  - type: builtin
    name: developer
  - type: streamable_http
    name: remote
    uri: https://mcp.example.com/mcp
    headers:
      Authorization: "Bearer ${MCP_TOKEN}"
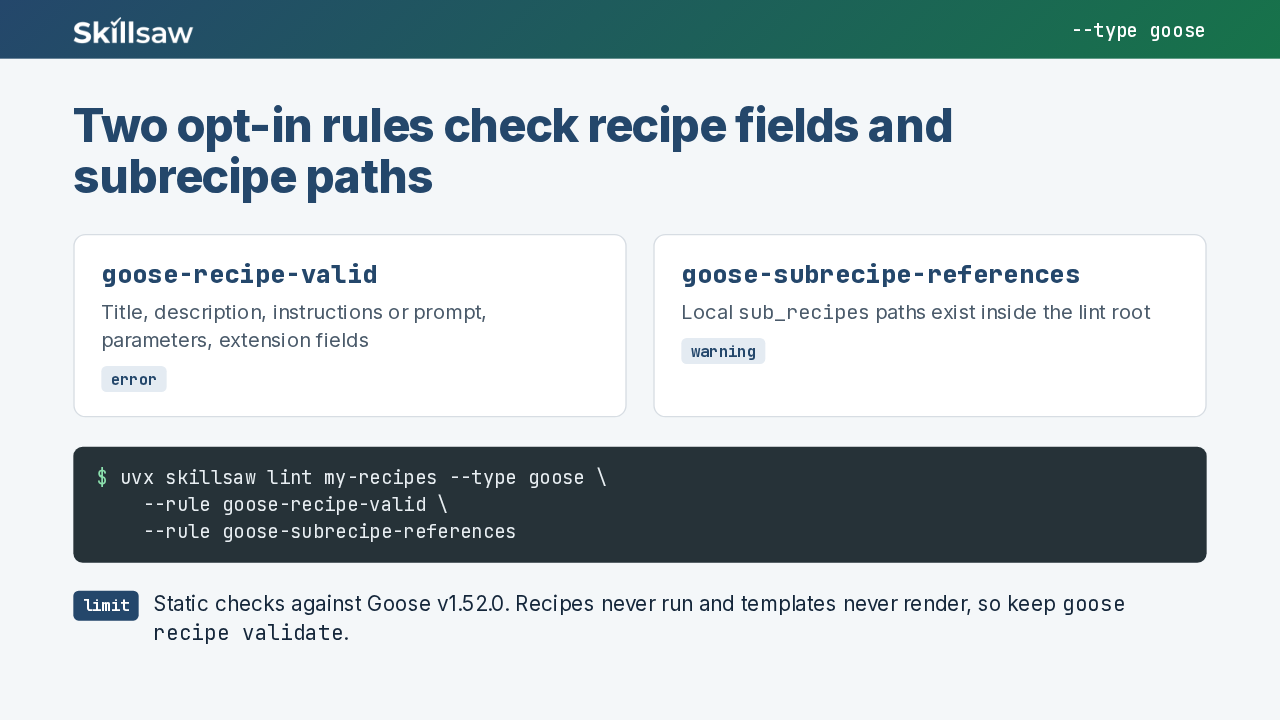
Instructions, prompt, activitiesShared content, reference and security checksExternal extensionsMCP credential checks and server policy. Built-ins are skipped.YAML, Desktop .yml, JSONFound in nested monorepo workspaces tooThe Goose rules themselves are opt-in. One checks a recipe's fields, and the other warns when a local subrecipe path is missing. For a folder of standalone recipes, pass type goose and name both rules. These are static checks against Goose 1.52. skillsaw never runs a recipe or renders a template, so keep running Goose's own validate command.
Slide text
--type goose
Two opt-in rules check recipe fields and subrecipe paths
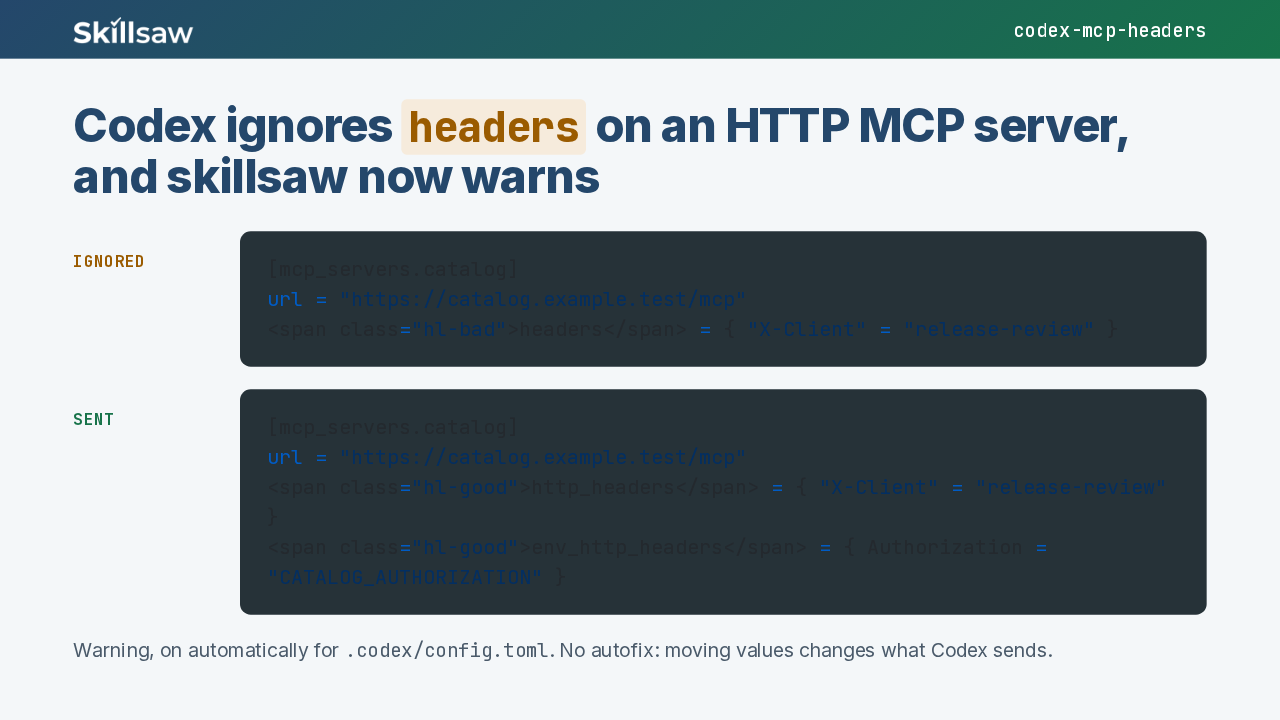
goose-recipe-validTitle, description, instructions or prompt, parameters, extension fieldserrorgoose-subrecipe-referencesLocal sub_recipes paths exist inside the lint rootwarning$ uvx skillsaw lint my-recipes --type goose \ --rule goose-recipe-valid \ --rule goose-subrecipe-referenceslimit Static checks against Goose v1.52.0. Recipes never run and templates never render, so keep goose recipe validate.In a Codex project config, headers on an HTTP MCP server load fine, but Codex ignores them, so requests go out without them. Codex reads http_headers for literal values and env_http_headers for variable names. The new rule warns automatically in Codex projects. It has no autofix, because moving the values changes what Codex sends.
Slide text
codex-mcp-headers
Codex ignores headers on an HTTP MCP server, and skillsaw now warns
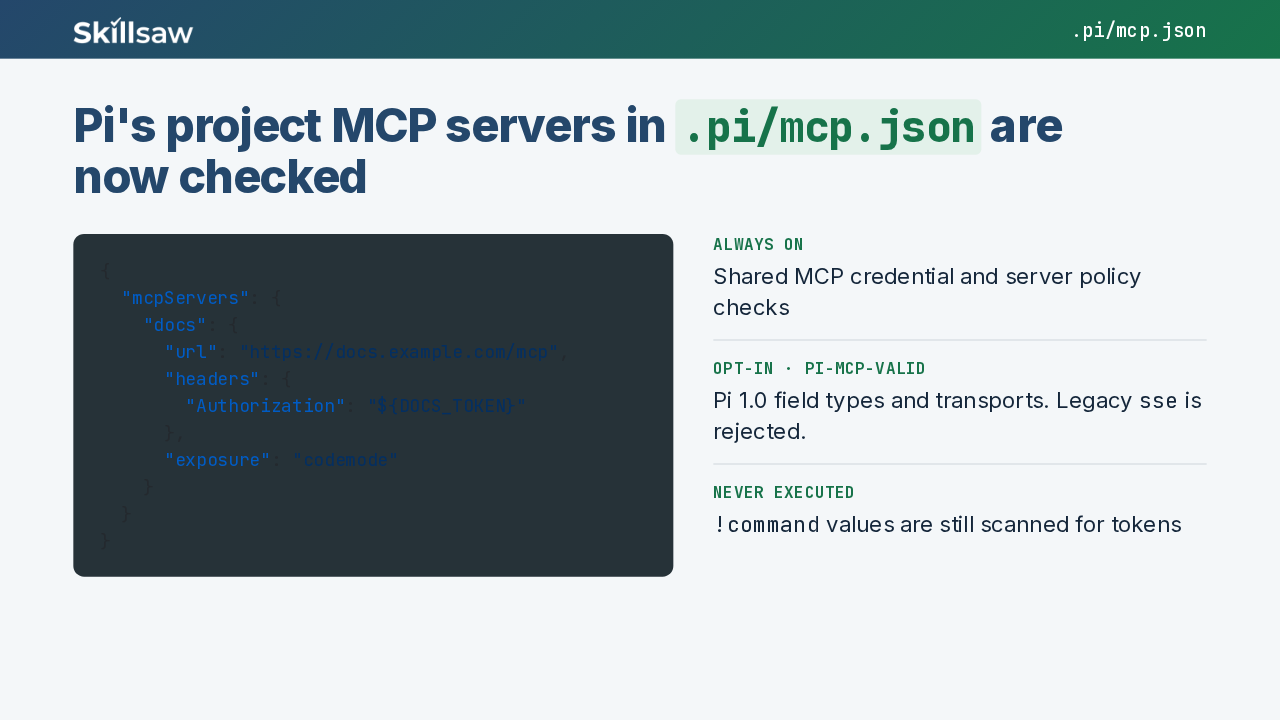
Ignored[mcp_servers.catalog] url = "https://catalog.example.test/mcp" headers = { "X-Client" = "release-review" }Sent[mcp_servers.catalog] url = "https://catalog.example.test/mcp" http_headers = { "X-Client" = "release-review" } env_http_headers = { Authorization = "CATALOG_AUTHORIZATION" }Warning, on automatically for .codex/config.toml. No autofix: moving values changes what Codex sends.Pi added project MCP servers in a file of its own, and skillsaw now finds it. The shared credential and policy checks run on it automatically. Turn on the Pi MCP rule for the field types and transports of Pi 1.0. It rejects the legacy SSE transport. Values that Pi resolves through a command are never run, but skillsaw still scans them for embedded tokens.
Slide text
.pi/mcp.json
Pi's project MCP servers in .pi/mcp.json are now checked
{
  "mcpServers": {
    "docs": {
      "url": "https://docs.example.com/mcp",
      "headers": {
        "Authorization": "${DOCS_TOKEN}"
      },
      "exposure": "codemode"
    }
  }
}
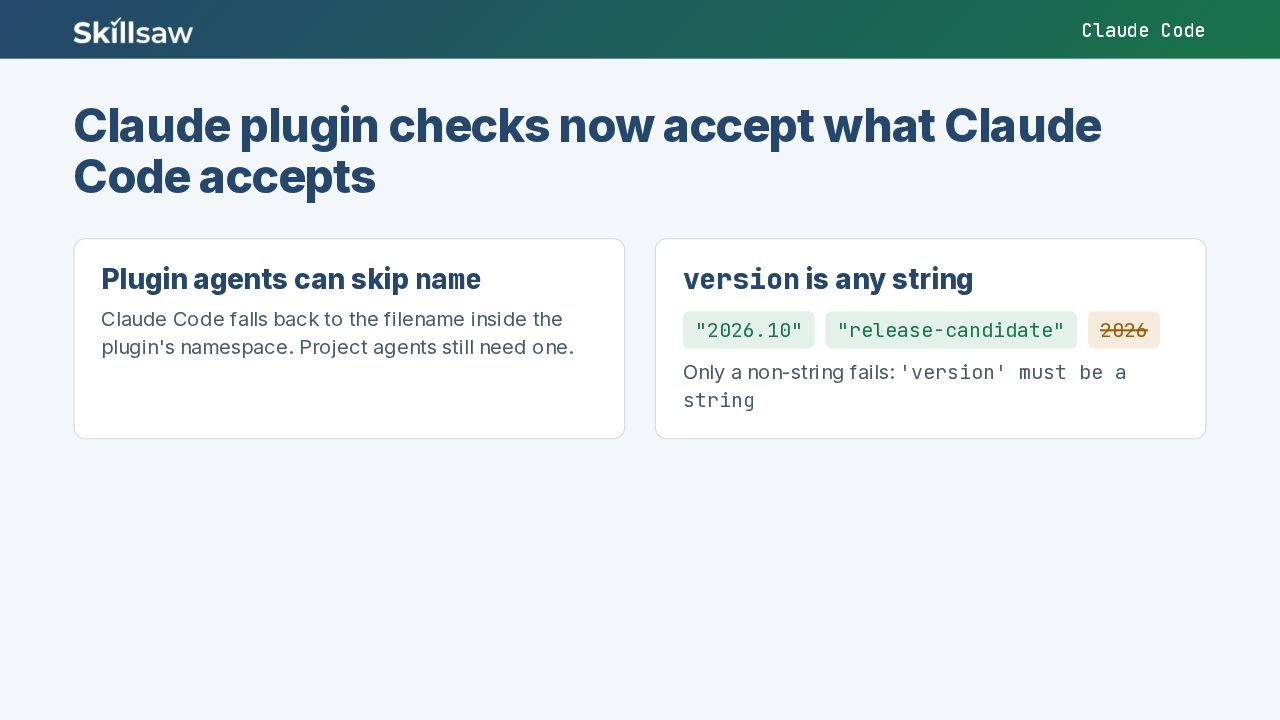
Always onShared MCP credential and server policy checksOpt-in · pi-mcp-validPi 1.0 field types and transports. Legacy sse is rejected.Never executed!command values are still scanned for tokensTwo Claude Code fixes remove false errors. Agents inside a plugin can skip the name field, since Claude Code falls back to the file name. Project agents still need one. And plugin versions no longer have to be semver. Calendar versions and labels pass, and only a version that isn't a string gets flagged.
Slide text
Claude Code
Claude plugin checks now accept what Claude Code accepts
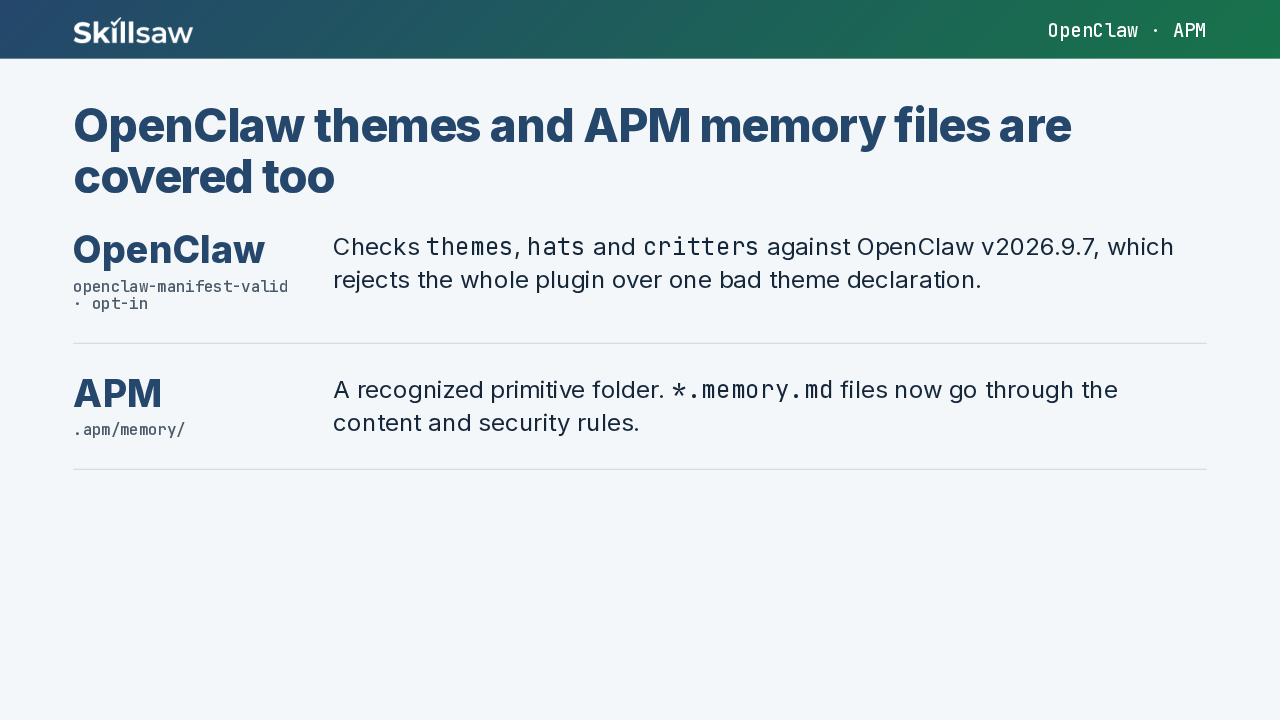
Plugin agents can skip nameClaude Code falls back to the filename inside the plugin's namespace. Project agents still need one.version is any string"2026.10" "release-candidate" 2026Only a non-string fails: 'version' must be a stringFor OpenClaw, the opt-in manifest rule now checks theme and artwork declarations, because one bad theme makes OpenClaw reject the whole plugin. For APM, a memory folder now counts as a package folder, and memory files get the security rules, so an instruction hidden in an HTML comment gets caught.
Slide text
OpenClaw · APM
OpenClaw themes and APM memory files are covered too
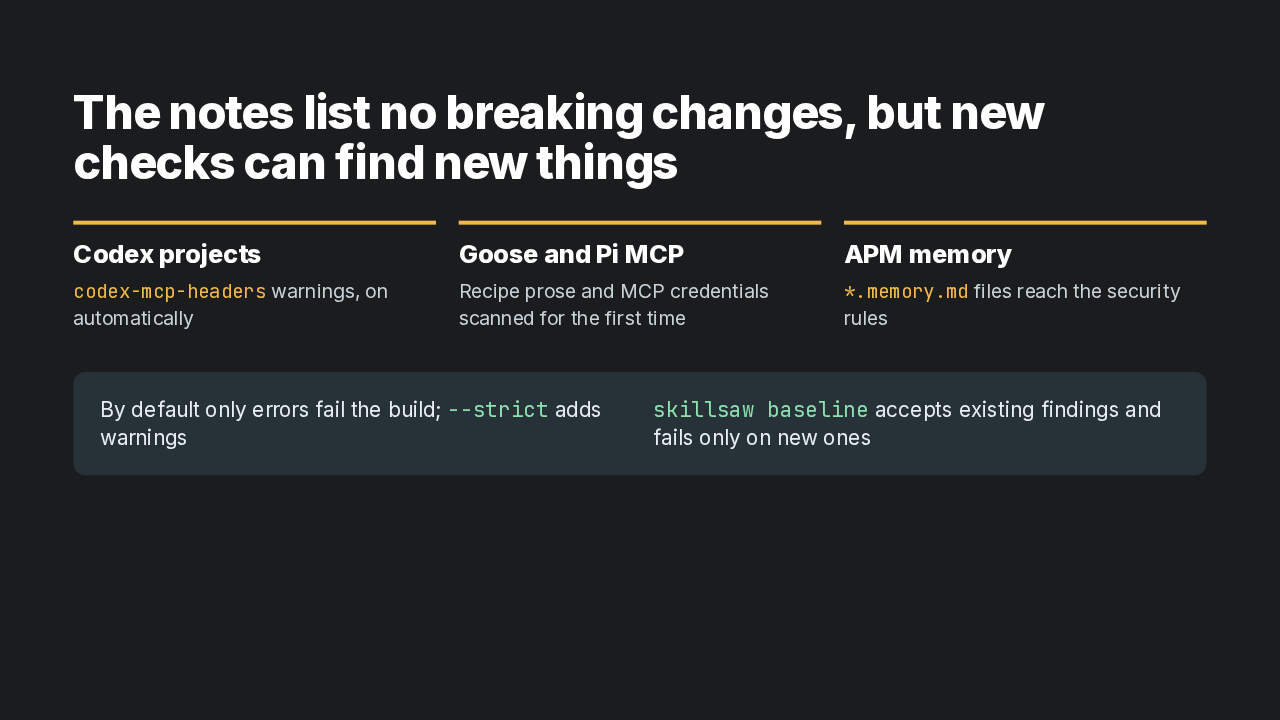
OpenClawopenclaw-manifest-valid · opt-inChecks themes, hats and critters against OpenClaw v2026.9.7, which rejects the whole plugin over one bad theme declaration.APM.apm/memory/A recognized primitive folder. *.memory.md files now go through the content and security rules.The release notes list no breaking changes, but wider coverage can turn up new findings. You may see the Codex headers warning, and first-time checks on Goose recipes, Pi MCP files and APM memory files. By default only errors fail the build, and skillsaw baseline accepts the existing findings, so only new ones fail.
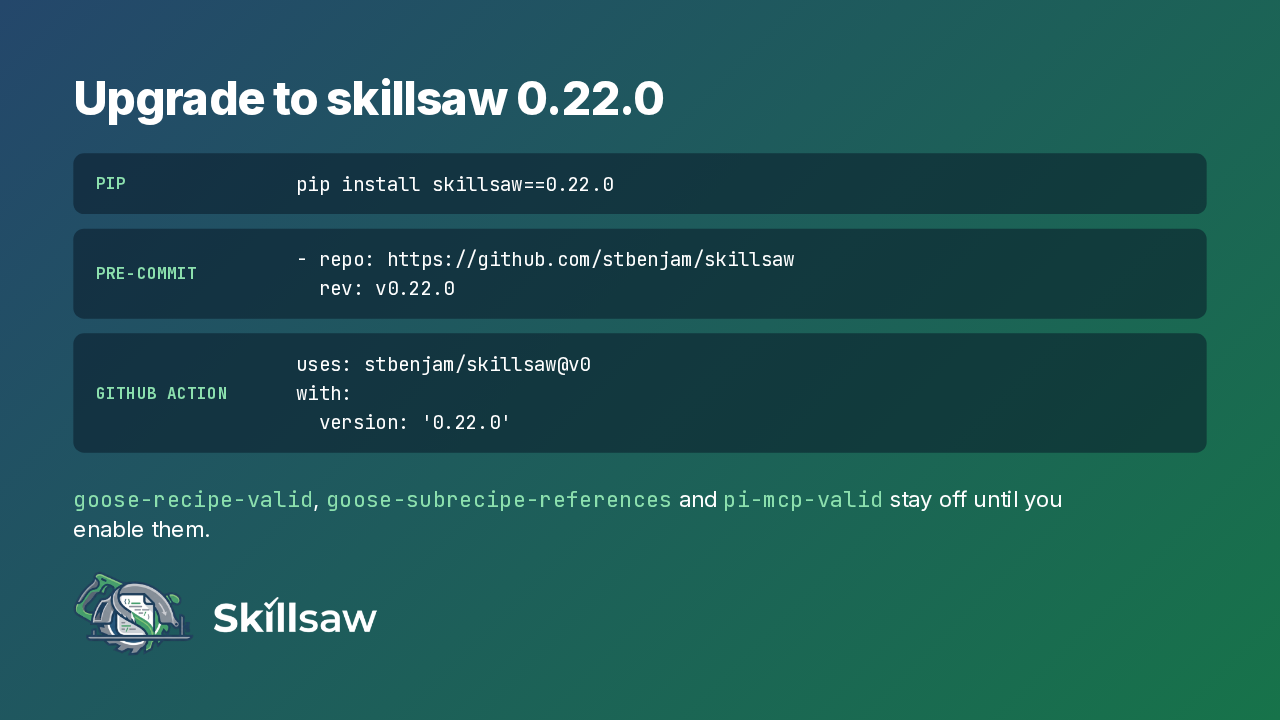
To upgrade, pin 0.22.0 with pip, bump the pre-commit rev, or set the version in the GitHub Action. The Goose and Pi MCP rules stay off until you enable them. Then skillsaw 0.22.0 lints your Goose recipes, and with -q, your CI log stays short.
Slide text
Upgrade to skillsaw 0.22.0
pippip install skillsaw==0.22.0
pre-commit- repo: https://github.com/stbenjam/skillsaw rev: v0.22.0
GitHub Actionuses: stbenjam/skillsaw@v0 with: version: '0.22.0'
goose-recipe-valid,goose-subrecipe-referencesandpi-mcp-validstay off until you enable them.