2026.10.6 needs a patched Node
 OpenClaw
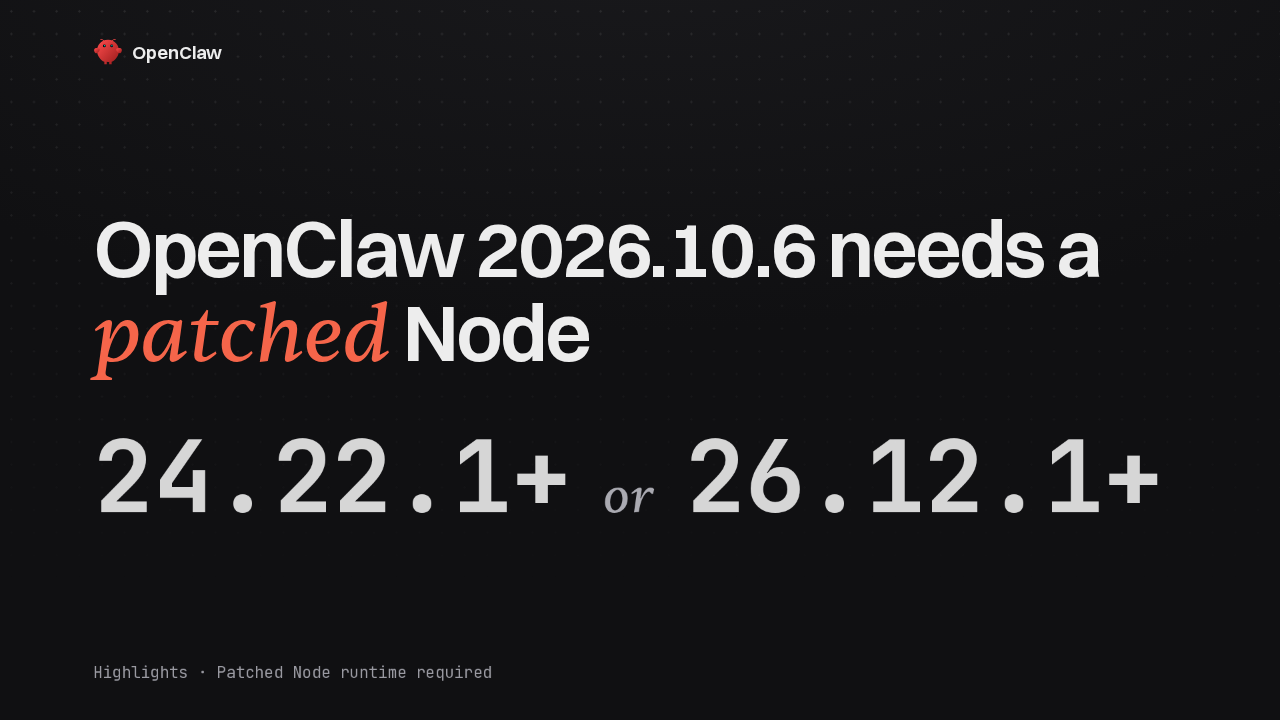
 2026.10.6 needs a patched Node
OpenClaw 2026.10.6 is a patch release of reliability fixes, and it raises the Node floor. You now need Node 24.22.1 or later on the 24 line, or 26.12.1 or later on the 26 line. Everything else in this release fixes something that used to go wrong.
Older Node trusts compromised certificates
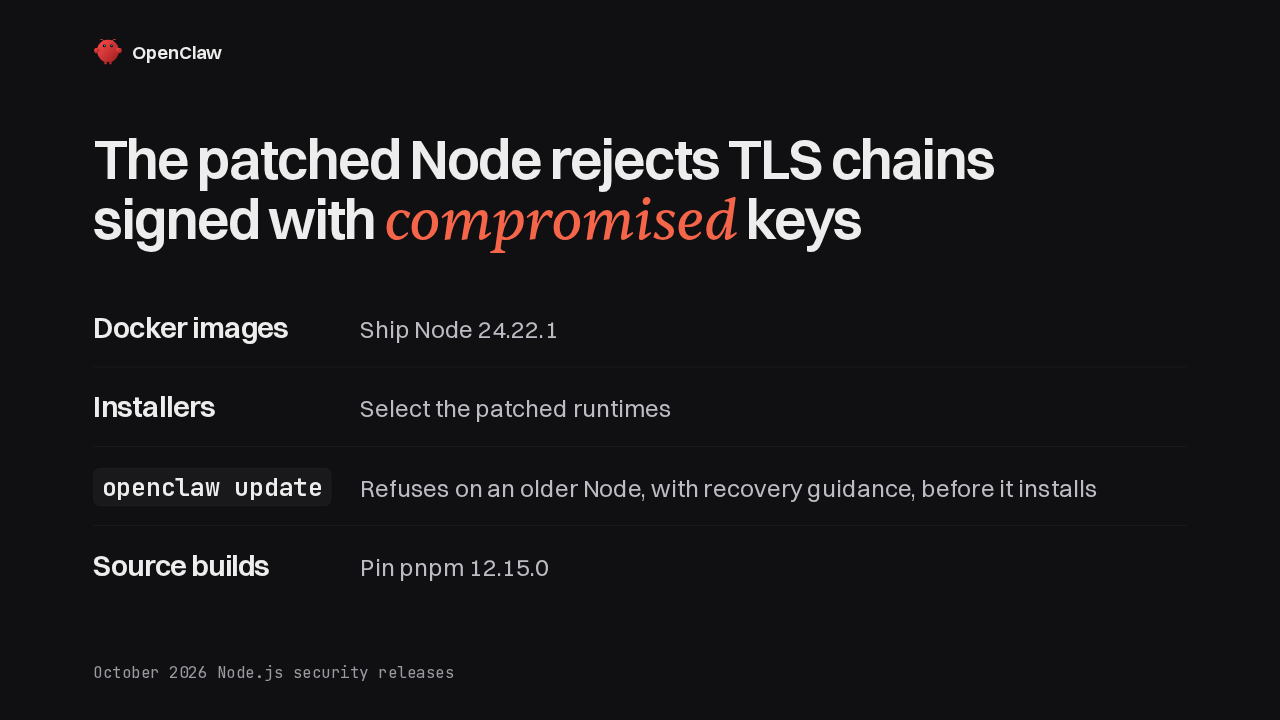
OpenClawThe patched Node rejects TLS chains signed with compromised keys
The October Node.js security releases addressed compromised certificate keys, and only the patched versions reject TLS chains signed with them. Most of the move is handled for you. Docker images ship Node 24.22.1 and the installers pick the patched runtimes. On an older Node, openclaw update refuses before it installs, so your running install keeps working.
Updates refuse an unsafe swap
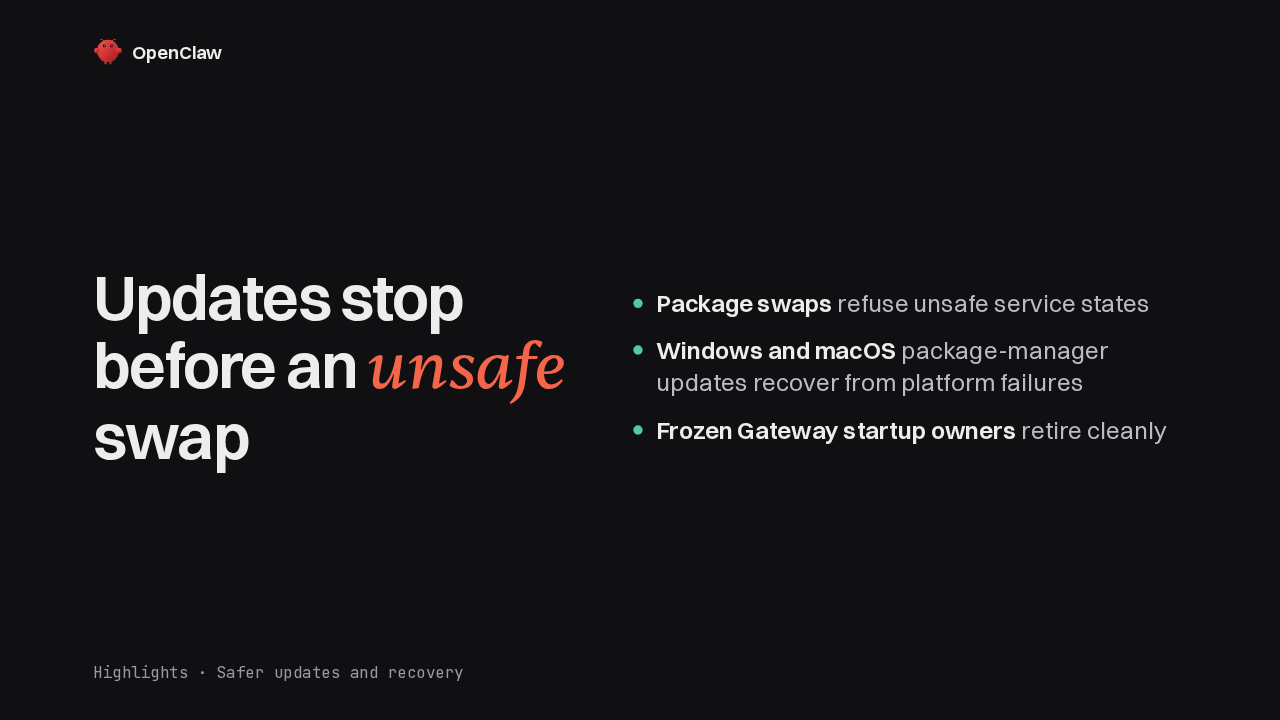
OpenClawUpdates stop before an unsafe swap
- Package swaps refuse unsafe service states
- Windows and macOS package-manager updates recover from platform failures
- Frozen Gateway startup owners retire cleanly
Updates themselves got harder to break. A package swap now refuses when the service is in an unsafe state. Package-manager updates on Windows and macOS recover from the failures specific to each platform. And a Gateway whose startup froze can be retired cleanly.
Doctor keeps your data intact
OpenClawDoctor refuses an import that would lose data
Doctor and the migration paths now stop before they lose data. A malformed or lossy workspace import is refused. Notes with malformed bytes keep them, and a wiki rewrite that isn't safe for non UTF-8 text is rejected. SQLite backups in deeply nested update paths are kept, and a failed restore leaves its staging evidence behind.
Messages arrive once
OpenClawMessages arrive once, across restarts
If OpenClaw talks to you through a chat app, this one is for you. WhatsApp stops sending duplicates after socket failures, and stickers sent from WhatsApp Web download. Telegram albums get through, Slack's relay recovers, and Discord keeps pending replies when a voice call ends. Queued turns and streamed replies also survive a restart, with no duplicates and no false missing-answer notices.
Models and tool calls recover
OpenClawTool calls recover instead of stalling
Models
- GPT-5.6 tool turns no longer fail
- DeepSeek via OpenRouter tool calls recovered
- LM Studio recovers from context overflow
Tools
- Unfinished tools time out visibly
- Very large patch hunks apply without crashing
- Stopped yielded tasks stay stopped
On the model side, GPT-5.6 tool turns stop failing with a reasoning effort error, DeepSeek tool calls routed through OpenRouter are recovered, and LM Studio recovers from context overflow. For tools, an unfinished tool now times out where you can see it, very large patch hunks apply without crashing, and a task you stopped stays stopped.
Windows starts, iOS reconnects
OpenClawWindows starts and iOS reconnects
On Windows, a fresh state store, a Proxy-backed environment or a stored Anthropic credential could stop OpenClaw from starting. Now it starts. And on iOS, Talk and chat recover from first-reply failures and timeouts.
Check your Node version first
OpenClawBring your own Node? Upgrade it first
26.1+
26.12.1+
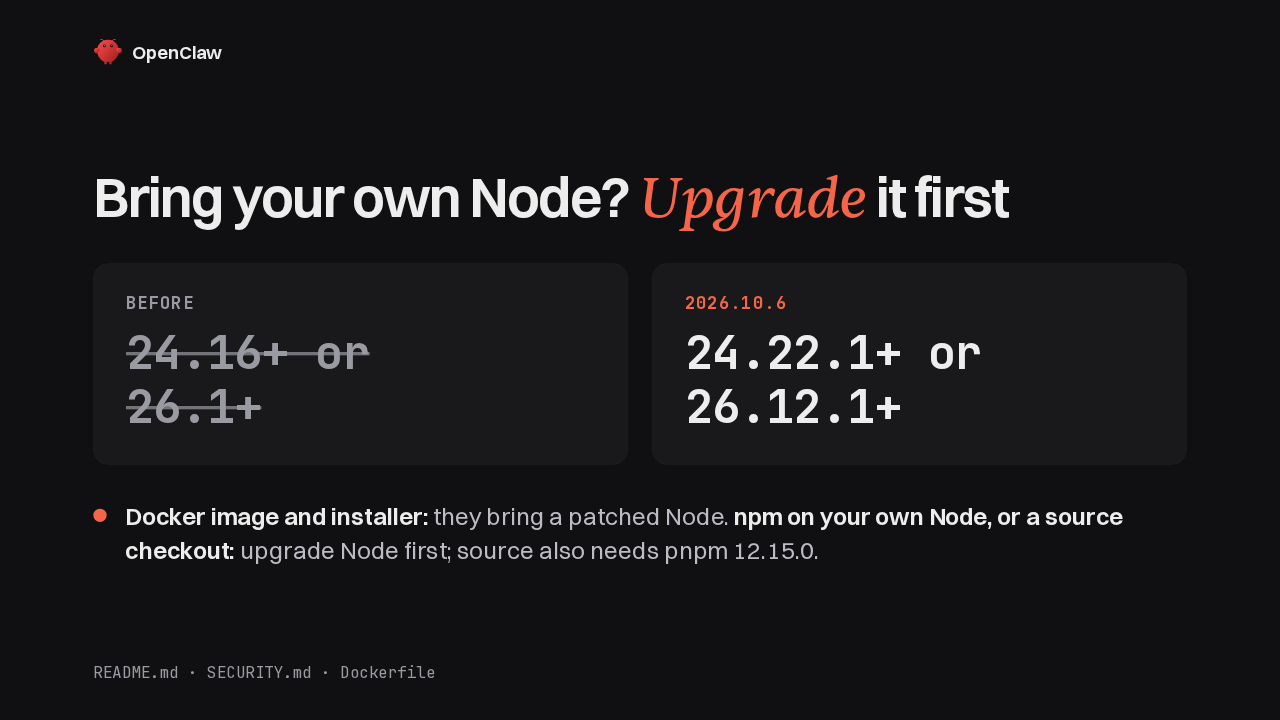
This is the one change you may have to act on. The floor used to be Node 24.16 or 26.1. It is now 24.22.1 or 26.12.1. The new Docker image ships a patched Node, and the installer picks one for you. If you installed with npm on a Node you manage, or build from source, upgrade Node first. Source builds also need pnpm 12.15.0.
How to upgrade
OpenClawCheck Node, then update
# v24.22.1+ or v26.12.1+
$ openclaw update
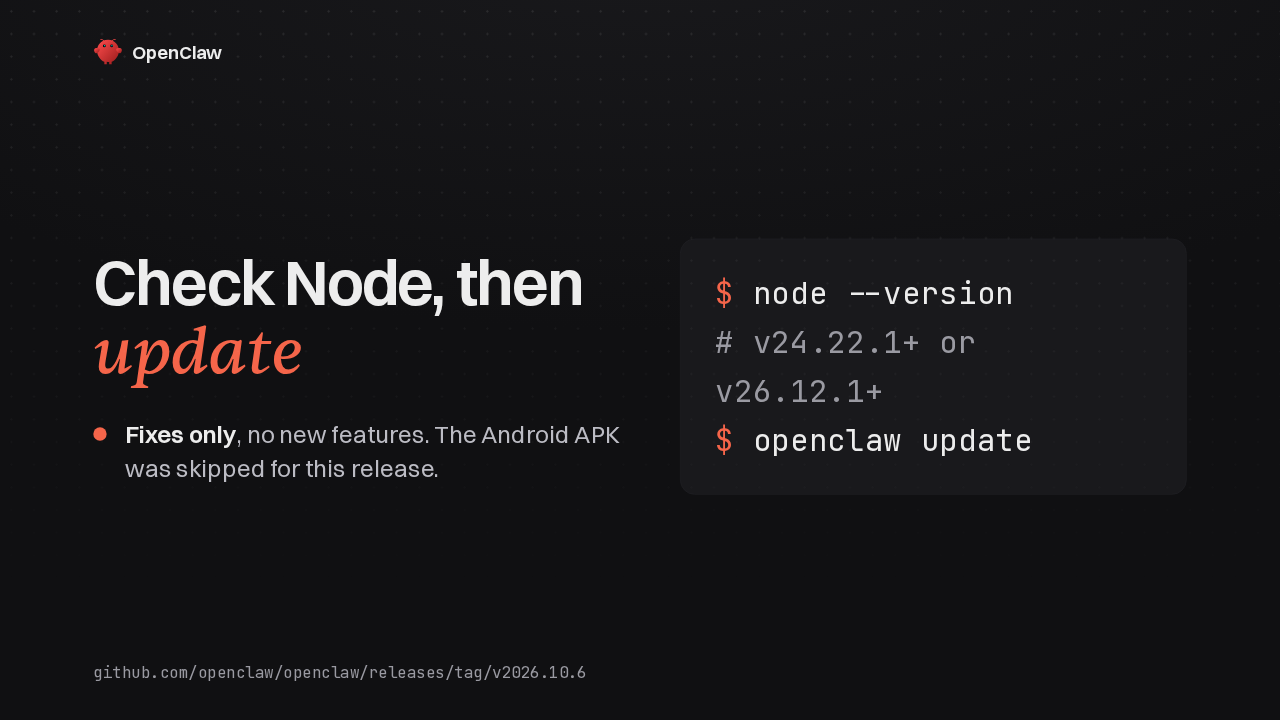
Check your Node version, then run openclaw update. On an older Node the update stops with recovery steps, and your current install keeps running. This release adds no new features, and it ships without a new Android APK. OpenClaw 2026.10.6 needs a patched Node.