Signed scanner images

gstack 1.91.22.0 gives /cso reviewed, signed scanner images
In gstack 1.91.22.0, /cso gets reviewed, signed images to build its security scanners from. Each of the six scanners has one pinned base image, for both Linux platforms.
Signed bases
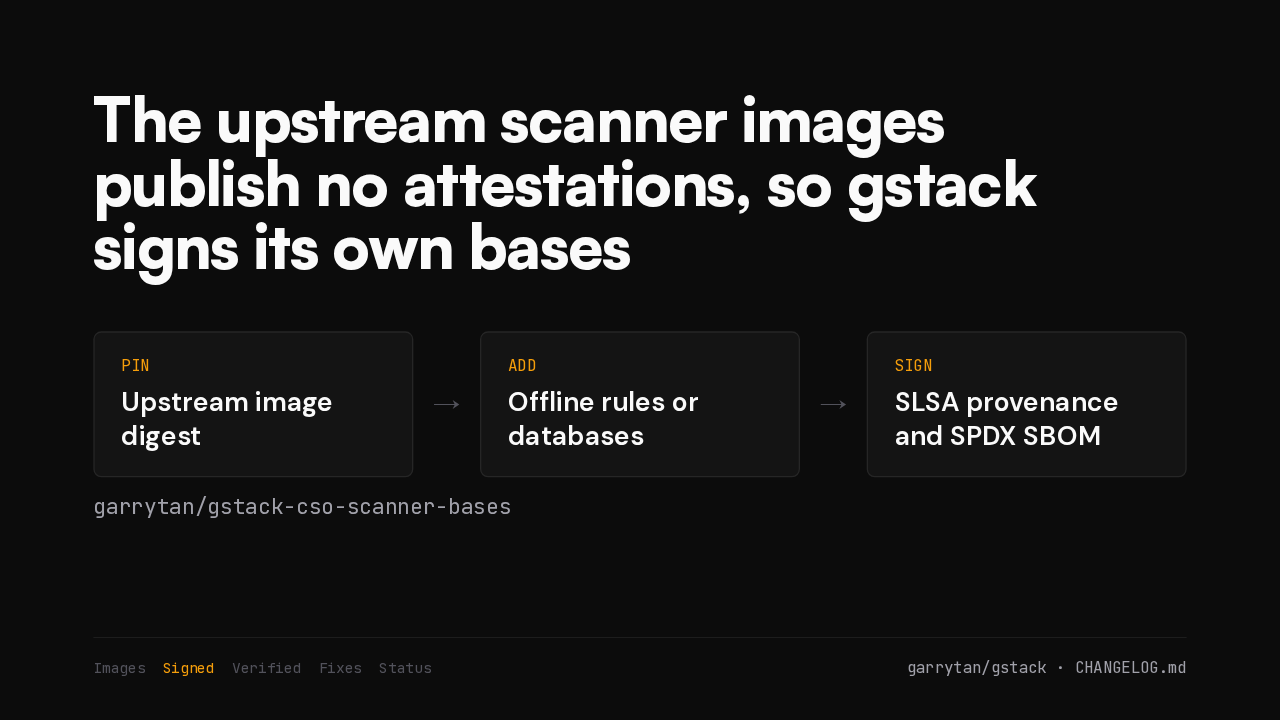
The upstream scanner images publish no attestations, so gstack signs its own bases
The upstream scanner images publish no attestations. So each base re-publishes a pinned upstream digest with its offline rules or databases added, then signs its provenance and a software bill of materials.
Re-verified
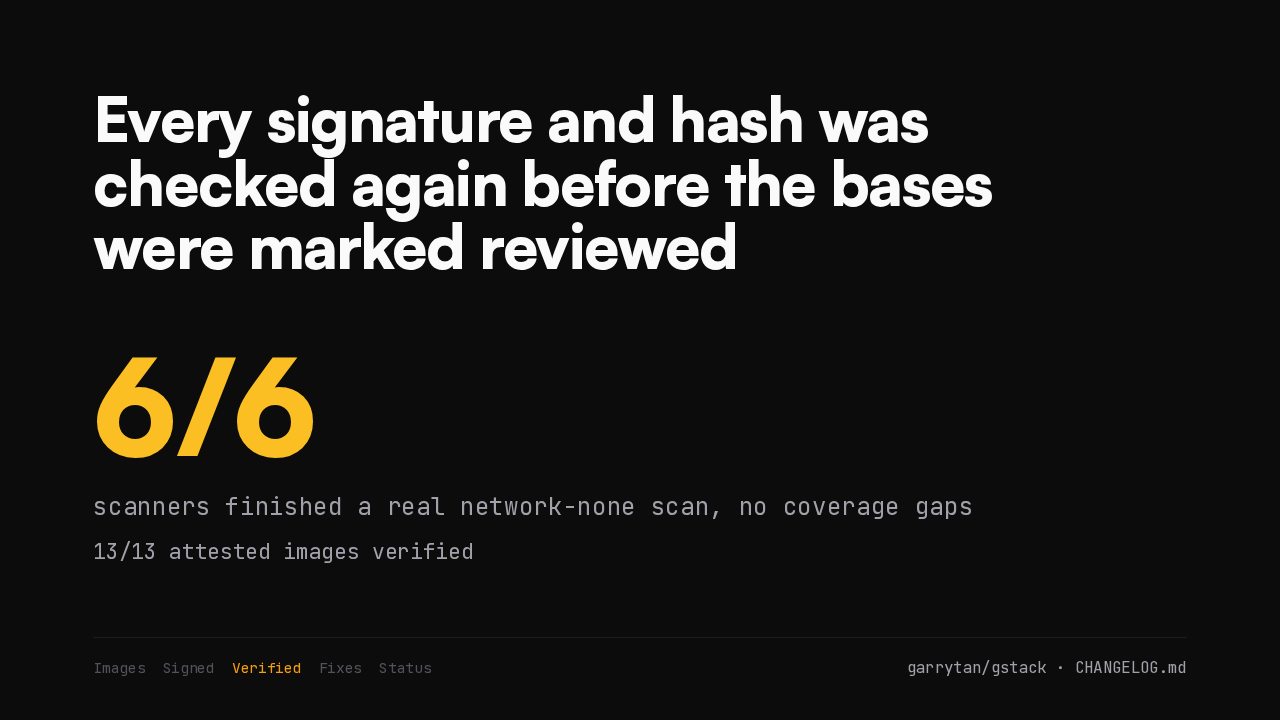
Every signature and hash was checked again before the bases were marked reviewed
scanners finished a real network-none scan, no coverage gaps
Every identity, digest and hash was re-checked independently before the bases were marked reviewed. On the published bases, all six scanners finished a real scan with networking off, with zero gaps in coverage.
Three fixes
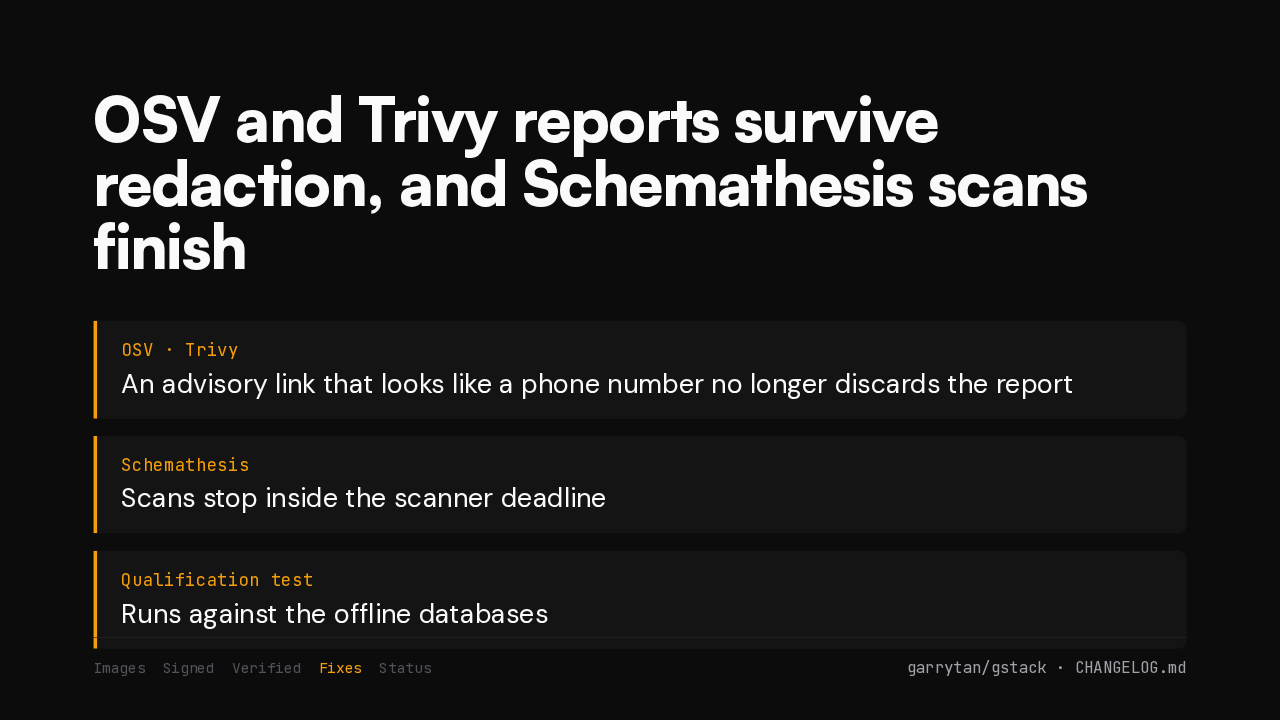
OSV and Trivy reports survive redaction, and Schemathesis scans finish
OSV and Trivy reports stop being thrown away when an advisory link looks like a phone number. Schemathesis scans now finish inside their deadline. And the scanner qualification test runs.
Not assessed yet
Until the scanner catalog merges, /cso scans still report not assessed
CHANGELOG.mdFull notes for 1.91.22.0Until the new scanner catalog merges into main, /cso scans still report not assessed. The changelog has the full notes for this release.