Repairs

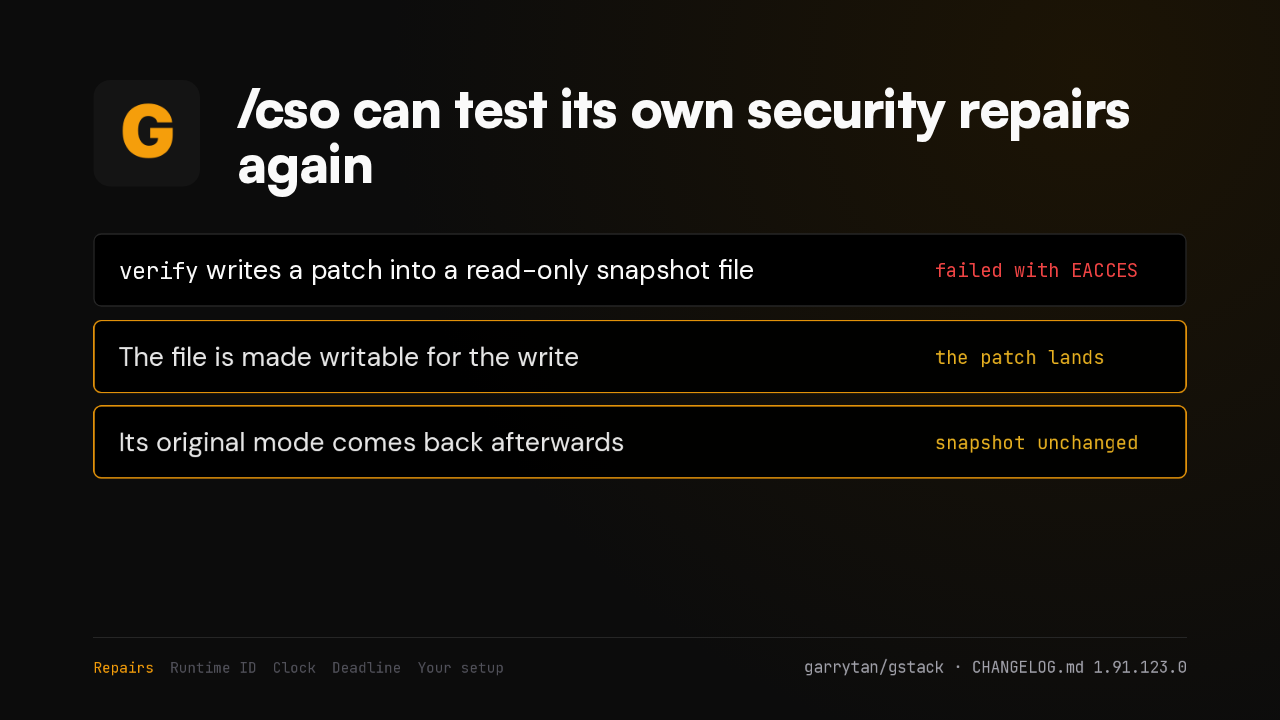
/cso can test its own security repairs again
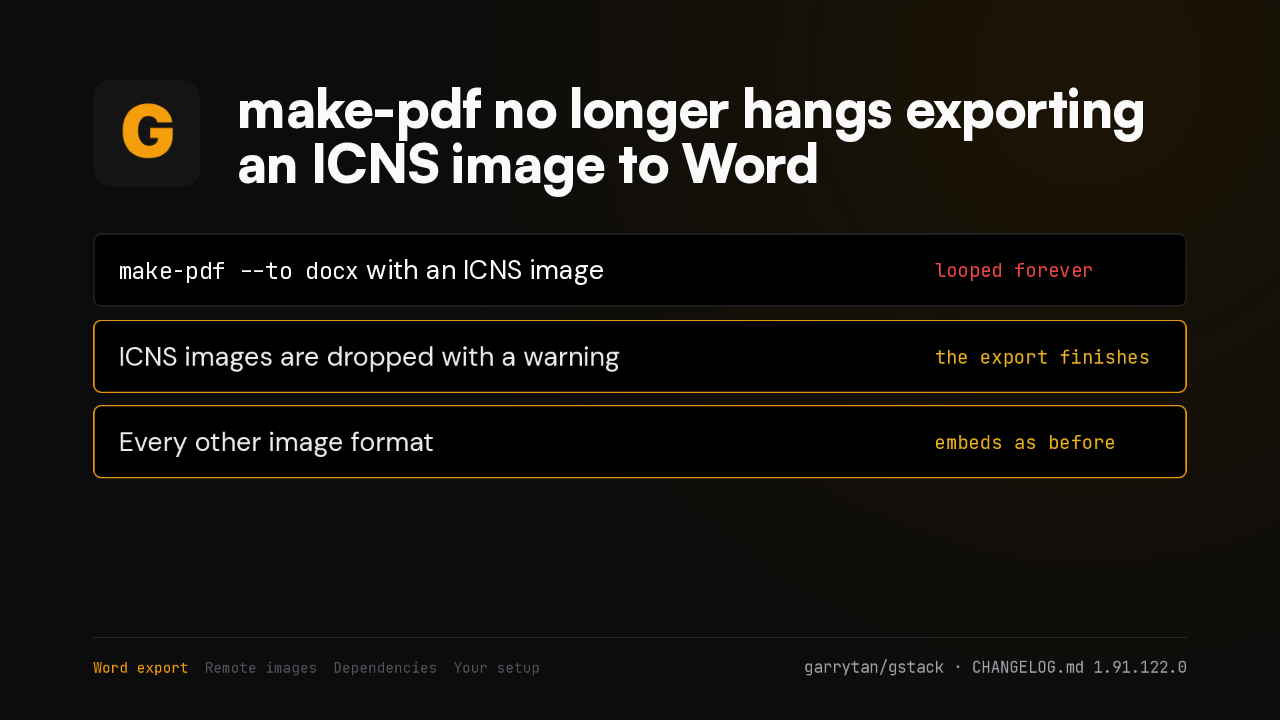
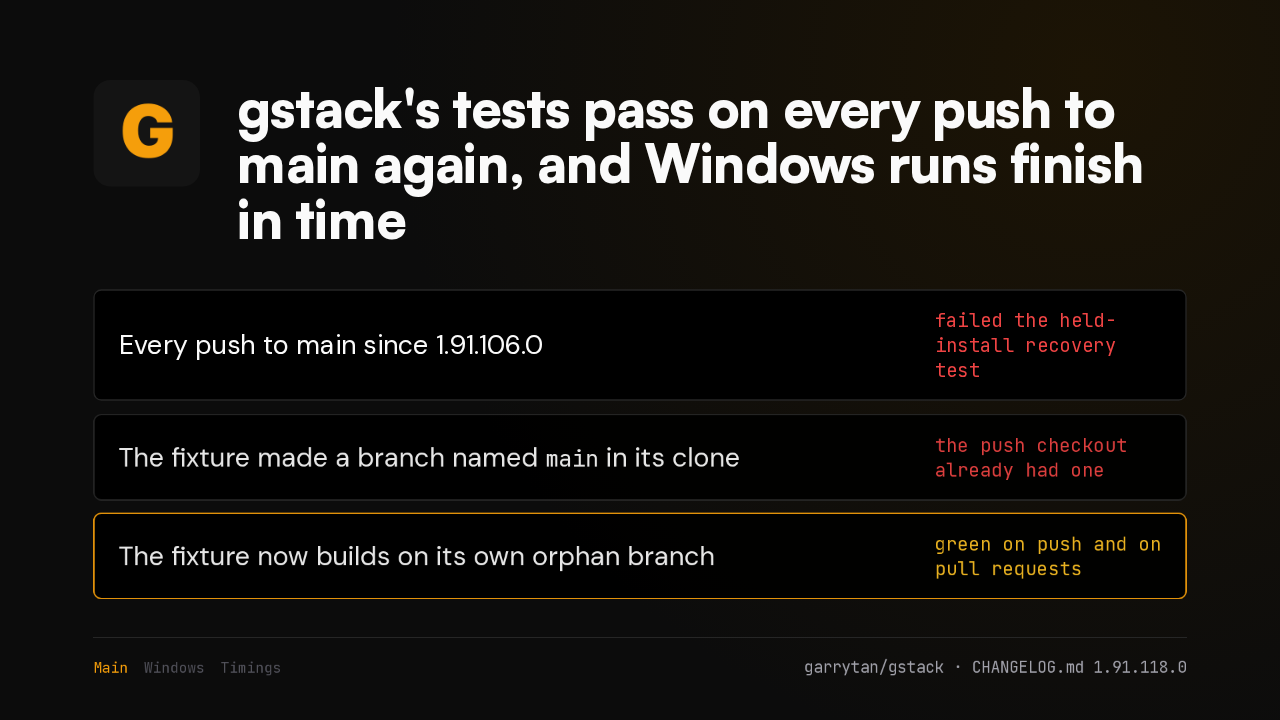
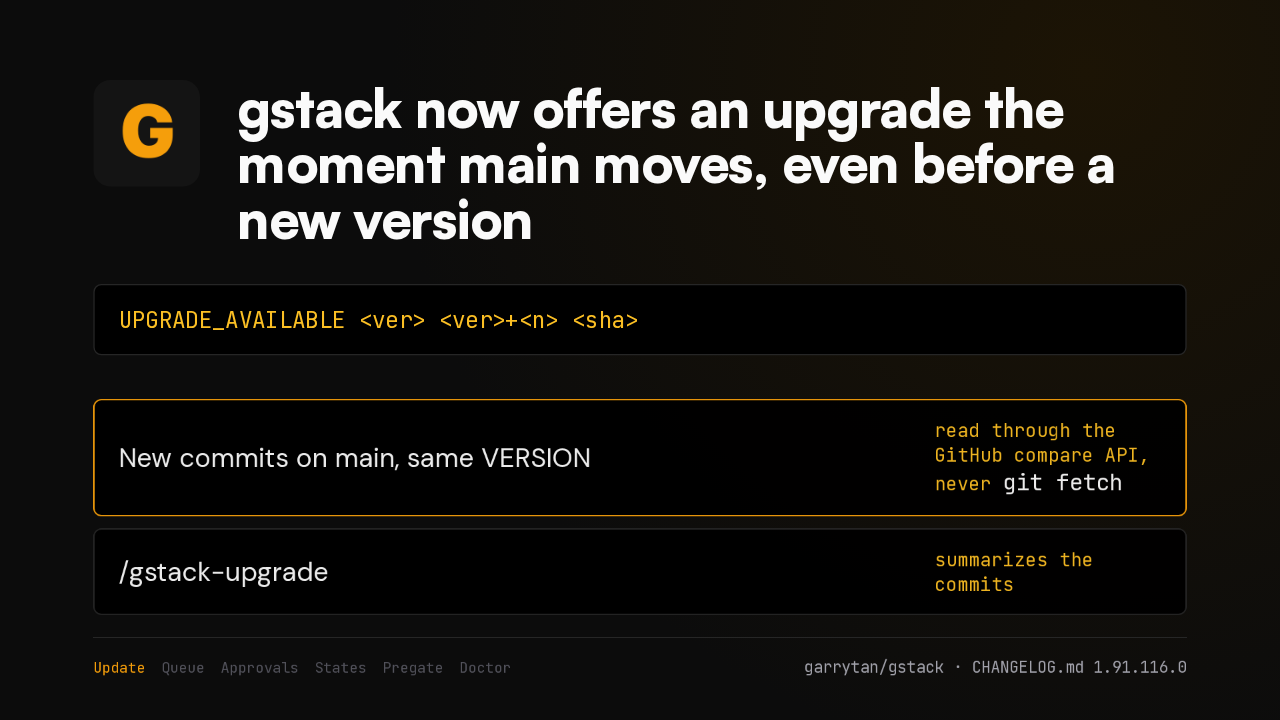
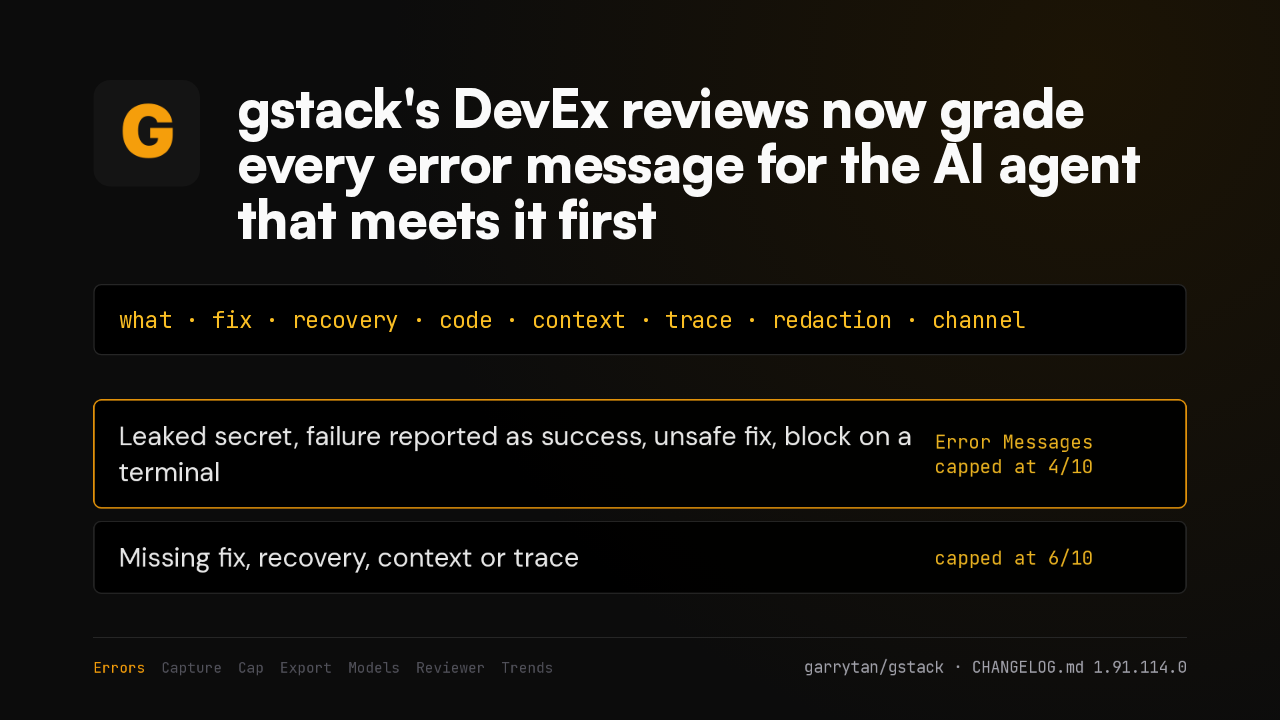
verify writes a patch into a read-only snapshot filefailed with EACCESgstack's /cso audit can test its own security repairs again. Patching a read-only snapshot file kept failing, so every repair check stalled. Now the helper makes the file writable, then restores its mode.
Runtime ID
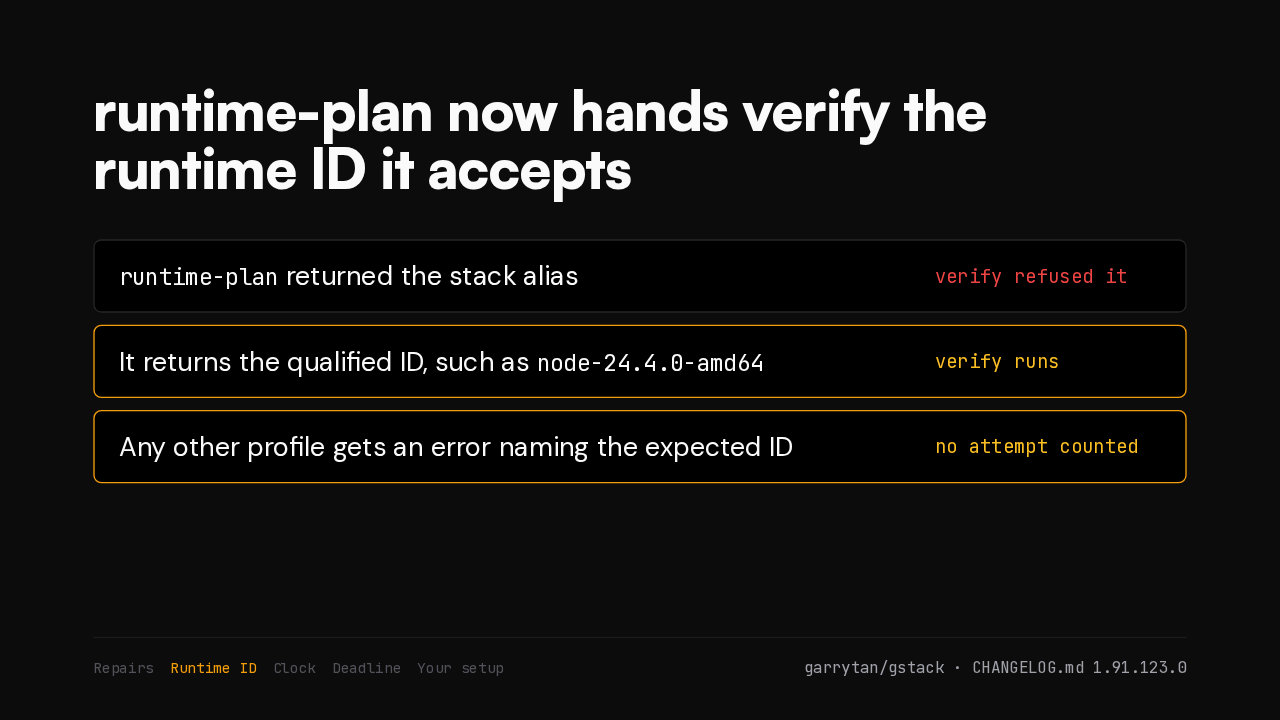
runtime-plan now hands verify the runtime ID it accepts
runtime-plan returned the stack aliasverify refused itnode-24.4.0-amd64verify runsA second bug stacked on top: the planning step handed out a stack name that verify refused. Now it returns the exact runtime ID. Any other profile gets an error naming the right one, before the attempt counts.
Clock
Every /cso helper reply now says how much time is left
Long /cso runs now finish on time. One run worked 25 minutes past its findings and was killed before its report was done. Now every helper reply carries the seconds left. The count ends a minute early, so finishing always has room.
Deadline
Under two minutes left, /cso stops and finishes
The skill now follows that clock. It starts only work that fits. Under two minutes, it stops waiting and finishes the report. If your own agent drives the helper, it gets the same count in every reply.
Your setup
Have you run a comprehensive /cso audit on your own repo yet?
CHANGELOG.md1.91.123.0 and 1.91.124.0, with their “If you…” notesBoth releases are in gstack's changelog. So, have you run a comprehensive /cso audit on your own repo yet?