CC Hub 0.9.8 fixes a high-severity Node.js flaw in request decompression
2 hours ago
CC Hub 0.9.8 is a security release. It fixes CVE-2026-111497, a high-severity flaw in how Node.js decodes Brotli, and the maintainers recommend every user upgrade as soon as possible. It also makes the cache ratios in the logs follow real prices, and fixes the user quota page for installs with many users.
Ask about this presentation
Chapters
Show transcriptHide transcript
CC Hub 0.9.8 is a security release. It fixes CVE-2026-111497, a high-severity flaw in how Node.js decodes Brotli, and the maintainers recommend every user upgrade as soon as possible. It also makes the cache ratios in the logs follow real prices, and fixes the user quota page for installs with many users.
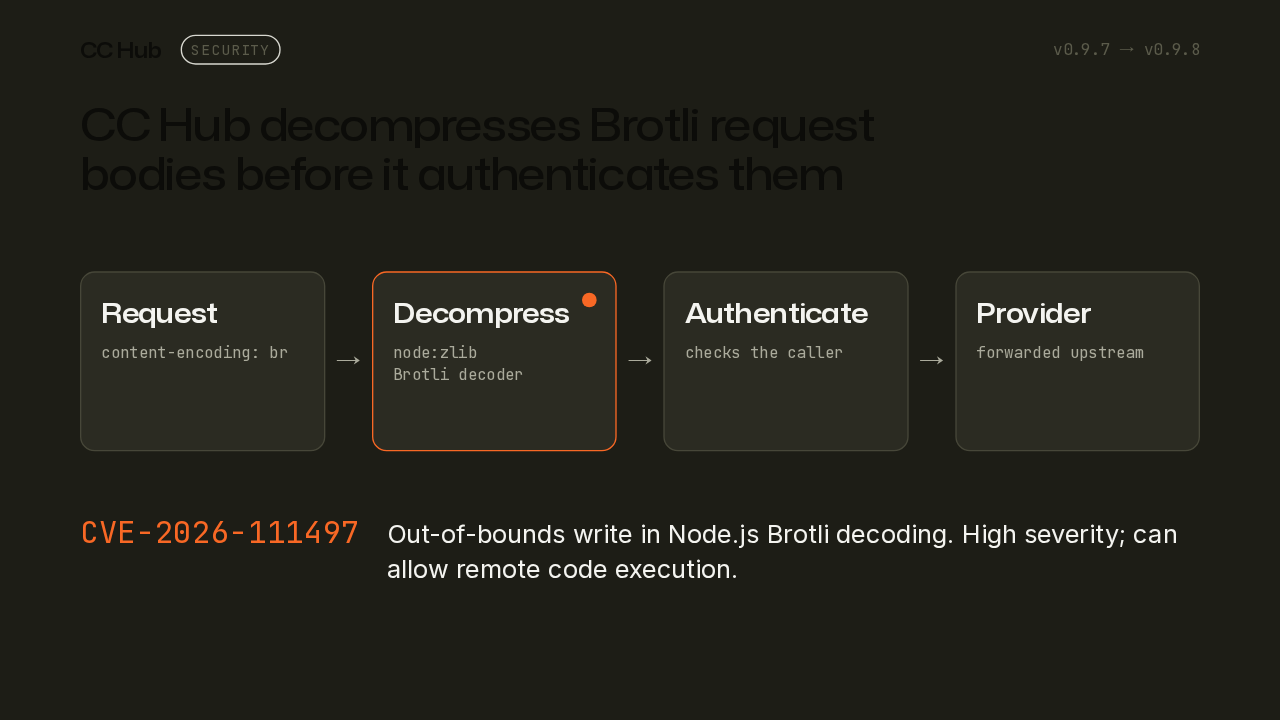
Here is why this flaw reaches CC Hub. When a request arrives with a Brotli-compressed body, CC Hub unpacks it first and checks who sent it afterwards. So the Node.js decoder handles that body before authentication runs. The bug is an out-of-bounds write in that Brotli decoder. It is rated high severity, and it can allow remote code execution.
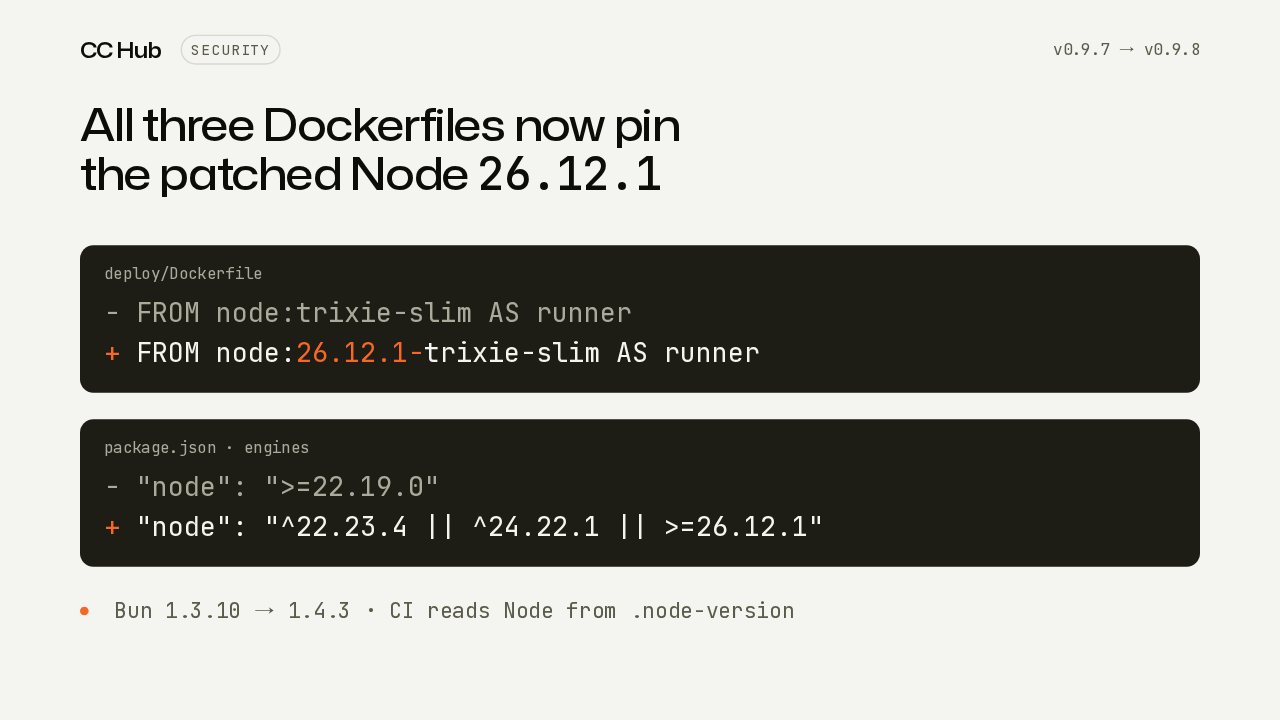
So the release pins the runtime. The production image used to follow a floating Node tag. Now all three Dockerfiles pin Node 26.12.1, so every image carries the fix. The engines field in the package file now accepts only patched Node releases. Bun moves to 1.4.3, and CI reads its Node version from one file.
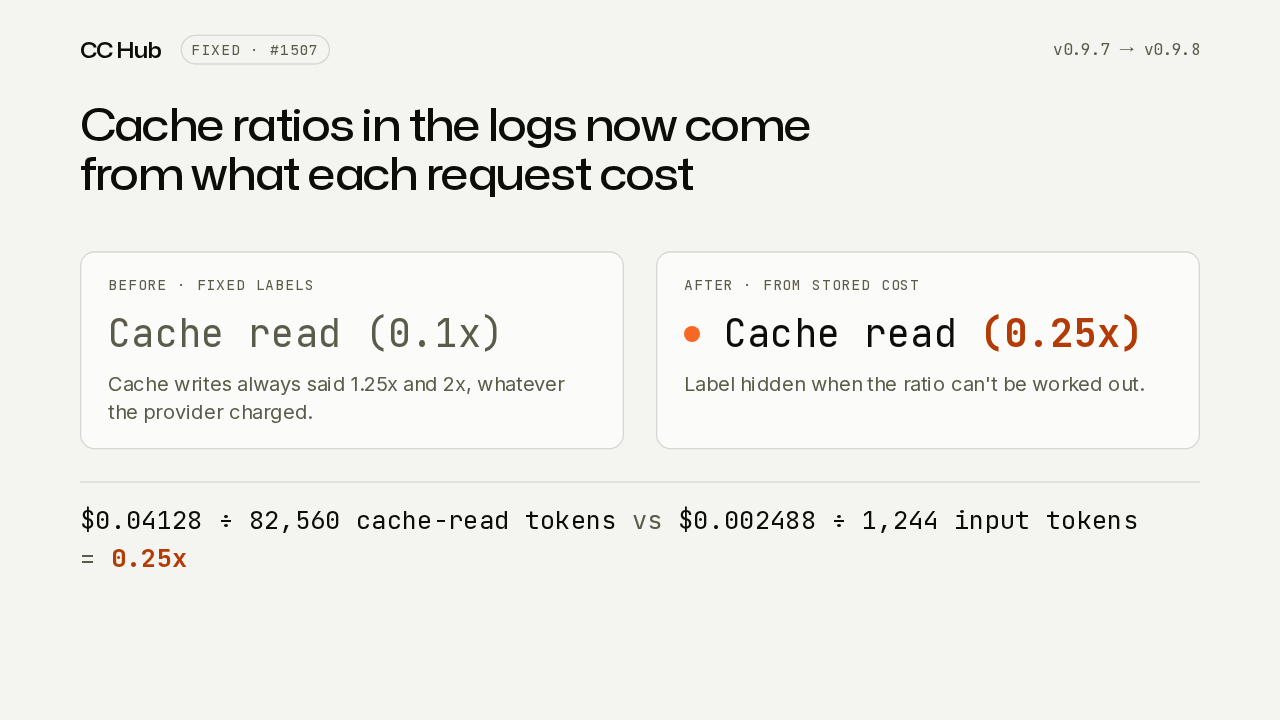
Next, the logs. Cache lines used to carry fixed labels: 1.25 times and 2 times for cache writes, 0.1 times for cache reads. Those are Anthropic's ratios, and other providers price cache tokens differently. Now CC Hub works the ratio out from the cost it stored for each request. Here a cached token cost a quarter of an input token, and the label says so.
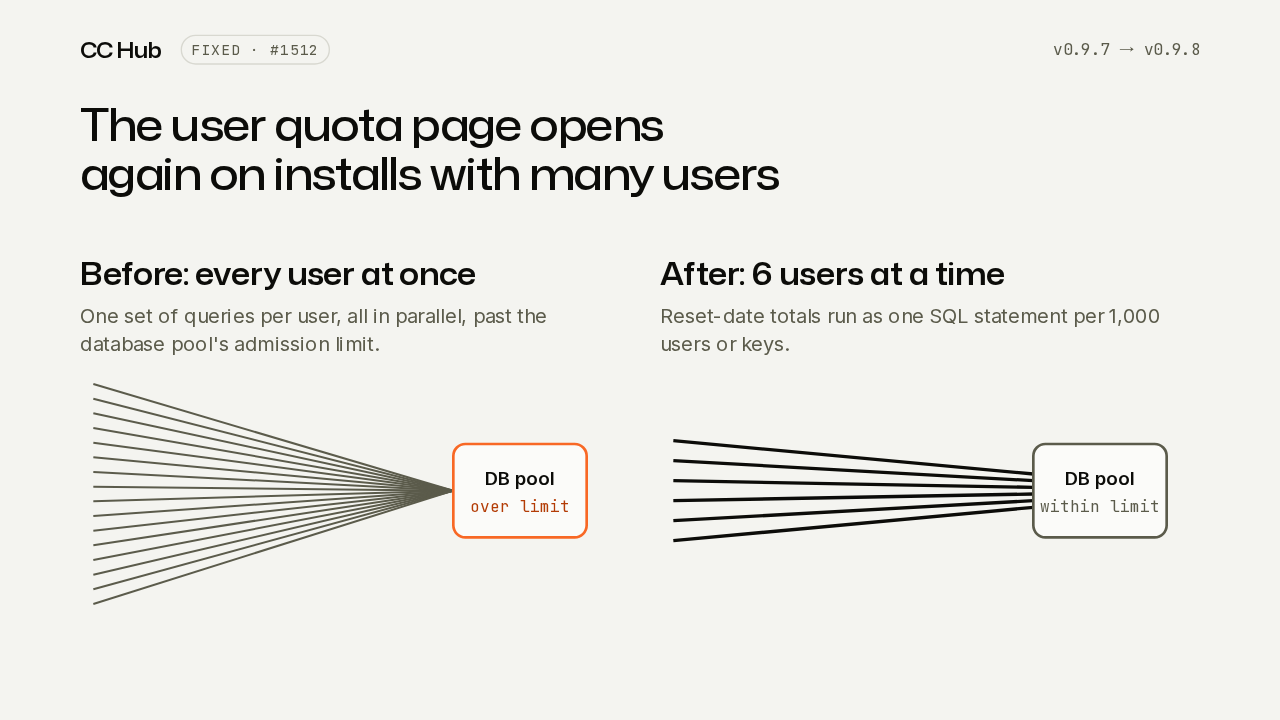
Large installs hit a different bug. The user quota page loaded usage for every user at once, all in parallel. With enough users, that went past what the database connection pool would admit, and the page failed to open. Now it works through six users at a time, and users with a cost reset date are totalled in one SQL statement instead of one query each.
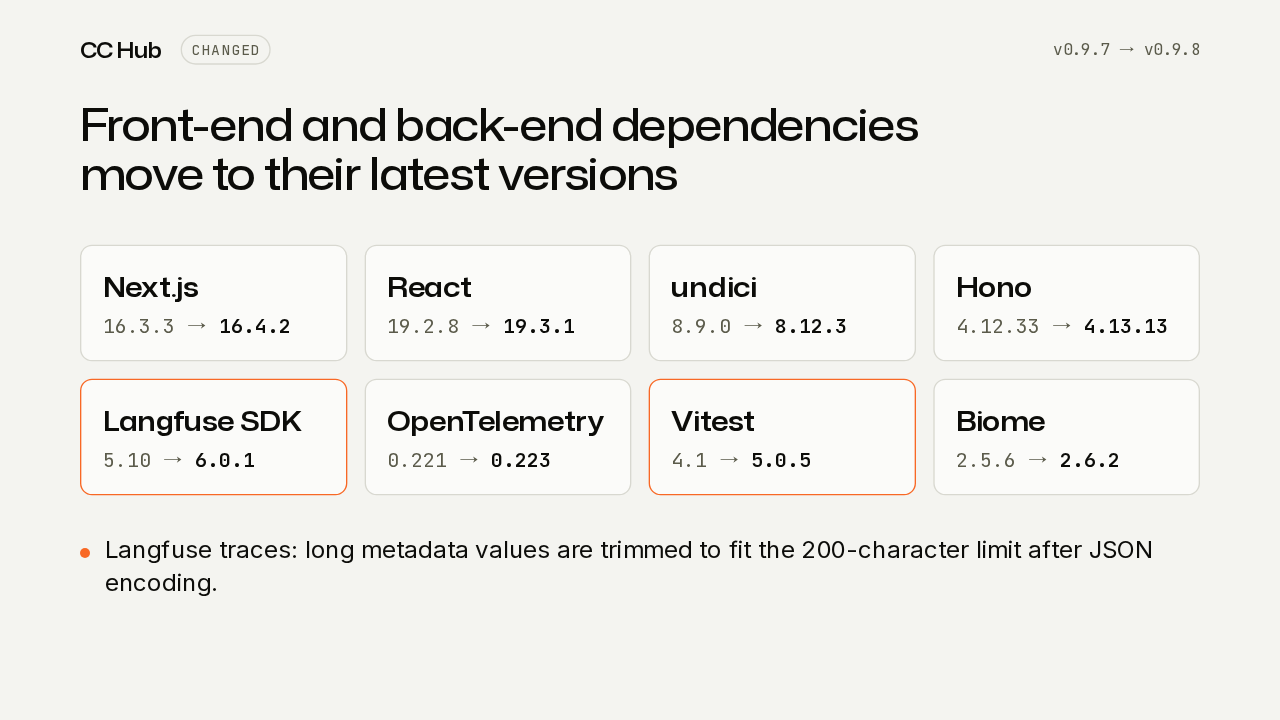
Every front-end and back-end dependency moves to its latest version. That includes Next.js 16.4, React 19.3, undici and Hono, and new major versions of the Langfuse SDK and Vitest. If you send traces to Langfuse, metadata values such as user and key names are now trimmed by their length after JSON encoding, so a value with escaped characters no longer runs past Langfuse's 200-character limit and gets dropped.
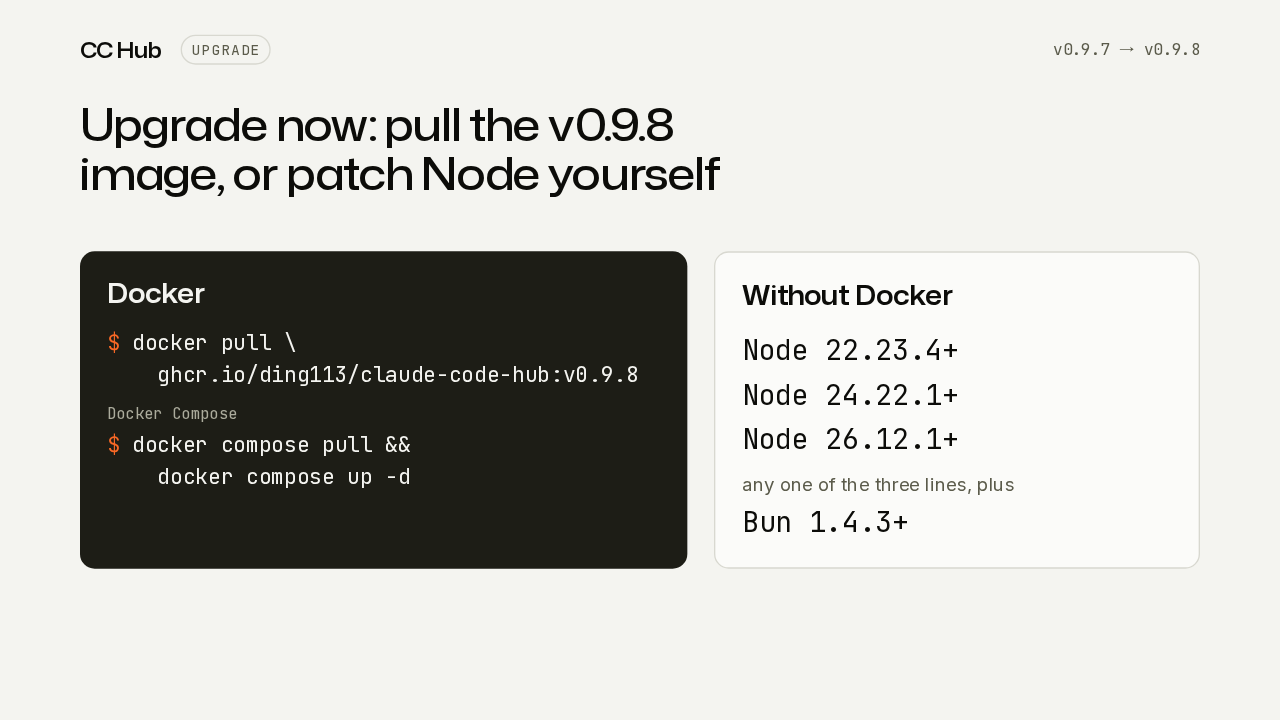
To upgrade with Docker, pull the v0.9.8 image, or with Docker Compose, pull and bring the stack back up. That image already runs Node 26.12.1. If you run CC Hub without Docker, upgrade Node to 22.23.4, 24.22.1, or 26.12.1 or newer, and Bun to 1.4.3 or newer.
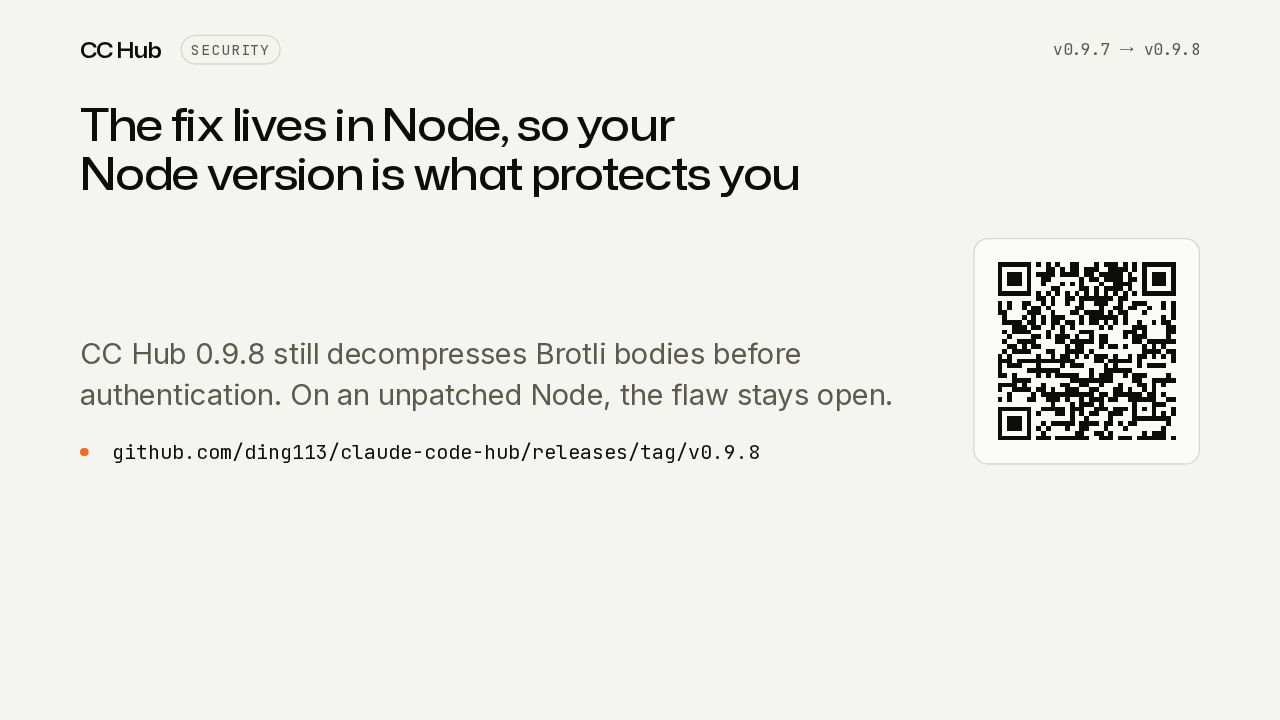
One limit to keep in mind. CC Hub still decompresses Brotli bodies before authentication, and the fix is in Node itself. So running 0.9.8 on an older Node leaves the flaw open. Pull the image or patch Node, and CC Hub 0.9.8 closes the high-severity Node.js flaw in request decompression. The full release notes are on GitHub.